Safari, Microsoft Edge exploits earn hackers $162k at Pwn2Own
Full article546 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The exploits, and money, are flying in Vancouver.
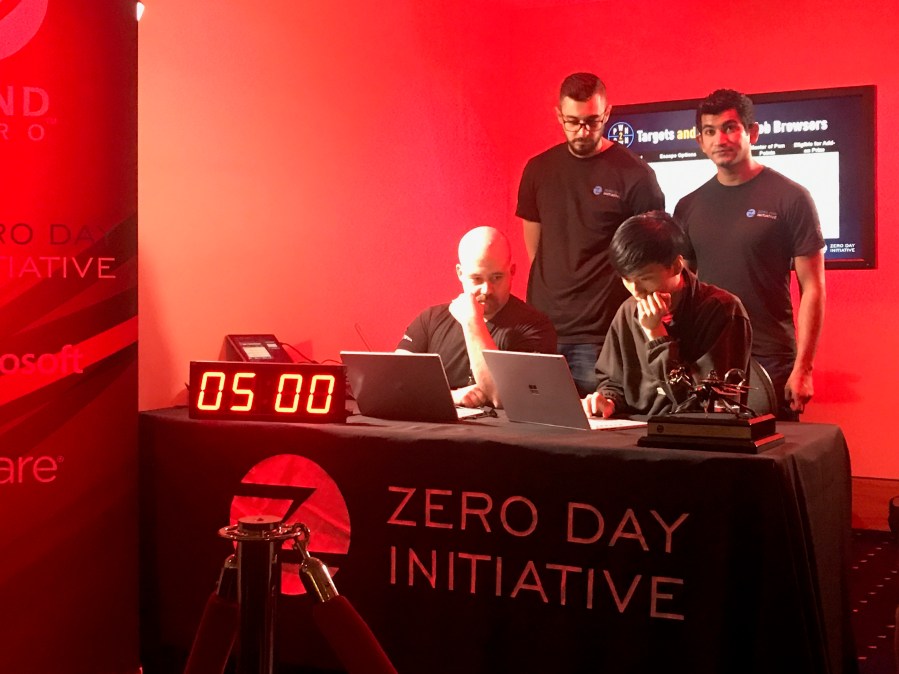
Zero-day exploits netted hackers $162,000 in total on Wednesday during the Pwn2Own contest in Vancouver, British Columbia.
Exploits targeting Apple Safari and Microsoft Edge web browsers were the highlight of Pwn2Own’s first day, a zero-day vulnerability hacking contest organized by Trend Micro’s Zero Day Initiative. Some of the best hackers in the world attended this year for a chunk of $2 million in prizes.
One of the biggest wins of the day belonged to Samuel Groß (saelo) who successfully completed a privilege escalation in macOS via Safari. He capped off his $65,000 payday with a bit of showmanship by signing the touchbar on a MacBook Pro:
Success! Samuel Groß (@5aelo) manages to pop calc and brings back his trademark touchbar finesse. Now off to the disclosure room for confirmation and vendor notification. pic.twitter.com/REQh1kHBjB
— Zero Day Initiative (@thezdi) March 14, 2018
Richard Zhu, a veteran of Pwn2Own, competed twice on Wednesday. He initially failed to pop macOS via Safari, but was paid an unspecified amount through Zero Day Initiative’s bug bounty program because the exploit ended up working after the timed portion.
Zhu completed the Microsoft Edge challenge on his third and final attempt.
After a win, the vulnerabilities and exploit techniques are disclosed to vendors that, along with a large crowd, watch up close as the software is attacked.
Zhu earned $80,000 from Pwn2Own contests last year. Samuel Groß was part of a team that won $28,000 last year.
Niklas Baumstark (_niklasb), a teammate of Groß’s, successfully targeted Oracle VirtualBox with a guest-to-host escape for $27,000.
Pwn2Own’s day two will see Zhu target Mozilla Firefox with a Windows kernel escalation of privilege for $50,000; Markus Gaasedelen, Nick Burnett, Patrick Biernat of Ret2 Systems, Inc. target Apple Safari for $65,000 and MWR Labs’ Alex Plaskett (AlaxJPlaskett), Georgi Geshev (munmap), Fabi Beterke (pwnfl4k3s) targeting Apple Safari with a sandbox escape worth $55,000.
Correction: The total amount of prizes given away was $162,000.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/pwn2own-exploits-apple-safari-microsoft-edge/