Apple releases, quickly pulls Rapid Security Response update for 0
Full article219 words · extracted from arstechnica.com · click to collapse
Yesterday, Apple published a new Rapid Security Response update for iOS 16, iPadOS 16, and macOS Ventura to patch yet another actively exploited WebKit code execution bug. But shortly after installation, users began having issues accessing certain websites, and Apple has apparently pulled the update to fix the problem.
According to MacRumors, affected sites include Facebook, Instagram, WhatsApp, and Zoom, which began showing warning messages about not being supported following the update.
Luckily for anyone who has installed it, Rapid Security Response updates can be removed just as quickly as they were installed; on iOS, navigate to the About page in the Settings app, tap on your iOS version, and then tap “Remove Security Response.”
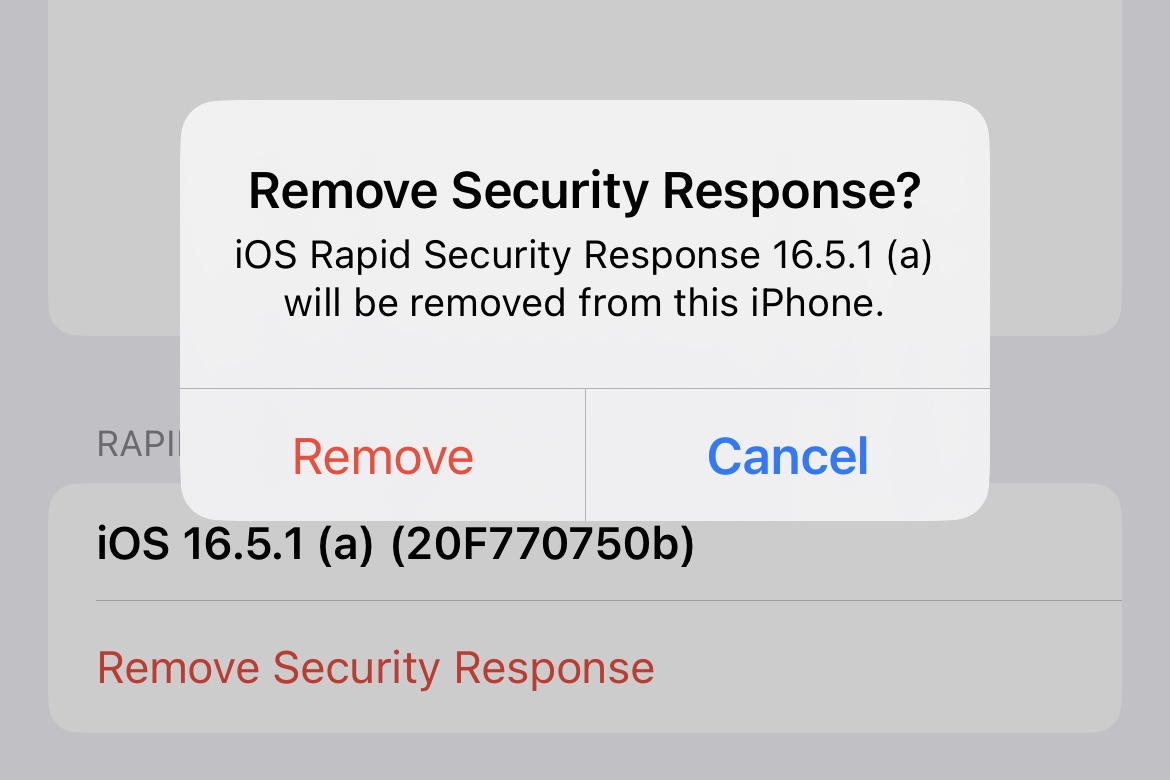
Removing a Rapid Security Response update on an iPhone running iOS 16.5.1. Credit: Andrew Cunningham
The benefit of Rapid Security Response updates is that they’re small in size and quick to install. The updates Apple has released so far have required a restart on my devices, but total downtime was much less than it was for a typical software update. This is because Apple has stored many Safari and WebKit components outside of the main Signed System Volume (SSV), a tamper-proof read-only volume for most system files that must be mounted separately, patched, and re-sealed every time most system updates are installed.
Text extracted automatically; images, tables and formatting may be missing. Original: https://arstechnica.com/security/2023/07/apple-releases-quickly-pulls-rapid-security-response-update-for-0-day-webkit-bug/