Detailed data on employees of U.S. national security lab leak online
Full article1,104 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The hacking group SiegedSed released personal data on thousands of employees at the Idaho National Laboratory, the nuclear research lab.
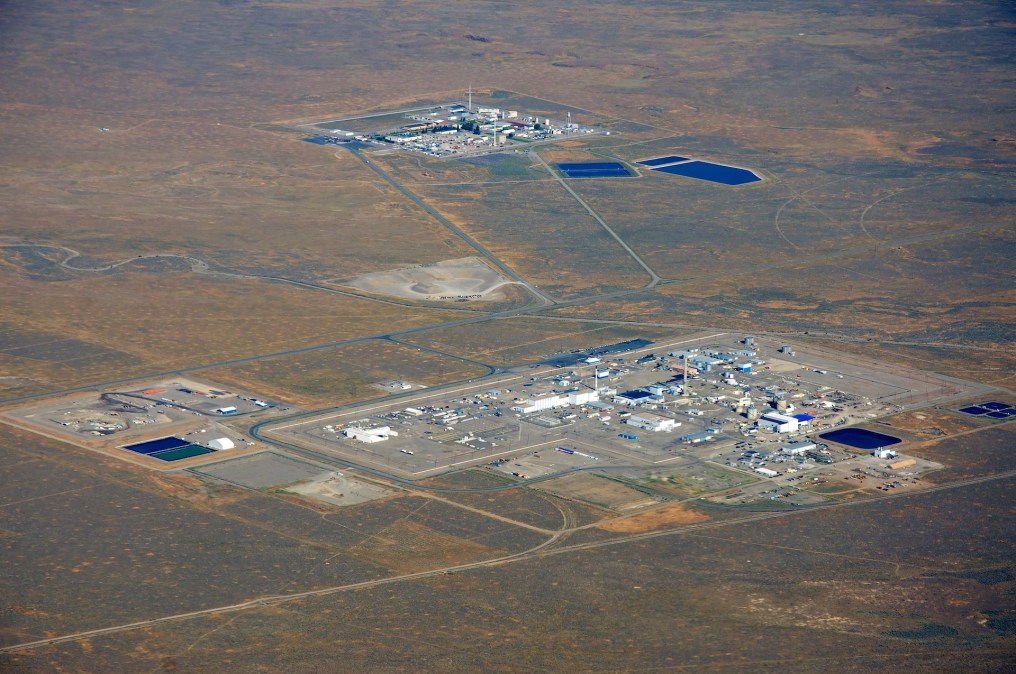
A cybercrime group that has engaged in politically motivated attacks breached a human resources application belonging to Idaho National Laboratory, claiming in a post to Telegram on Sunday that it had obtained detailed information on employees working at the nuclear research lab.
The hacking group SiegedSec said it had accessed “hundreds of thousands of user, employee, and citizen data,” including full names, social security numbers, bank account information, and addresses. The group posted a sample of the leaked data, but CyberScoop could not confirm whether SiegedSec is in possession of the much larger data set it claims to have stolen.
An INL spokesperson, Lori McNamara, confirmed that the breach had taken place but said the lab is still investigating the extent. “Earlier this morning, Idaho National Laboratory determined that it was the target of a cybersecurity data breach, affecting the servers supporting its Oracle HCM system, which supports its Human Resources applications. INL has taken immediate action to protect employee data,” McNamara said.
The group has not said why it targeted INL, but the breach presents serious national security concerns. The scientists at INL work on some of the United States’ most sensitive national security programs, including protecting critical infrastructure like the U.S. power grid from cyber and physical attacks. Personal data such as detailed employee and banking information would represent a treasure trove for foreign intelligence agencies looking to penetrate the lab.
INL has been in touch with the FBI and the Cybersecurity and Infrastructure Security Agency to investigate the extent of the impact, the spokesperson said. The FBI and Oracle did not respond to request for comment before publication. CISA referred a request for comment to INL.
Idaho National Laboratory operates under the Department of Energy and is one of 17 labs that serve as the United States’s research and development test beds. INL is the premier lab for nuclear energy, but also focuses on energy security, reliability and other national security issues, such as cybersecurity.
A sample of the leaked information viewed by CyberScoop includes social security numbers, health care information, bank account and routing numbers, types of accounts, and marital status, among other things. One file includes a detailed list of recent terminations and a brief reason for the termination. Another file that shows active employees’ social security numbers includes more than 6000 lines. As of October 2022, INL said it had around 5,500 employees .
Another file containing detailed employee data has just over 58,000 lines of data that span current, retired and former employees.
The date of some of the information in the files posted by SiegedSec show updates as recent as October 31, 2023. Some of the screenshots show additional categories of information beyond what was included in the sample, indicating that there may be more data pilfered than can be determined from the sample.
It’s unclear how SiegedSec infiltrated the HR application or how the group was able to exfiltrate such a large quantity of data across a wide variety of personal identifiable information.
Oracle describes the Human Capital Management product that was targeted as a “complete cloud solution that connects every human resource process — and every person — across your enterprise.”
This is not the first time the national laboratories have been targeted by hackers. U.S. national laboratories work on everything from nuclear weapons to renewable technologies — and everything in between — and have been the target of multiple state-backed hacking operations. Earlier this year, Russian hackers targeted the Brookhaven, Argonne, and Lawrence Livermore National Laboratories, Reuters reported.
SiegedSec, the group that has claimed responsibility for the breach, has a history of carrying out politically motivated cyberattacks, including claims of breaching of NATO systems. The group mostly recently targeted NATO in October, when it alleged to have stolen roughly 3,000 documents.
The group has previously claimed that they are less interested in hacktivist-type attacks and instead consider themselves “more blackhat than activists,” as the group previously told CyberScoop. They have previously carried out attacks against U.S. states that limit access to gender-affirming healthcare and abortion. More recently, the group has claimed to attack Israeli infrastructure.
More Scoops
Plankey vows to boot China from U.S. supply chain, advocate for CISA budget
But Trump’s pick to lead CISA sidestepped questions about alleged past or future election manipulation claims.
Contract lapse leaves critical infrastructure cybersecurity sensor data unanalyzed at national lab
White House needs to urgently fix nation’s approach to protecting critical infrastructure, group says
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/idaho-national-laboratory-siegedsec/