Industrial networking manufacturer Moxa reports 'critical' router bugs
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2024-9138 | Moxa’s cellular routers, secure routers, and network security appliances are affected by a high-severity vulnerability, CVE-2024-9138. Moxa’s cellular routers, secure routers, and network security appliances are affected by a high-severity vulnerability, CVE-2024-9138. This vulnerability involves hard-coded credentials, enabling an authenticated user to escalate privileges and gain root-level access to the system, posing a significant security risk. NVD description · AI analysis pending | 8.6 | 1% | — | — | ||
| CVE-2024-9140 | Moxa’s cellular routers, secure routers, and network security appliances are affected by a critical vulnerability, CVE-2024-9140. Moxa’s cellular routers, secure routers, and network security appliances are affected by a critical vulnerability, CVE-2024-9140. This vulnerability allows OS command injection due to improperly restricted commands, potentially enabling attackers to execute arbitrary code. This poses a significant risk to the system’s security and functionality. NVD description · AI analysis pending | 9.3 | 2% | — | — |
Full article607 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Moxa says the flaws can be used to bypass user authentication, escalate privileges and gain root access to devices.
Listen to this article
0:00
Learn more.
Firmware in cellular routers, secure routers and network security appliances made by Moxa are vulnerable to a pair of high severity bugs that can escalate privileges for an attacker, give root-level access or allow for unauthorized execution of commands.
In a pair of CVEs published Jan. 3, Moxa called the flaws “critical” and warned they “pose a significant security risk” to affected users.
The first (CVE-2024-9138) requires a user to be authenticated and takes advantage of hardcoded credentials in the firmware of 10 different Moxa products to gain root access. The second (CVE-2024-9140) uses special characters to bypass input restrictions and conduct OS command injection attacks for firmware used in 7 Moxa products and can be exploited remotely by an unauthenticated user. The vulnerabilities were rated 8.6 and 9.8 on the Common Vulnerability Scoring System (CVSS) for severity.
“Immediate action is strongly recommended to prevent potential exploitation and mitigate these risks,” the company said in a security advisory.
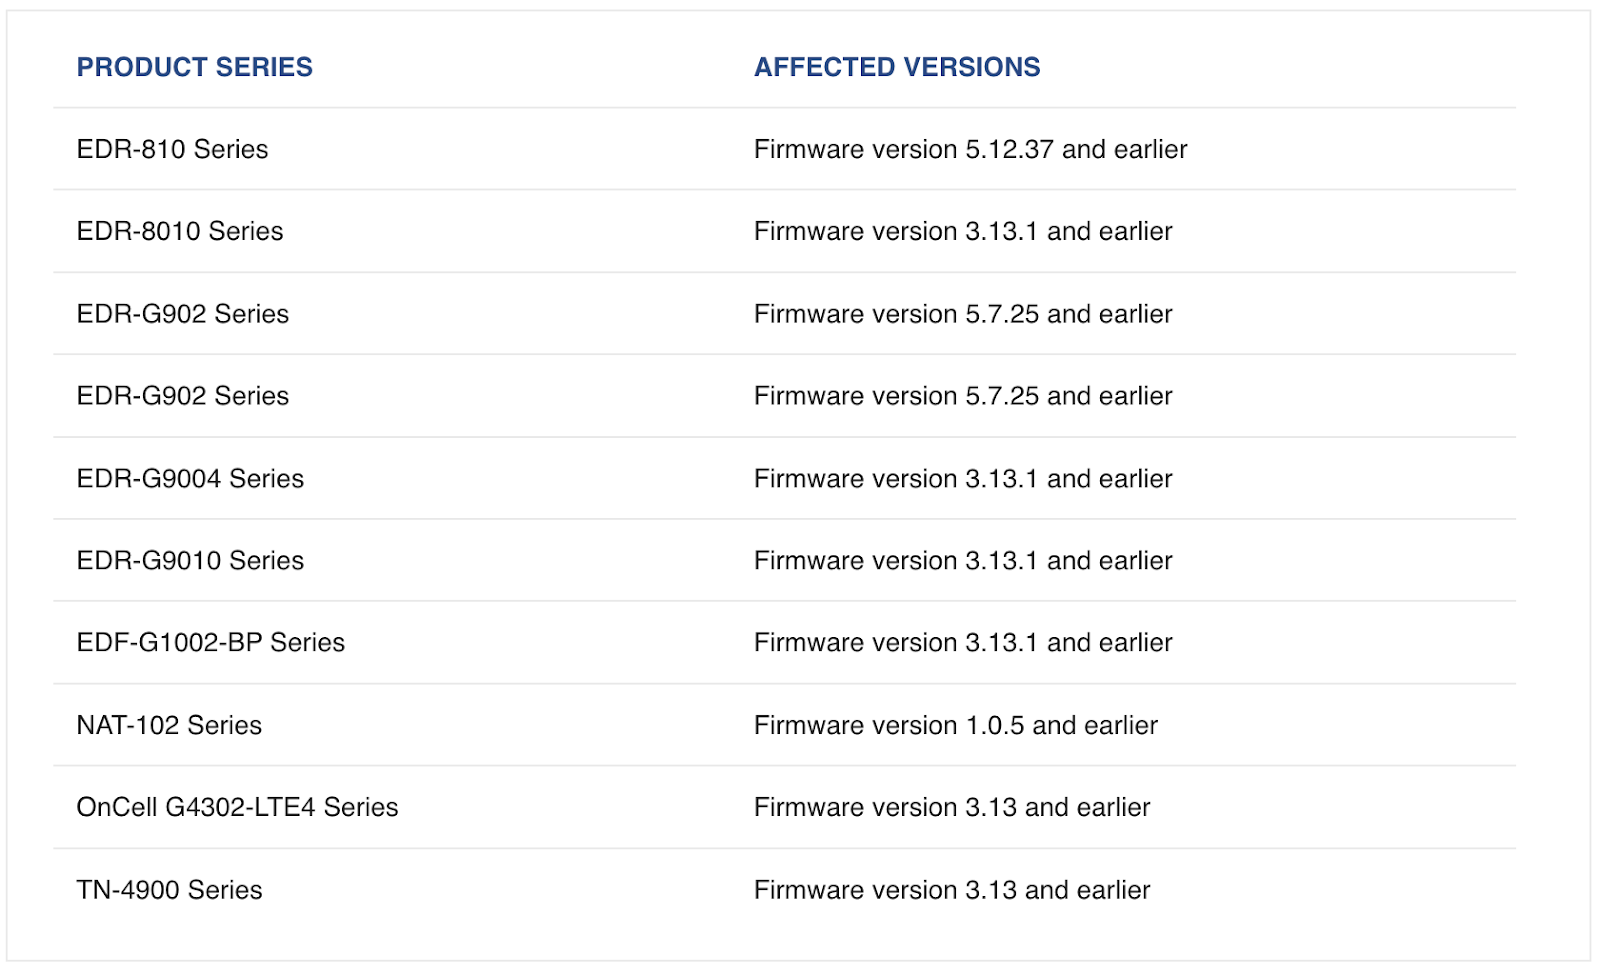
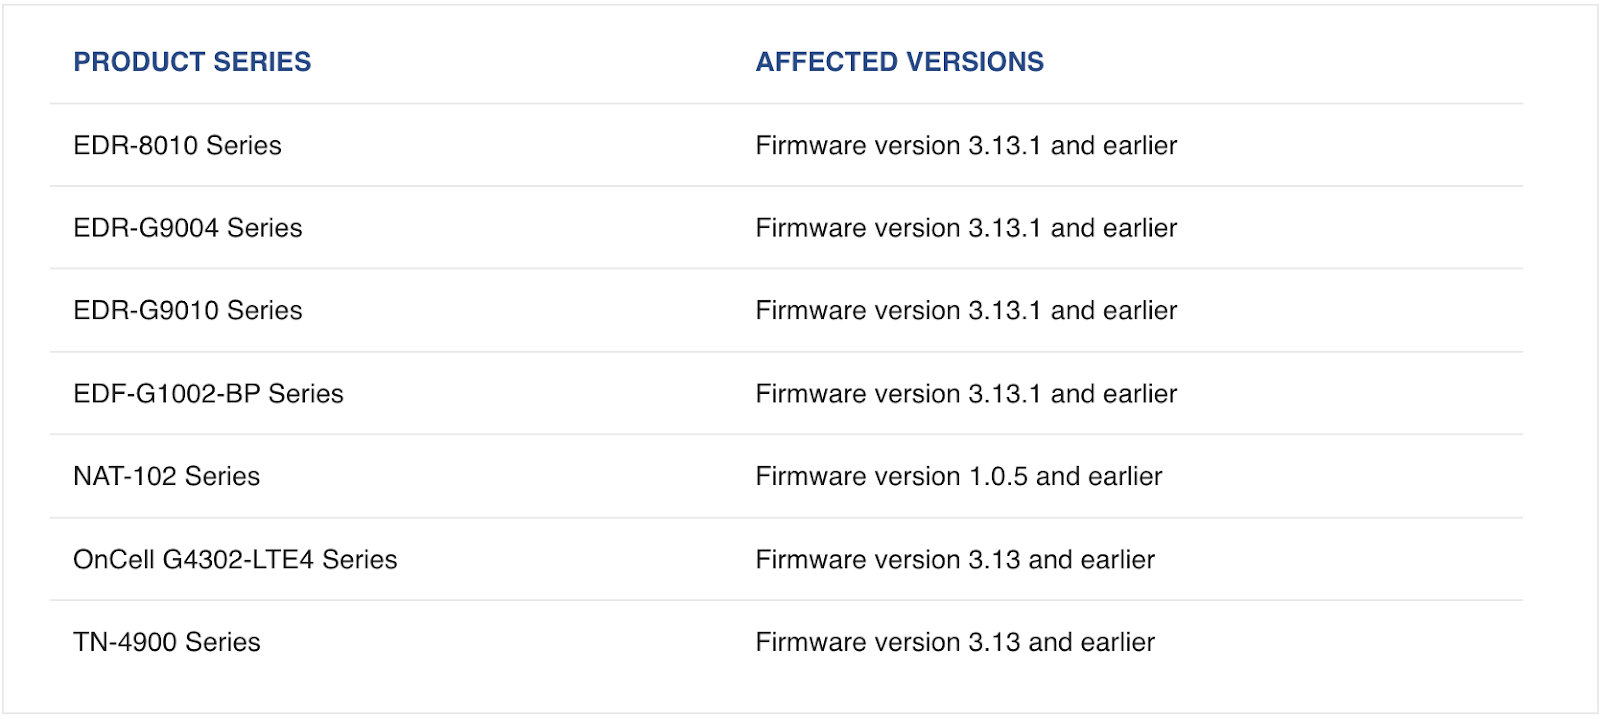
Moxa has already developed software patches for many of the affected products. However, some, like NAT-102 Series secure routers, OnCell G4302-LTE4 Series cellular routers and TN-4900 Series M12 routers, currently lack publicly-available patches for affected firmware or require users to reach out to Moxa for further technical support.
In the event patching is not possible, the company advises users to minimize network exposure and ensure the affected devices aren’t connected to the internet, limit SSH access to trusted IP addresses, and implement intrusion detection systems to monitor for malicious traffic attempting to exploit the vulnerabilities.
Moxa thanked security researcher Lars Haulin for initially reporting the vulnerabilities.
Moxa bills itself as an industrial networking, communications and automation manufacturer. According to the company’s website, their products are used by some of the largest global train builders, wind turbine builders, semiconductor manufacturers, cloud service providers and oil and gas companies in the world.
They list Thailand’s Provincial Electricity Authority, the City of Lancaster, California, software vendor GreenPowerMonitor, consulting firm KPMG and others as users of Moxa products on their customer successes page.
You can read the full security advisory on Moxa’s website.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Jail time for Maine child in 764 marks turning point in federal law enforcement
Dogged Russia-based botnet dismantled after 23-year run
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/industrial-networking-manufacturer-moxa-reports-critical-router-bugs/