Stealing User’s Password with Free Online Forms
Full article324 words · extracted from securelist.com · click to collapse


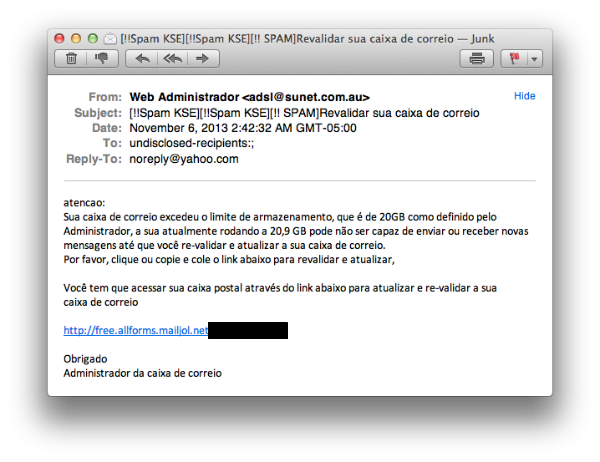
I just received a spam e-mail in Portuguese stating that my mailbox had exceeded its maximum storage.
Translation: Attention! Your email box has exceeded the 20Gb storage limit set by the Administrator. At this moment you are using 20,9Gb and can’t send or receive new messages unless you revalidate your email inbox.
Please click on or copy the link below to revalidate and to update it.
You have to access your email box via the link below to update and revalidate your email inbox.
Thank you,
Email Administrator.
It’s classic phishing, abusing Free online forms. If you click, you will see the next set of messages:
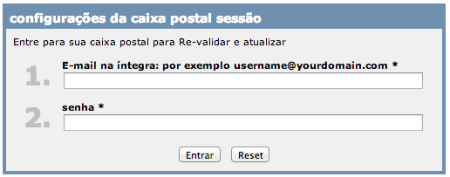

(This Captcha warning message is not in Portuguese anymore but in French)
Why do such simple attacks still work? Well, in Latin America, in the good sense of this word, people are very naïve. It’s clear that attacks do not need to be complex to be effective. Simple tricks used 10-15 years ago are still functioning for cybercriminals. And as you can see, there is no need to clone an original Web site, so any rookie cybercriminal is able to use such methods to steal users’ information.
I already reported the form as fraudulent and hope it will be taken down quickly.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/stealing-users-password-with-free-online-forms-2/57215/