Senate bill hopes to sort out supply-chain cybersecurity risks, prevent next Kaspersky drama
Full article846 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
A new bipartisan Senate bill tries to get to the bottom of supply chain risk by setting up a federal acquisition council to get national-security and civilian agencies on the same page.
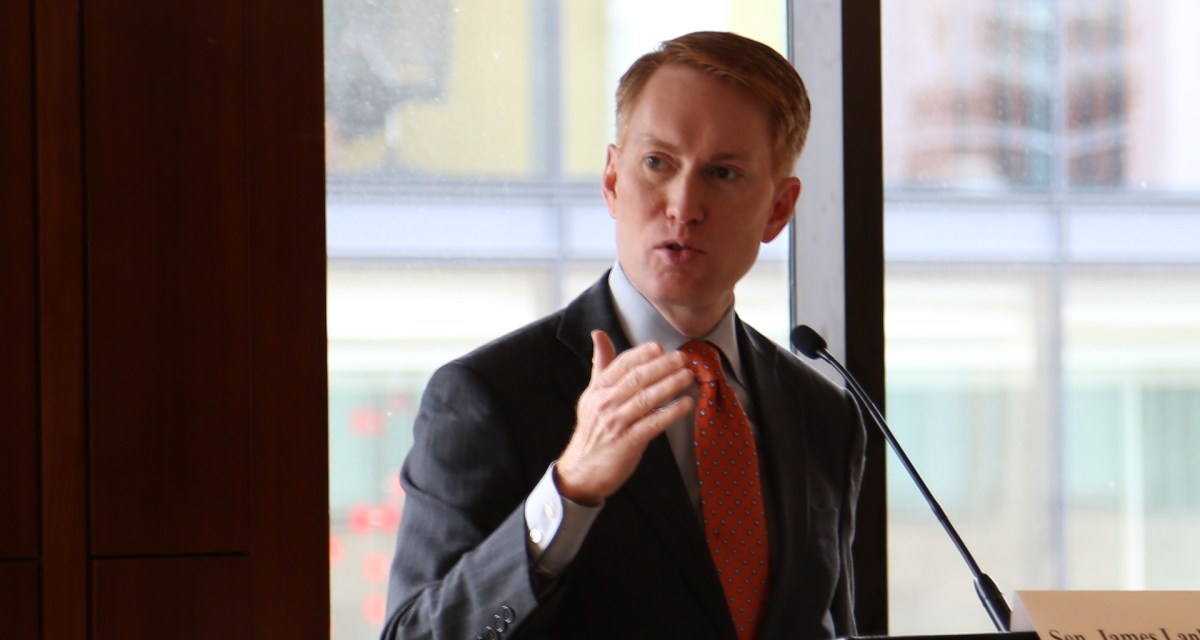
A new bipartisan Senate bill would try to get to the bottom of supply chain risks by setting up a federal acquisition council that would include representatives of the intelligence community and Defense Department.
The goal of the bill is to increase policy coordination between agencies so that the government can avoid buying technology that is bugged by foreign spies.
The “Federal Acquisition Supply Chain Security Act” was introduced Tuesday by Sens. James Lankford, R-Okla., and Claire McCaskill, D-Mo. It tasks agencies across the government with creating a strategy to address supply chain threats embedded in federally procured technology systems. If a tainted software or hardware component enters an agency’s supply chain, experts say it could be used for espionage or to carry out a cyberattack.
The announcement comes after a year in which U.S. officials have repeatedly grappled with national security concerns surrounding Moscow-based antivirus vendor Kaspersky Lab. Lawmakers claim that Kaspersky could be coopted by Russian intelligence to spy on specific users. But the company has consistently denied all wrongdoing.
In practice, the bill intends to bridge “the information gap between the intelligence community, the Department of Defense, and the rest of the government on technology vulnerabilities and characteristics that could jeopardize our national security,” the senators’ offices said in a prepared statement. An Office of Management and Budget official would chair the inter-agency council, which would issue guidance on IT threats.
The bill is the latest attempt to legislate the supply-chain challenge. On Monday, the Senate passed a defense bill that would nix a deal between the Trump administration and Chinese smartphone maker ZTE, another company accused of enabling espionage. Last year’s defense bill included a governmentwide ban on using software made by Kaspersky. That ban, however, has been difficult to enforce given how deeply embedded the relevant coding is in U.S. technology, the Daily Beast reported.
With acquisition policy emanating from multiple agencies, Lankford and McCaskill say more clarity on acquisition policy is needed.
“We can’t simply respond to supply chain threats piecemeal, we’ve got to have a system in place to assess these risks across the government,” McCaskill said in a statement.
Under the bill, the council would decide whether one agency’s ban on a company’s products should apply to other agencies. The Department of Homeland Security has exercised authority over civilian agencies on this issue, as it did last year when it directed agencies to remove any Kaspersky gear from their networks.
You can read the full bill below:
[documentcloud url=”http://www.documentcloud.org/documents/4524038-FASCSA.html” responsive=true]
More Scoops
Congressional leaders want an executive branch strategy on China 6G, tech supply chain
In an exclusive, Rep. Raja Krishnamoorthi, D-Ill., told CyberScoop that policymakers must learn from past mistakes around 5G.
Senators take another swing at vulnerability disclosure policy bill for federal contractors
Vulnerability disclosure policy bill for federal contractors clears Senate panel
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Election official says Tina Peters would be consultant, won’t have access to election systems
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/senate-bill-hopes-sort-supply-chain-cybersecurity-risks-prevent-next-kaspersky-drama/