A cyber-espionage effort against Tibetan leaders leveraged known Android, iOS vulnerabilities
Full article838 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Citizen Lab says the spyware campaign involved attackers who posed as journalists, Amnesty International researchers, nongovernmental organization workers through May 2019.
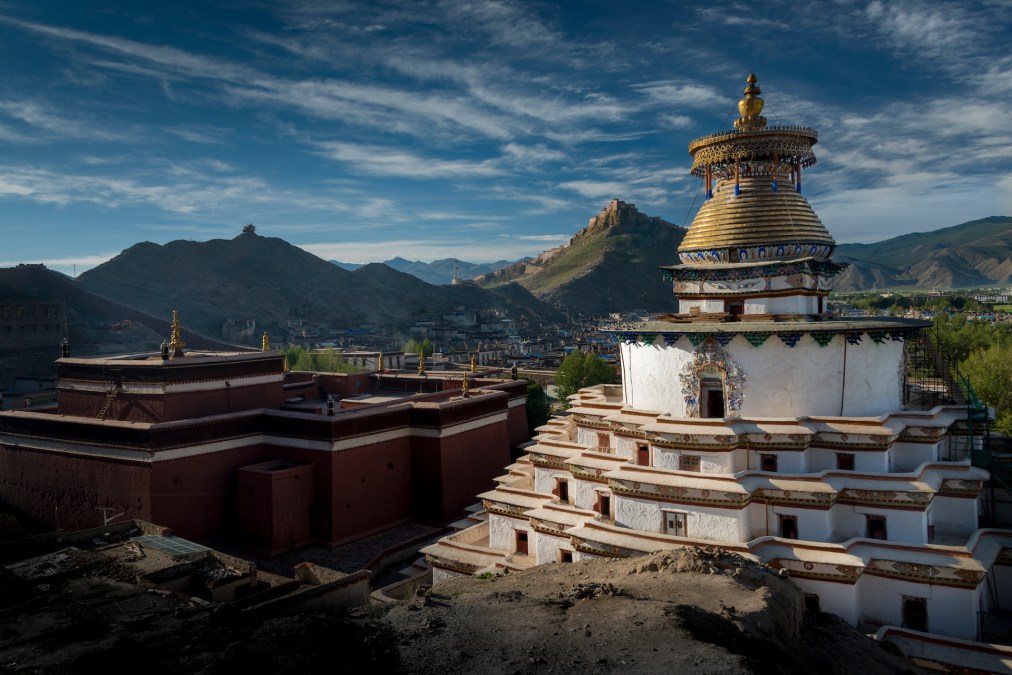
Hackers aimed to infect mobile phones belonging to senior members of Tibetan groups, including people who worked directly for the Dalai Lama, as well as lawmakers in Tibet’s parliament, according to new findings from a team of researchers at the University of Toronto.
The digital rights group Citizen Lab on Tuesday detailed an apparent cyber-espionage effort which involved attackers posing as journalists, Amnesty International researchers, nongovernmental organization workers and other faked identities to send malicious links in a WhatsApp conversation. Researchers observed the campaign, dubbed Poison Carp, between November 2018 and May 2019.
Hackers relied on eight Android browser vulnerabilities, Android spyware, a single iOS exploit chain (a combination of malicious actions allowing hackers to achieve a goal) and iOS spyware. None of the attacks utilized zero-day exploits, the name given to hacking tools that take advantage of never-disclosed vulnerabilities.
None of the intrusion attempts detected here were successful, but at least one person reported clicking on the malicious link, Citizen Lab said. Running up-to-date software on their phones was apparently enough to help targets avoid infection.
Some of the malicious tools also were noted in previous research detailing similar attacks against China’s Uighur population reported by experts on Google’s Project Zero team, and in other findings by the security firm Volexity. Hackers, by infiltrating a phone, could have collected location information, message details, leveraged the phone’s camera and microphone and mapped contacts.
Those attacks were later attributed to China and, although Citizen Lab does not speculate who may be behind the effort revealed Tuesday, the Chinese government for years has dedicated vast surveillance efforts to gather information about both the Tibetan and Uighur populations.
“Based on these similarities, it is likely the campaigns were conducted by the same operator, or a coordinated group of operators, who have an interest in the activities of ethnic minority groups that are considered sensitive in the context of China’s security interests,” Citizen Lab researchers wrote.
Along with providing insight into international spying tactics, this research also provides the latest evidence that iOS software is more vulnerable than many security practitioners realized until very recently. The zero-day broker Zerodium in September noted that the most advanced Android exploits now are worth more than their iOS counterparts, in part because of the popularity of iOS hacking tools.
More Scoops
Pegasus, NoviSpy variant spyware found on devices of Serbian activists
It’s the first Pegasus infection of 2026 that Citizen Lab is forensically confirming, and the SHARE Foundation said it’s the biggest wave of spyware surveillance in Serbia…
DarkSword’s GitHub leak threatens to turn elite iPhone hacking into a tool for the masses
Second iOS exploit kit now in use by suspected Russian hackers
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/tibet-citizen-lab-spyware-espionage/