Supply-chain vulnerabilities are a 'digital public health crisis,' says DHS's Manfra
Full article723 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Persistent supply chain vulnerabilities such as hardware and software bugs “amount to a digital public health crisis” that the government and private sector must work together to resolve, according to the Department of Homeland Security’s top cybersecurity official.
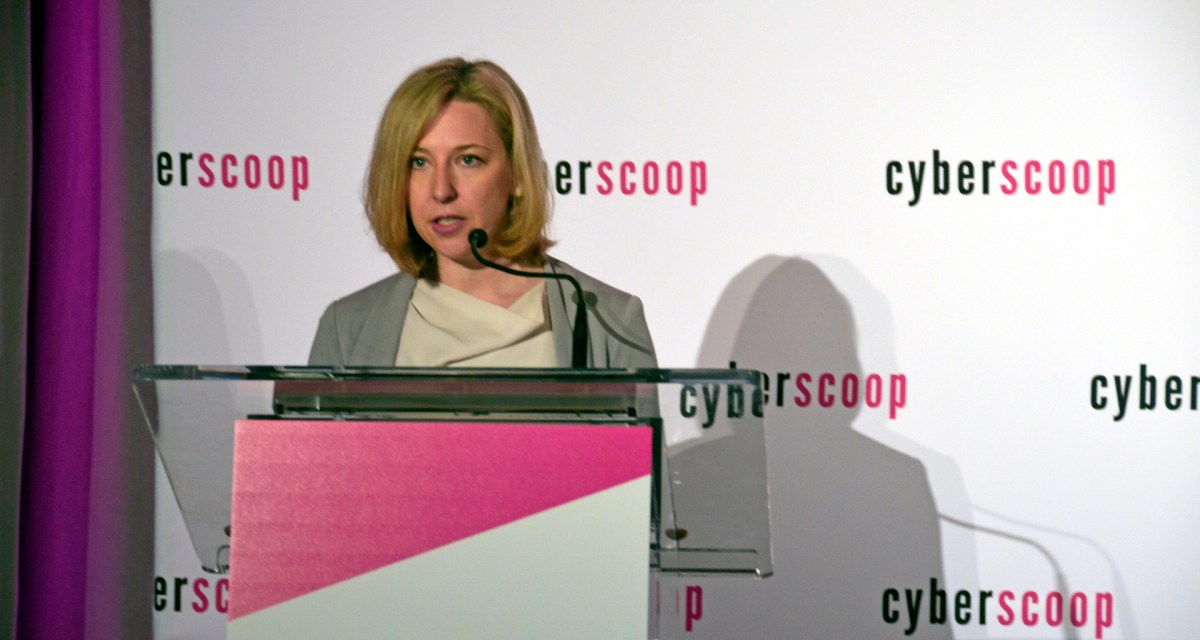
Persistent supply chain vulnerabilities such as hardware and software bugs “amount to a digital public health crisis” that the government and private sector must work together to resolve, according to Jeanette Manfra, the Department of Homeland Security’s top cybersecurity official.
“We must begin to think in terms of global digital public health, where the decisions of each of us have the potential to affect us all,” Manfra said Monday at SF CyberTalks presented by CyberScoop ahead of the RSA Conference in San Francisco.
Manfra, DHS’s assistant secretary for the Office of Cybersecurity and Communications, said that security tools need to be pushed further down the supply chain “to prevent unseen and unknown risk transmitting from vendors to infrastructure.”
DHS earlier this year established a supply chain program that provides cyber risk assessments to critical infrastructure firms and federal agencies on products they may acquire or deploy.
The supply chain is a logical pathway for hackers targeting critical infrastructure. In early April, a cyberattack on billing software disrupted customer transactions for a network of U.S. natural gas pipelines. The incident did not threaten gas companies’ critical operating systems, but it was a reminder that supply chains are in hackers’ crosshairs.
Risk assessment requires “visibility into an often-opaque supply-chain process and a clear understanding of the threat,” Manfra told a crowd of public and private-sector cybersecurity executives.
Manfra also pledged that the U.S. government would continue to publicly call out malicious cyber-activity, adding that such “naming and shaming” must be paired with punitive measures to be effective.
“Our most capable adversaries have stepped up efforts to conduct ‘gray-zone’ cyber-operations to achieve objectives in areas where they are unable or unwilling to compete normally,” Manfra said.
Her comments came as the American and British governments announced that hackers backed by the Russian government had carried out a coordinated campaign against internet traffic routers worldwide.
Private companies have an important role to play in thwarting hackers by “coordinating takedowns, sink-holing, and strategic software updating and patching,” Manfra said.
More Scoops
The long-awaited Trump cyber strategy has arrived
The administration also released an executive order on cybercrime and fraud.
Plankey vows to boot China from U.S. supply chain, advocate for CISA budget
Biden cyber executive order gets mostly plaudits, but its fate is uncertain
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/jeanette-manfra-sf-cybertalks-supply-chain/