Workshop: Cyber Crime and the Law
Full article238 words · extracted from securelist.com · click to collapse



Last week I participated in a student workshop at the “Pontfica Universidad Catlica del Ecuador” – PUCE http://www.puce.edu.ec/. The workshop wasn’t geared only for technical students but was also aimed at students studying law and jurisprudence. During the sessions, we discussed ways to obtain and to join electronic evidence related to malware attacks, how to interpret them and to present to law enforcement for prosecution of cyber criminals.
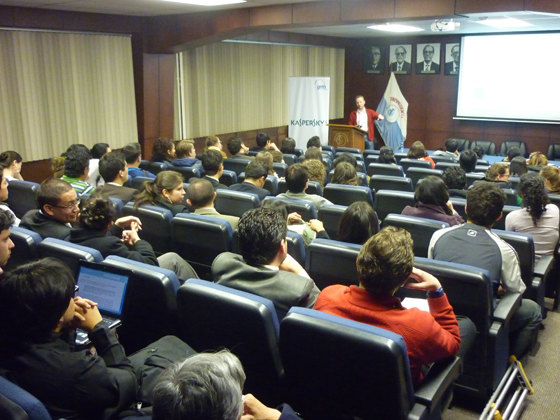
We also analyzed the ongoing merging of classic (traditional) crime to cybercrime in terms of document-cloning, grooming and other crimes.
I believe these initiatives are very important for current students and future law professionals to get a clear understanding of the modern attacks, the legal limitation the reform that is needed to improve the battle against cyber crime.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/workshop-cyber-crime-and-the-law/29793/