CISA's 2023 priorities include election security, corporate cyber risk
Full article639 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Director Jen Easterly said the agency's focus will include working with the C-suite, local officials and educators on key cyber issues.
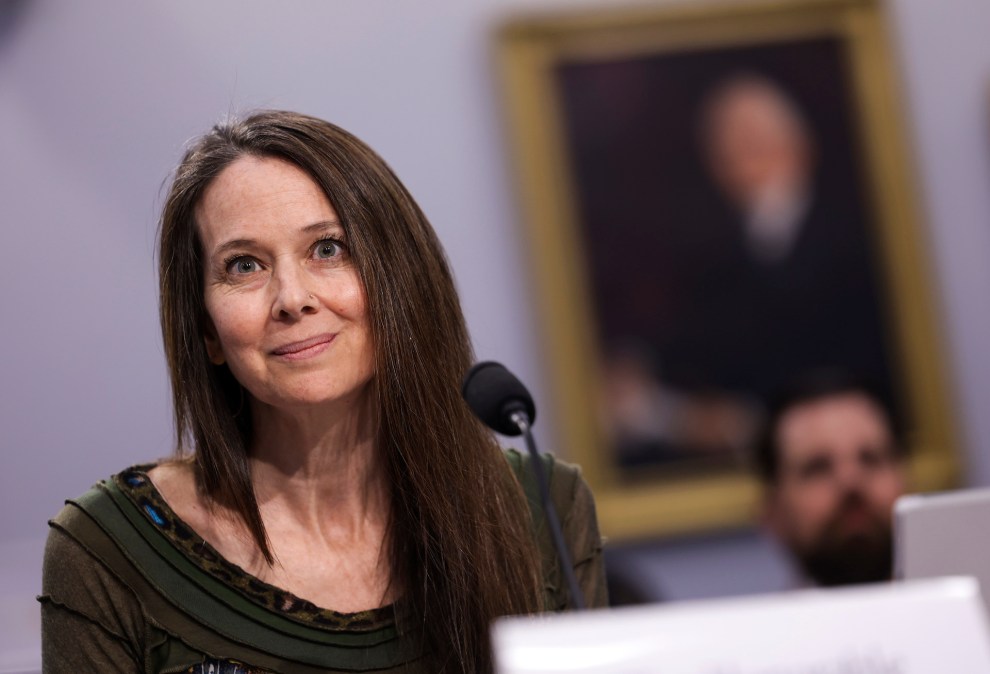
Jen Easterly, director of the Cybersecurity and Infrastructure Security Agency, said the agency’s 2023 priorities include working with state and local officials to prepare for the next presidential election and making inroads with corporate boards to improve how the C-suite manages cyber risk.
“We’re going to be laser focused over the coming year … as we prepare for the general election in 2024,” Easterly said Tuesday during a meeting with the agency’s Cybersecurity Advisory Committee, an independent body that helps guide CISA strategy.
Additionally, she said, the agency is going to zero in on “what boards and C-suite execs must do to effectively manage cybersecurity risk” through a newly launched subcommittee within the advisory committee to focus on corporate cyber responsibility.
Even though it’s only a year old, the advisory committee has become an influential voice in shaping CISA priorities. It has already held 94 meetings and made 48 recommendations. Easterly noted that CISA has accepted “virtually all” the group’s initial batch of 24 recommendations but did not provide details on every suggestion it will implement.
Two early pieces of advice included holding “what to expect” sessions on Election Day with the press and election officials as well as hiring a chief people officer, Elizabeth Kolmstetter.
In addition to helping improve board-level cyber preparedness and continuing to work on election security, Easterly said the agency will commit resources to “a talent management ecosystem and a people-first culture at CISA.”
Furthermore, Easterly also said an agency subcommittee will focus on “shaping the technology ecosystem to be both secure by design and secure by default,” as well as supporting CISA’s cyber 311 initiative and supporting so-called “target rich, resource poor” sectors such as K-12 education, hospitals, water and wastewater facilities and small businesses.
She also said CISA will continue working on the National Cybersecurity Alert system.
“While Shield’s Up … has to be the new normal for national cyber defense in order for it to be sustainable, we can’t just remain on the highest level of alert in perpetuity because that’ll wind up in vigilance fatigue,” Easterly said.
Easterly also said that they’ll roll out a public service awareness campaign later this year. “We know that this is something that’s going to need to be plain and simple and exciting and compelling to be appreciated by the American public.”
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/cisa-2023-priorities/