FBI seizes domains tied to stolen records, DDoS services
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | ipstress.in | ator, The Record reported . Agents also seized two domains, ipstress.in and ovh-booter.com, that offered to conduct “DDoS,” or “Dis |
| domain | ovh-booter.com | reported . Agents also seized two domains, ipstress.in and ovh-booter.com, that offered to conduct “DDoS,” or “Distributed Denial of |
Full article527 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
U.S. authorities took down a related site in 2020.
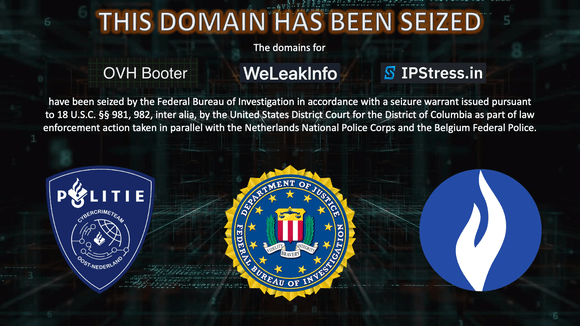
The FBI and Justice Department said Tuesday they had seized the domain of a search engine service that claimed to offer users the ability to scour billions of records of personal data from more than 10,000 data breaches, effectively shutting down the criminal operation.
The site, weleakinfo.to, offered a subscription service where customers could access personal information leaked in data breaches, including names, email addresses, usernames, phone numbers and passwords for online accounts. Such information is valuable to cybercriminals looking to commit identity fraud and financial crimes.
U.S. authorities seized a related website, weleakinfo.com, in 2020. The site boasted more than 12 billion personal records and also offered a monitoring feature to alert customers if their data showed up in the database.
One of the original site’s operators was sentenced to two years in prison in the Netherlands last year. The unnamed Dutch suspect said that he did not create the site but joined it in early 2016 as an administrator, The Record reported.
Agents also seized two domains, ipstress.in and ovh-booter.com, that offered to conduct “DDoS,” or “Distributed Denial of Service” attacks, for hire. In DDoS attacks, cybercriminals flood a target website with traffic in order to render it inoperable.
The FBI coordinated with law enforcement in the Netherlands and Belgium to execute the takedowns. No arrests have been made public in connection with the seizures.
“These seizures are prime examples of the ongoing actions the FBI and our international partners are undertaking to disrupt malicious cyber activity,” said Wayne Jacobs, special agent in charge of the FBI Washington Field Office’s Criminal and Cyber Division. “Disrupting malicious DDoS operations and dismantling websites that facilitate the theft and sale of stolen personal information is a priority for the FBI.”
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/fbi-seizes-domains-tied-to-stolen-records-and-ddos-services/