Top cybersecurity officials stress more funding for federal agencies
Full article652 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Coker and Easterly applaud recommendations around cyber-physical resilience laid out in a new report from the President's Council of Advisors on Science and Technology.
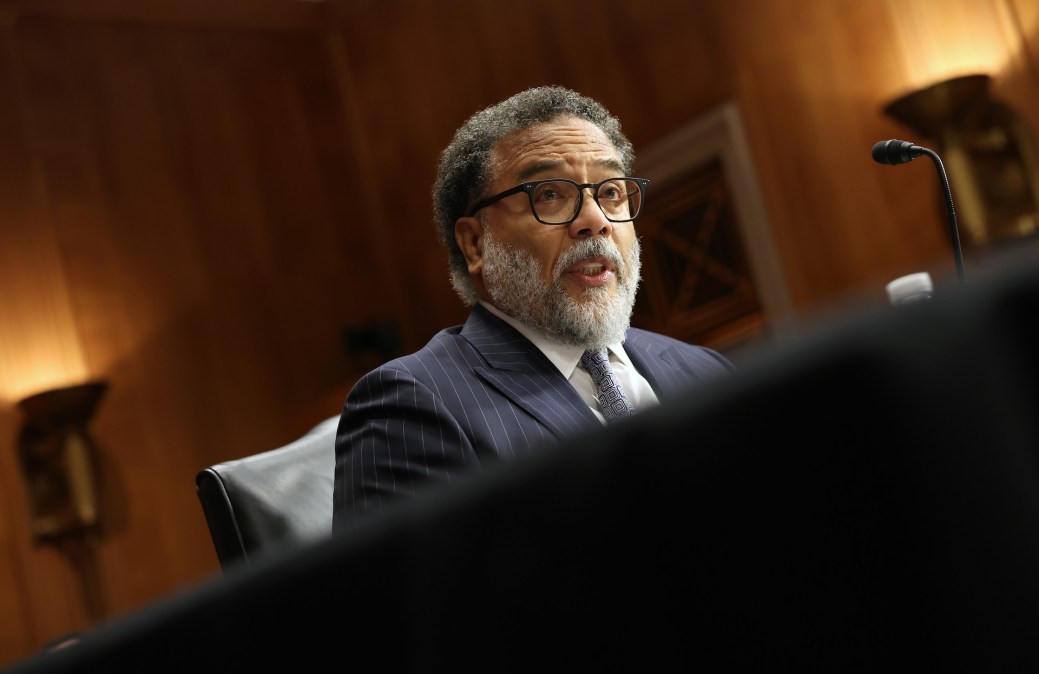
A presidential advisory report on improving the resilience of critical infrastructure sectors won the approval of the nation’s top cybersecurity experts Wednesday, particularly around better funding for the agencies that are supposed to help them protect against cyberattacks.
The report from the President’s Council of Advisors on Science and Technology, which laid out multiple recommendations for the White House to consider, was first approved in January and made public in February. While the report has four overarching recommendations, a large portion is dedicated to gaining a better understanding and prioritizing the increased complexity and interdependencies of critical infrastructure organizations.
At an event panel on the report Harry Coker, the national cyber director, and Jen Easterly, the director of the Cybersecurity and Infrastructure Security Agency, both lauded the report, pointing out in particular the recommendation to give additional funds to the agencies in charge of sectors, known as the sector risk management agencies.
Coker said that President Joe Biden’s fiscal year 2025 budget proposal showed that it was a “priority.”
“I think we can all agree there are certain sector risk management agencies in certain sectors that have invested more significantly in security and resilience,” Easterly said. “And frankly, it’s why we prioritized over the last year and a half working with SRMAs like [the Department of Health and Human Services, the Environmental Protection Agency and the Department of Education]. So we can work with those sectors to provide free services and capabilities.”
Easterly also provided minor updates to multiple initiatives that the agency is pursuing, including that its list of systemically important critical infrastructure entities has grown to just under 500.
However, Easterly also said that there is more work to be done on that front, as UnitedHealth Group was considered a systemically important entity but Change Healthcare was not. HHS is currently monitoring the situation with Change Healthcare after a ransomware attack on the UnitedHealth subsidiary disrupted health care services across the country.
Easterly also said that CISA plans to publish a set of sector-specific cybersecurity performance goals for the finance, information technology, and energy sectors in the coming months.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/pcast-critical-infrastructure-resilience/