BlackByte Ransomware abuses driver to bypass security solutions
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2018-19320 | Ring0 Memcpy Flaw in GIGABYTE GDrv Driver Enables Local Privilege Escalation CVE-2018-19320 is a local privilege-escalation flaw in the GDrv (gdrv.sys) low-level Windows kernel driver shipped with GIGABYTE APP Center (v1.05.21 and earlier), AORUS GRAPHICS ENGINE (before 1.57), XTREME GAMING ENGINE (before 1.26), and OC GURU II (v2.08). The driver exposes an unchecked ring0 memcpy-like routine, so a low-privileged local process can have it copy attacker-controlled data into protected kernel memory. An attacker who exploits this gains complete control of the affected system at ring 0, enabling kernel-level code execution and the ability to disable security software, which ransomware operators such as RobbinHood and BlackByte have done by leveraging the vulnerable GIGABYTE driver. Any Windows system running one of the affected GIGABYTE utilities, or where the gdrv.sys driver those utilities install remains present, is exposed. The flaw was added to CISA's Known Exploited Vulnerabilities catalog on 2022-10-24 with known ransomware use and is being actively exploited; EPSS estimates a 3.6% probability of exploitation within 30 days (89th percentile). Do: Apply vendor updates per CISA's required action: upgrade to AORUS GRAPHICS ENGINE 1.57 or later, XTREME GAMING ENGINE 1.26 or later, and current APP Center and OC GURU II releases, or uninstall the utilities entirely. Hunt endpoints for the gdrv.sys driver in the System32 drivers folder, since it can persist after the utility is removed, and prioritize patching systems where unprivileged users can invoke it, as ransomware operators actively load or exploit this driver to gain ring0 access and kill security software. | 7.8 | 4% | KEV ransomware PoC ×2 |
| mass≈1,000,000+ systems (bundled utilities from a top-tier motherboard/GPU vendor; no published install counts) | |
| CVE-2019-16098 | The driver in Micro-Star MSI Afterburner 4.6.2.15658 (aka RTCore64.sys and RTCore32.sys) allows any authenticated user to read and write to arbitrary memory, I/ The driver in Micro-Star MSI Afterburner 4.6.2.15658 (aka RTCore64.sys and RTCore32.sys) allows any authenticated user to read and write to arbitrary memory, I/O ports, and MSRs. This can be exploited for privilege escalation, code execution under high privileges, and information disclosure. These signed drivers can also be used to bypass the Microsoft driver-signing policy to deploy malicious code. NVD description · AI analysis pending | 7.8 | 20% | PoC |
| — |
Full article553 words · extracted from securityaffairs.com · click to collapse

The BlackByte ransomware operators are leveraging a flaw in a legitimate Windows driver to bypass security solutions.
Researchers from Sophos warn that BlackByte ransomware operators are using a bring your own vulnerable driver (BYOVD) attack to bypass security products.
In BYOVD attacks, threat actors abuse vulnerabilities in legitimate, signed drivers, on which security products rely, to achieve successful kernel-mode exploitation.
Other ransomware gangs in the past abused the BYOVD technique to disable security solutions, for example RobbinHood and AvosLocker operators exploited vulnerabilities (i.e. CVE-2018-19320) in the gdrv.sys and asWarPot.sys.
While investigating the most recent variant of the ransomware, which is written in Go, the experts discovered that the threat actors are exploiting a vulnerability in a legitimate Windows driver to bypass security solutions.
“We found a sophisticated technique to bypass security products by abusing a known vulnerability in the legitimate vulnerable driver RTCore64.sys.” reads the post published by Sophos. “The evasion technique supports disabling a whopping list of over 1,000 drivers on which security products rely to provide protection. Sophos products provide mitigations against the tactics discussed in this article.”
“Bring Your Own Driver” is the name given to this technique [1, 2, 3, 4, 5, 6] — exploiting a targeted system by abusing a legitimate signed driver with an exploitable vulnerability.”
The researchers discovered that the BlackByte ransomware operators are exploiting a privilege escalation and code execution vulnerability (CVE-2019-16098, CVSS score 7.8) affecting the Micro-Star MSI Afterburner RTCore64.sys driver.
The RTCore64.sys and RTCore32.sys drivers are widely used by Micro-Star’s MSI AfterBurner 4.6.2.15658 utility which gives extended control over graphic cards on the system. The CVE-2019-16098 exploitation allows an authenticated user to read and write to arbitrary memory, potentially leading to privilege escalation, code execution under high privileges, or information disclosure.
Sophos researchers pointed out that Kernel Notify Routines are used by loaded drivers to be notified by the kernel of system activity, Drivers related to security products often rely on these routines to collect information about system activity.
The experts noticed that the ransomware sample they analyzed has multiple similarities with the EDR bypass implementation used by the EDRSandblast open-source tool which allows abusing vulnerable signed drivers to evade detection.
Siphos experts also identified the kernel routines to deactivate the ETW (Event Tracing for Windows) Microsoft-Windows-Threat-Intelligence provider which is used to log the use of API calls associated with malicious activities such as NtReadVirtualMemory to inject into another process’s memory. Disabling ETW, every security feature that relies on them is blind.
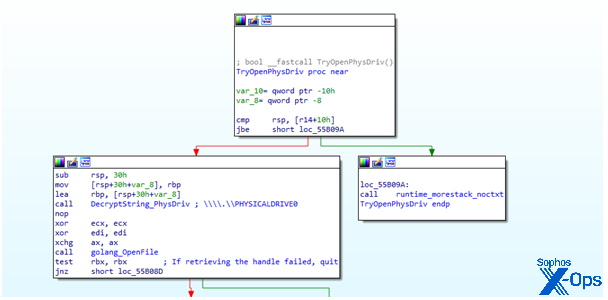
“Once the anti-analysis checks finish, BlackByte attempts to retrieve a file handle of the Master Boot Record, as seen in Figure 3. If failed, the ransomware tries to at least bypass User Access Control and restart itself with higher privileges via CMLUA or CMSTPLUA UAC Bypass.” continues the report.
Experts provide the following recommendations to defend against such type of attacks:
- Threat actors usually exploits well known vulnerabilities in the used driver, for this reason by keeping track of the latest security issues it is possible blocklist drivers known to be exploitable.
- Always keep track of the drivers installed on your systems and keep them up to date.
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, BlackByte ransomware)
[adrotate banner=”5″]
[adrotate banner=”13″]
Text extracted automatically; images, tables and formatting may be missing. Original: https://securityaffairs.com/136816/malware/blackbyte-ransomware-byovd-attack.html