Area41, formerly known as …
Full article417 words · extracted from securelist.com · click to collapse



Gruezi from Zurich, Switzerland, where the Area41 conference is currently being held. Area41 doesn’t ring a bell? Well, this event went under a renaming process and was formerly known as Hashdays, that took place in Lucerne. However, the steering team behind it still is the DEFCON Switzland group. And they have found a fantastic venue! The Komplex457 building oozes that indie type of atmosphere, that makes you feel right at home.
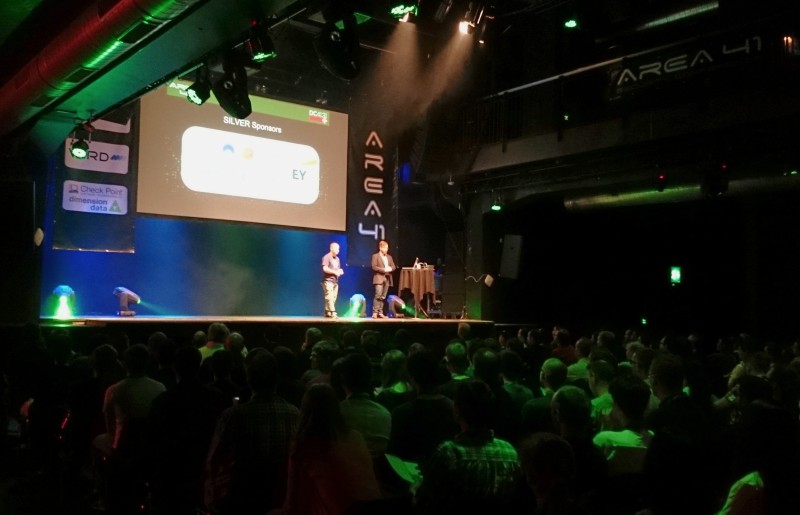
Opening ceremony with Candid Wüst and Stefan Friedli.
Since the event is organised by the DEFCON Switzerland group, it’s not lacking the trademark puzzle. This time every attendee gets a fancy coin as a badge, that will give you the first hint to solve the puzzle game.

The Area41 badge.
Halvar Flake was invited to hold the Keynote (slides are already available). He made everyone in the audience aware of the chain of trust and how much the IT industry as a whole is depending on certification authorities (and yes, there are hundreds of them!) as well as on trusting the goods produced by the hardware industry, especially with the recent revelations in mind. He finally pleaded for more transparency, for example by CAs publishing lists of files officially signed by them. By doing so everyone is able to verify if a digital signature on software is genuine or if the file got signed by a third party with stolen keys from a breach. Security clearly goes further than solely software security.
The bandwidth of talks presented here shows a great variety, from vulnerability research to mobile threats, bitcoins or just entertaining stories in the field of IT-security. Make sure you have a closer look at the agenda here. Overall, the event presents itself with a very open, friendly atmosphere – just what you would expect from the successor of the Hashdays.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/area41-formerly-known-as/63831/