Threat awareness, cloud security, quantum computing among chief agency cyber policy priorities ahead
Full article614 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The interim Federal Chief Information Security Officer spelled out some 2025 agenda items for feds at CyberTalks.
Listen to this article
0:00
Learn more.
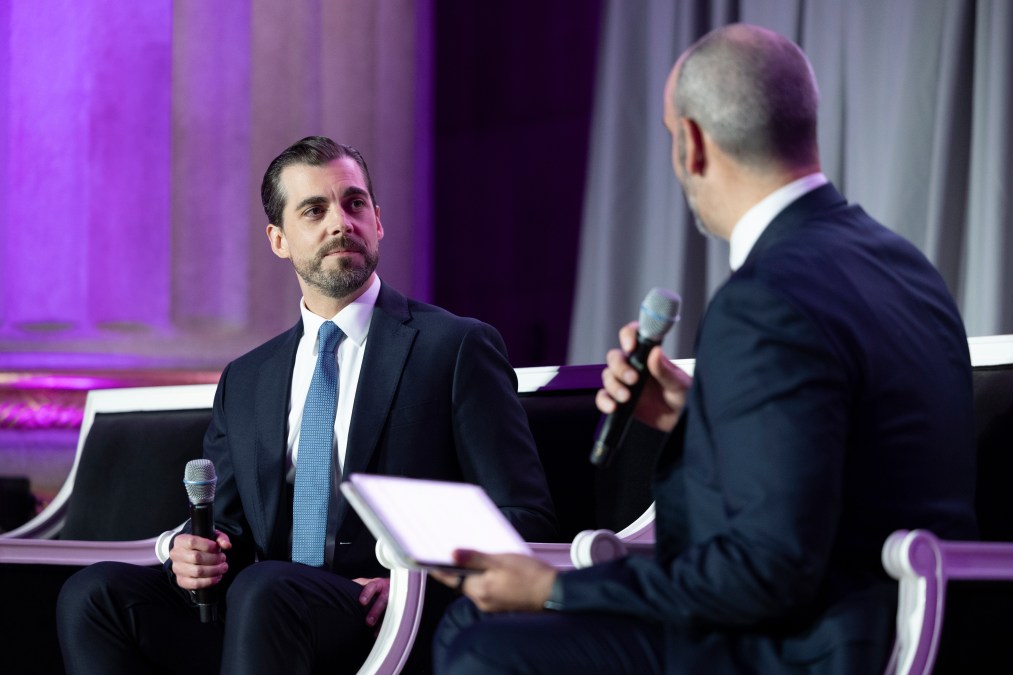
Top federal security and IT officials recently met to discuss 2025 cyber policy priorities, setting an emphasis on sustaining zero trust, building up awareness of threats against agency systems, securing the cloud and getting ready for post-quantum cryptography, the interim Federal Chief Information Security Officer said Wednesday.
At that joint federal Chief Information Officers Council and Federal CISO Council meeting, there was a discussion of “what’s coming next, what are we seeing coming down the pike that you can go back to your team and have meaningful discussions about where your cyber strategy is going,” Federal CISO Mike Duffy said at CyberTalks, presented by CyberScoop. “There were four things we discussed as, ‘Please take note, federal CIOs and CISOs. Let’s see these through in 2025.’”
One of those four things was advancing zero trust, a subject also discussed elsewhere at CyberTalks. Another was “operational visibility,” Duffy said. That means agencies taking advantage of existing investments, he said, to “gain visibility across your environments and make a difference, make an impact, reduce risk individually, so that across the government, we have visibility as the threat actor moves.”
Another was “hardening secure cloud environments,” Duffy said, namely by turning to the Cybersecurity and Infrastructure Security Agency’s Secure Cloud Business Applications Project to protect federal information.
And another was quantum readiness, including for post-quantum cryptography (PQC). “It’s critically important for agencies to be thoughtful about their inventories, how they are planning for migration of their critical systems to PQC, considering what the future holds and what the next steps can be,” Duffy said.
November’s election will bring a new president, regardless of who wins between Democrat Kamala Harris or Republican Donald Trump.
But it’s important for federal agencies to head into the new year with “unified effort,” Duffy said.
Looking ahead to policy developments in 2025 still involves a continuation of things that have come before, he said. That means things such as setting foundational governance structures on things like artificial intelligence or secure software development, advancing “critical work” for the long-term like multifactor authentication and phishing resistance and making good use of past investments like those for CISA’s Continuous Diagnostics and Mitigation program.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/federal-cyber-priorities-threat-awareness-cloud-security-quantum-computing/