Global beef provider JBS interrupted by 'organized' attack
Full article681 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The White House said it's been in touch with JBS leadership since Sunday.
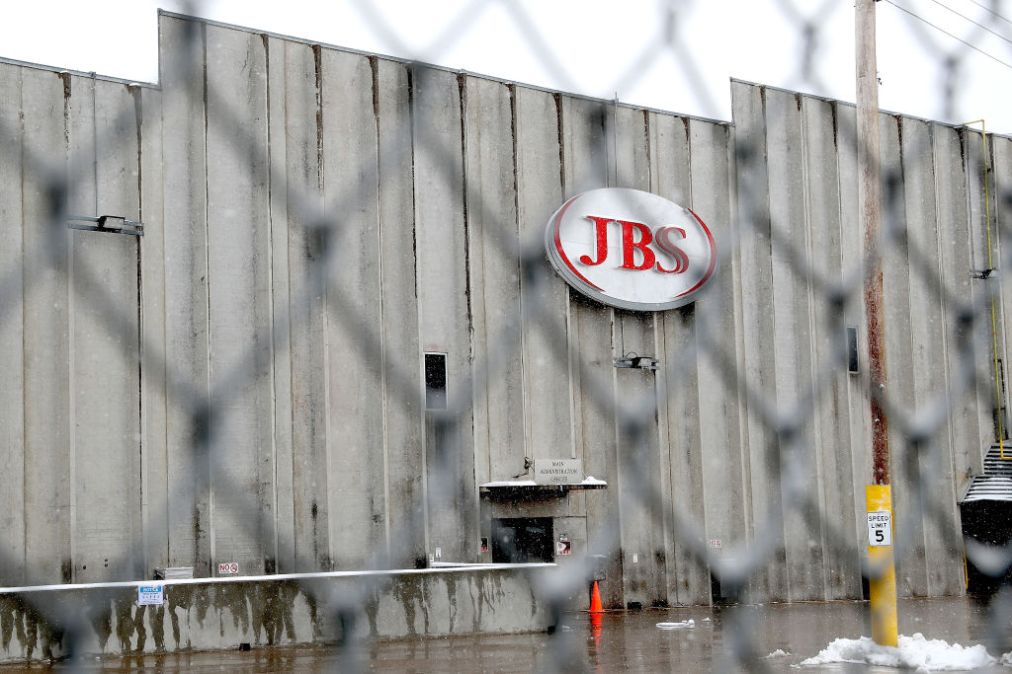
Production at a number of meat packaging facilities in Australia, Canada and the U.S. were disrupted Tuesday as JBS, the world’s largest meat supplier, contended with a digital security incident.
Brazil-based JBS, which employs more than 230,000 people globally, said Sunday it had been the target of an “organized cybersecurity attack” that apparently targeted the firm’s IT systems in North America and Australia. The company is the largest meat and food processing firm in Australia, with 47 facilities there as well as offices in Canada and Colorado.
The specific nature of the security incident remains unclear. The hack, though, comes just three weeks after hackers infected another commodities provider, Colonial Pipeline, with ransomware, which halted fuel deliveries in the southern U.S. for multiple days.
The White House has been in contact with JBS since Sunday, and has offered assistance to the company, principal deputy press secretary Karine Jean-Pierre told reporters on Tuesday.
“JBS notified the administration that the ransom demand came from a criminal organization, likely based in Russia,” Jean-Pierre said. “The White House is engaging directly with the Russian government on this matter, and delivering the message that responsible states do not harbor ransomware criminals.”
JBS had shuttered much of the company’s network activity in North America and Australia on Monday, suggesting the hack may result in delayed transactions between customers and suppliers, Bloomberg reported. The breach also forced the closure of a beef plant outside Calgary, Alberta, according to union officials, and resulted in the cancellation of slaughterhouse shifts at a plant in Greeley, Colorado.
“The company took immediate action, suspending all affected systems, notifying authorities and activating the company’s global network of IT professionals and third party experts to resolve the situation,” JBS said in a statement. “The company’s backup servers were not affected, and it is actively working with an incident response firm to restore its systems as soon as possible.”
JBS brands include Pilgrim’s, Great Southern and Aberdeen Black.
Investigators have not identified any suspect or specific malicious software that might be responsible for the attack.
Hundreds of workers at JBS plants in the U.S. had reportedly been infected with COVID-19 in early 2020, resulting in the closure of the meat plant in Greeley, as the Denver Post reported. Employees said the company relied on a “work while sick” culture, according to local news outlets. Health officials also traced virus outbreaks to JBS beef processing plants in Nebraska, Texas, Wisconsin, Michigan and Pennsylvania.
Update, June 1, 2:40pm ET: This story has been updated to include mention of the White House’s engagement with JBS, and the possible connection to Russian hackers.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/meatpacking-hack-jbs-ransomware-australia/