Warkitteh, Mainframes and planes
Full article301 words · extracted from securelist.com · click to collapse

This years DefCon just ended and thousands of hackers, security professionals and other visitors heading back home. This years schedule was again a good mix of talks, but which to attend is not that easy due to the mass of visitors. That’s why the organizers will move again next year to a different location, in order to deal with the growth of participants and events happening.
Five main tracks of talks, skytalks, contests and areas for different interests fills participation schedule for three days easily. Some talks got lots of attention as the experiment by Gene Bransfield, who utilized a cat to map WiFis in the neighborhood, named “Warkitteh“. Hacking airplanes let one quick think of horror scenarios, but, as Phil Polstra stated, it’s not possible to override the pilot. But also attacks on Mainframes were discussed. Mainframes are special systems, mainly used in enterprise and government segement. Several talks focused on hacking connected devices, reflecting the general IoT (Internet of Things) trend.
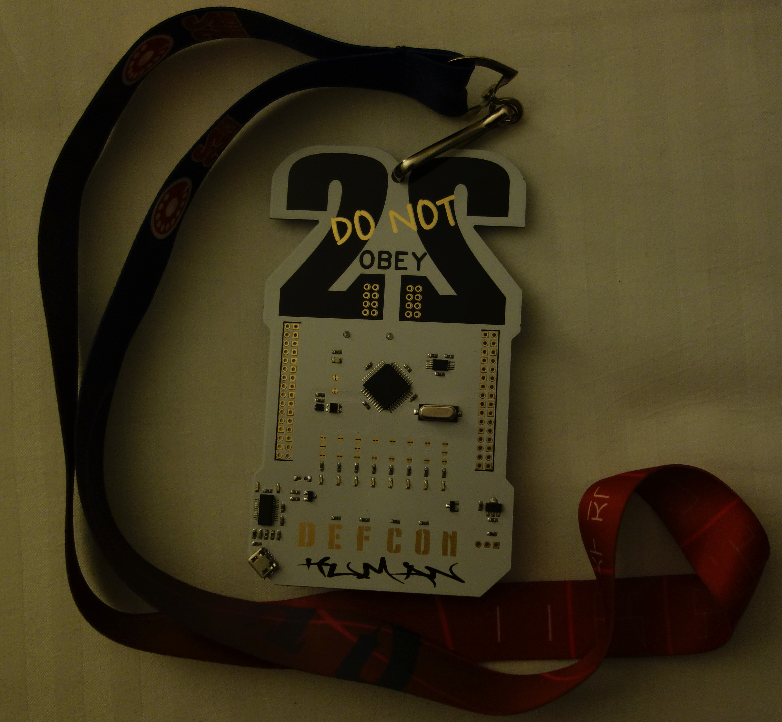
This years DefCon-Badge was again an electronic one, open for hacking and modifying. This ranked from basic to advanced LED/Light-extensions to Quadcopter mounting.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/warkitteh-mainframes-and-planes-defcon22/65689/