As adversaries get craftier, Marine Corps cyber official touts appeal of zero
Full article707 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The Marine Corps wants to be proactive.
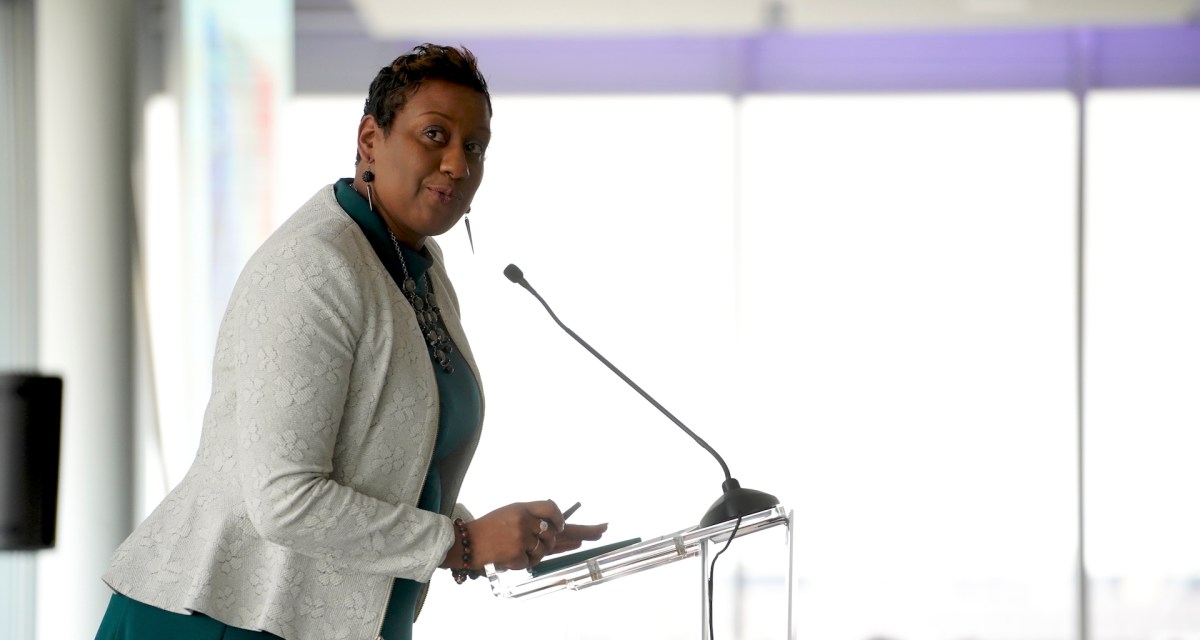
As the Department of Defense tries to be more proactive about preventing hackers from gaining access to its networks, the Marine Corps is working to implement zero-trust security, a top Marine Corps cybersecurity official said Tuesday.
Under the approach, a network never trusts users or devices automatically, and they must meet certain security standards, such as multi-factor authentication, before connecting. For military agencies, zero trust could help reframe how they think about digital adversaries, said Renata Spinks, the cyber technology officer for the Marine Corps Forces Cyberspace Command.
“In some cases today we’re very reactive. A breach occurs, we get an alert, and then we do incident response. Looking at user credentials … configuration policies, and procedures” could get the Pentagon one step ahead of would-be attackers, Spinks said at the Zero Trust Security Summit presented by Duo Security and produced by CyberScoop and FedScoop
The Department of Defense has already begun working on implementing this zero-trust approach through its new “Comply to Connect” pathfinder program, Spinks said.
Spinks warned that simply creating standards for which devices can connect to the Department of Defense Information Network (DODIN) or the Marine Corps Enterprise Network (MCEN) won’t cut it. Network defenders need to think about ways the adversary may try to outsmart zero-trust frameworks, she said.
“The enemy gets a vote,” Spinks said. “Those architectures have to consider the enemy, the adversary, the [tactics, techniques, and procedures] they are learning as we distribute our policies.”
Part of the reason zero trust is top of mind for Spinks is due in part to the plethora of breaches in the public and private sector alike, including those at the Office of Personnel Management and point of sale systems, which have revealed government employees’ personally identifying information (PII) to hackers.
“If I know where this person shops and they just so happen work for the Department of Defense and Air Force and that person is a commander who’s going to make decisions, maybe … I’ll go through their different logins — publicly available data — and I’ll infiltrate their cell phone,” Spinks said, speaking from the perspective of a potential attacker. The phone could then be a problem, she said.
“Quite possibly there may not be a policy in place where they detect when someone has plugged that phone in and now [the hacker has] the ability to gain access to that government system,” Spinks said.
Government employees’ social media postings about their job history and personal lives is another issue, especially as hackers may cross-reference publicly available PII to those details, Spinks said. All of it increases the potential for an adversary to mimic a network user if there aren’t other safeguards in place, she said.
“The ability to aggregate that information is why the zero-trust model is so important,” Spinks said.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/renata-spinks-zero-trust-pentagon-military/