A few words about the HLux botnet
Full article221 words · extracted from securelist.com · click to collapse



Today my colleague Jorge Mieres found some interesting information related to the new HLux botnet.
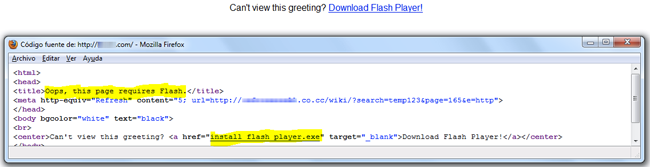
This new worm is propagating via e-mail with a backboned administration through a crimeware pack called BOMBA. The scam messages come with a message to a fake eCard requiring installing Flash Player (an old scammers trick).
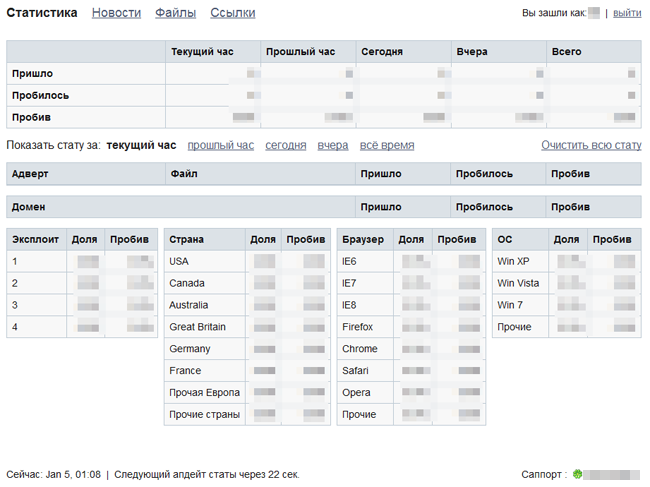
After the infection, the newly installed malware downloads a malicious update which is detected by Kaspersky as Email-Worm.Win32.Hlux.c and establishes a connection with BOMBA’s server reporting statistics about the infection.
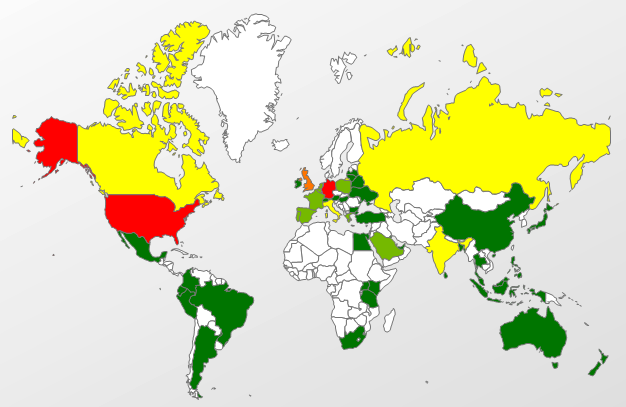
Our statistics for Jan 5 show countries with the highest infection attempts are the U.S., Germany and the U.K.
We’ll keep researching this issue and will keep you updated.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/a-few-words-about-the-hlux-botnet/29806/