Report: Discovery rate of new software vulnerabilities flattens
Full article574 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The rate at which software vulnerabilities are discovered by cybersecurity researchers is flattening off and may actually be falling back to levels lower than prior years, according to new figures.
The rate at which new software vulnerabilities are discovered and catalogued by cybersecurity researchers flattened off during 2016 after steeply rising for the past five years, according to new figures Monday from Risk Based Security.
But the proportion of very severe vulnerabilities continues to creep up and the number found in industrial control or SCADA systems — the special computer software that runs industrial plants like auto factories or oil refineries — is rising steadily, the security management solutions vendor said.
A total of 15,000 vulnerabilities were reported during 2016, the company said in a report, just slightly above the 14,982 in 2015 — a rate of increase much lower than prior years since 2011, which saw the numbers jump by hundreds or even thousands.
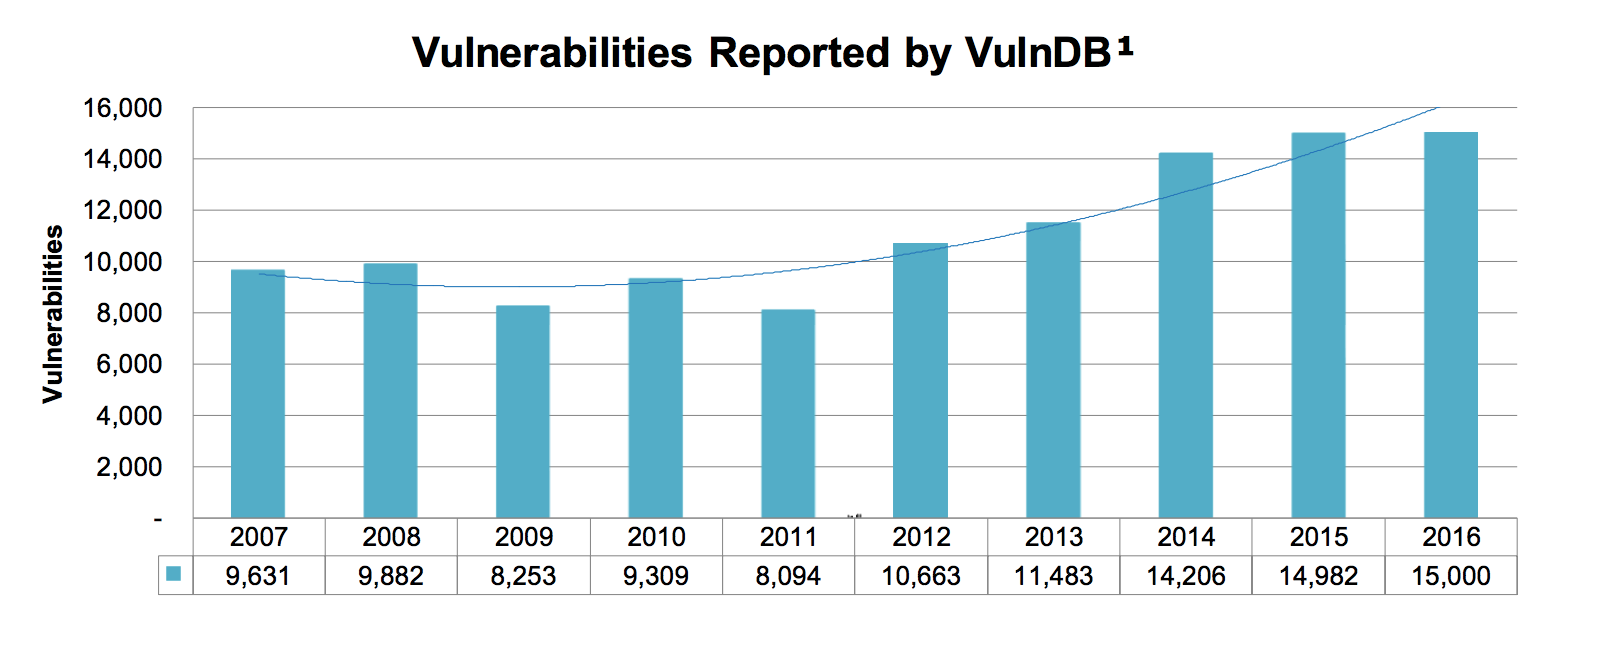
Number of software security vulnerabilities reported and catalogued each year (Source: Risk Based Security)
The numbers come from Risk based Security’s VulnDB service which the company claims is the most comprehensive catalogued of identified software vulnerabilities and is compiled by a proprietary search engine and the analysis of disclosed vulnerability announcements by company researchers.
The report shows that 20.5 percent — more than 1 in 5 — of reported vulnerabilities were rated “critical” according to the Common Vulnerability Scoring System or CVSS, with scores between 9.0 and 10.0.
About one third (32.8 percent) of vulnerabilities reported during 2016 had a public exploit available for them, and just under half (48.9 percent) can be exploited remotely, the company said in a statement. But four out of five (81.3 percent) of them have a documented fix available.
There were 438 vulnerabilities reported in ICS/SCADA software, up from 349 the previous year and 237 in 2014. These vulnerabilities are considered especially worrying because the machinery those systems control is capable of inflicting potentially massive damage in the physical world.
“Using metrics to help determine which vendors and products are putting your organization at risk needs to be a key part of your vendor risk management and procurement process,” said Carsten Eiram, the company’s chief research officer.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/risk-based-security-report-number-vulnerabilities-cve-cvss/