Thousands of Exchange servers breached prior to patching, CISA boss says
Full article632 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
“Patching is not sufficient,” Brandon Wales said.
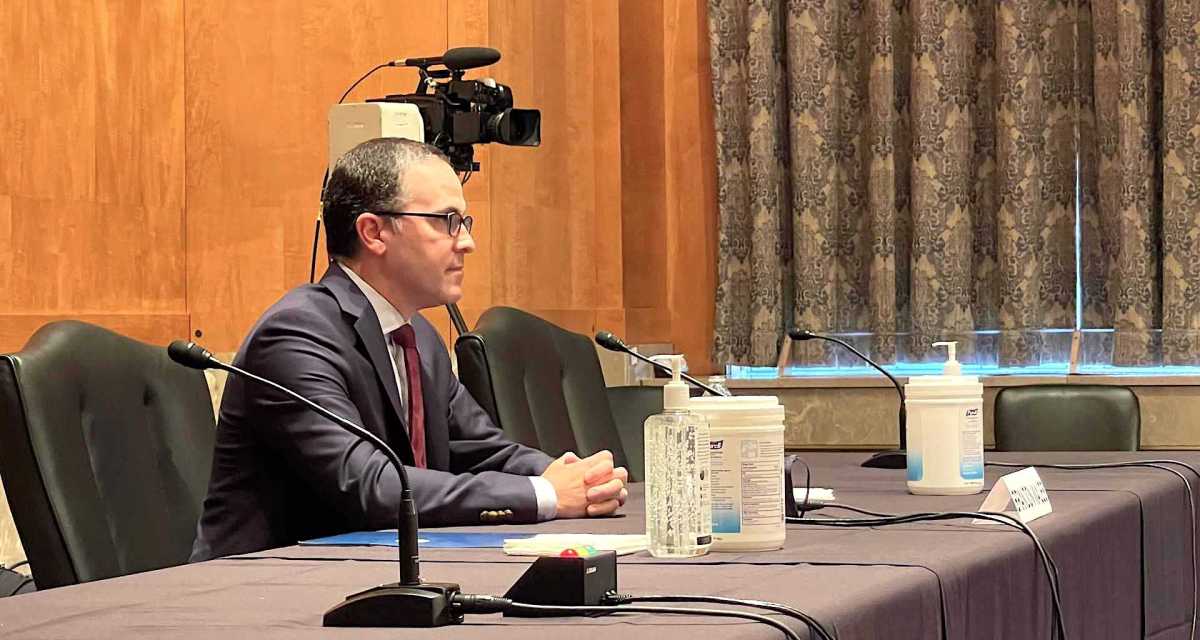
A U.S. government cybersecurity official on Monday warned organizations not to have a false sense of security when it comes to vulnerabilities in Microsoft Exchange Server software, noting that “thousands” of computer servers with updated software had already been breached.
“Patching is not sufficient,” said Brandon Wales, acting head of the Department of Homeland Security’s Cybersecurity and Infrastructure Security Agency (CISA). “There are literally thousands of compromised servers that are currently patched. And these system owners, they believe they are protected.”
“We’re seeing improvements there, but more work needs to be done,” Wales said at an event hosted by Auburn University’s McCrary Institute. “The vulnerabilities can be scriptable, allowing automation exploitation, and that’s just a risk that’s unacceptable.”
Everyone from suspected Chinese spies to ransomware gangs have in the last month moved to exploit the flaws in Exchange Server, a popular email software. At least one of the bugs could allow an attacker to steal the entire contents of email inboxes. U.S. local government organizations and small businesses, which generally lack security resources, are among the most exposed organizations.
Microsoft has released a free tool to detect and mitigate compromises, and CISA has ordered all federal civilian agencies to address the issue.
That sense of urgency has led to progress: Overall, the number of vulnerable systems fell 45% last week to less than 10,000 in the U.S., the White House said Monday.
Wales made it clear, though, that investigating the compromises remains a pressing issue. He called on organizations that find malicious Exchange Server-related activity on their networks to “take aggressive action to remediate” the problem, or to ask for outside help. “You can be used to attack third parties or you can yourself be disrupted,” Wales warned, citing the risk of ransomware.
The malicious activity amounts to the second major set of cyber incidents facing the Biden administration, which is already coping with a suspected Russian hacking campaign that has exploited software made by federal contractor SolarWinds and other vendors.
CISA officials told lawmakers March 10 that CISA had yet to find any signs that federal civilian agencies had been breached in the Exchange Server activity.
Wales said Monday that CISA’s investigation into the matter is ongoing.
“We’re actually still working with a couple of federal agencies … to review their network traffic and identify whether there were any compromises,” Wales said.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/brandon-wales-exchange-server-patch-dhs/