Red Cross attributes server breach to nation
Full article714 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The breached data hasn't shown up on the dark web, so far.
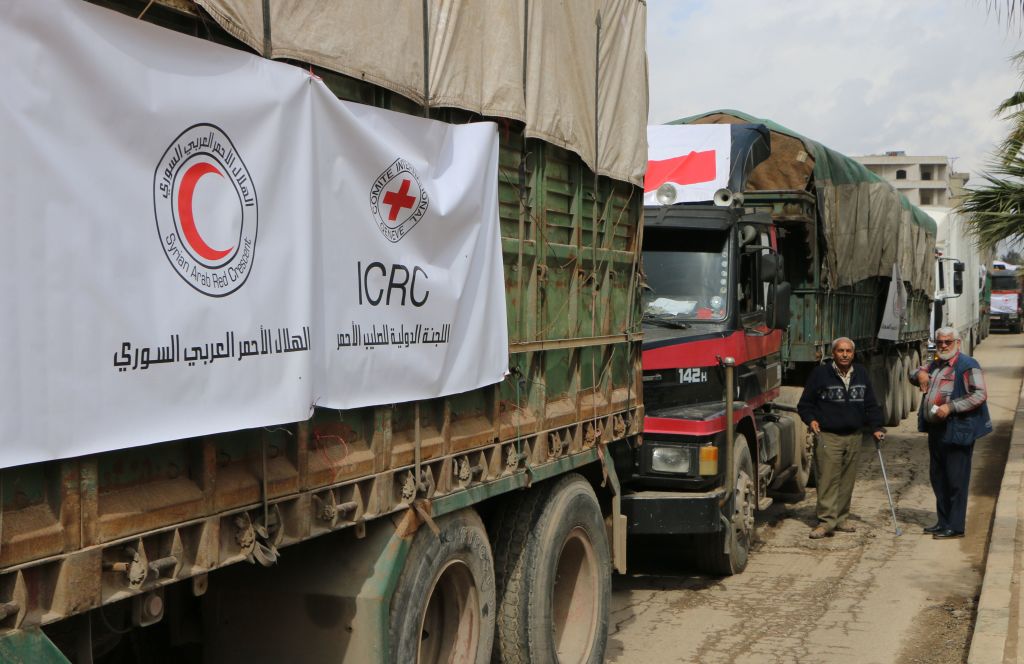
The International Committee of the Red Cross has concluded that a nation-state hacker was behind a cyberattack on its servers discovered last month.
A forensic analysis of the attack revealed the use of tools designed specifically to go after ICRC servers, the organization said Wednesday.
“This was a sophisticated attack — a criminal act — breaching sensitive humanitarian data,” ICRC Director-General Robert Mardini said. “We know that the attack was targeted because the attackers created code designed solely for execution on the concerned ICRC servers, a technique we believe was designed to shield the hackers’ activities from detection and subsequent forensic investigations.”
Separate from Mardini’s statement, the organization released a summary of the technical findings by an unnamed “specialist cyber security company.” The forensic report does not attribute the attack to any specific advanced persistent threat (APT) group, and ICRC declined to speculate on the culprit.
“[M]ost of the malicious files deployed were specifically crafted to bypass our anti-malware solutions, and it was only when we installed advanced endpoint detection and response (EDR) agents as part of our planned enhancement programme that this intrusion was detected,” the organization said.
The ICRC says the hackers have not made contact.
The attack compromised the personal data of more than half a million individuals helped by ICRC’s program, which reunites families separated by conflict, disaster or migrations. Personal data included names, locations, and contact information of individuals served by the group as well as login information for staff and volunteers.
Forensic analysis shows that the breach, which was discovered on Jan. 18, occurred on Nov. 9, 2021.
Hackers were able to get into the system by exploiting an unpatched vulnerability in the password reset management system Zoho ManageEngine ADSelfService Plus, which allowed them to place web shells that provided further access to move within the systems and exfiltrate data, the ICRC. Microsoft warned in November that Chinese-based hackers were using the vulnerability to target victims in the U.S. defense industrial base, higher education, consulting services and information technology sectors.
The ICRC analysis presumes that hackers were able to copy or export data, but none of that information has shown up on the dark web yet.
“We are confident in our initial analysis that no data was deleted in the breach,” the report notes. “This is important because it is allowing us to set up interim systems to get back to work reconnecting loved ones.”
The attack on the human rights organization drew a rebuke from the U.S. State Department, which called on other nations to condemn attacks on humanitarian data.
Mardini said the organization has continued operations of its location program “albeit at minimal service levels, through low-tech solutions (using simple spreadsheets, for example), while we work toward resuming full service with enhanced security features.”
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/red-cross-attributes-hack-to-nation-state-actor/