Voting machine vendor says it installed remote software connections in a ‘small number’ of systems
Full article650 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Election Systems & Software has conceded that it installed remote-access software on systems, potentially leaving them vulnerable to hackers.
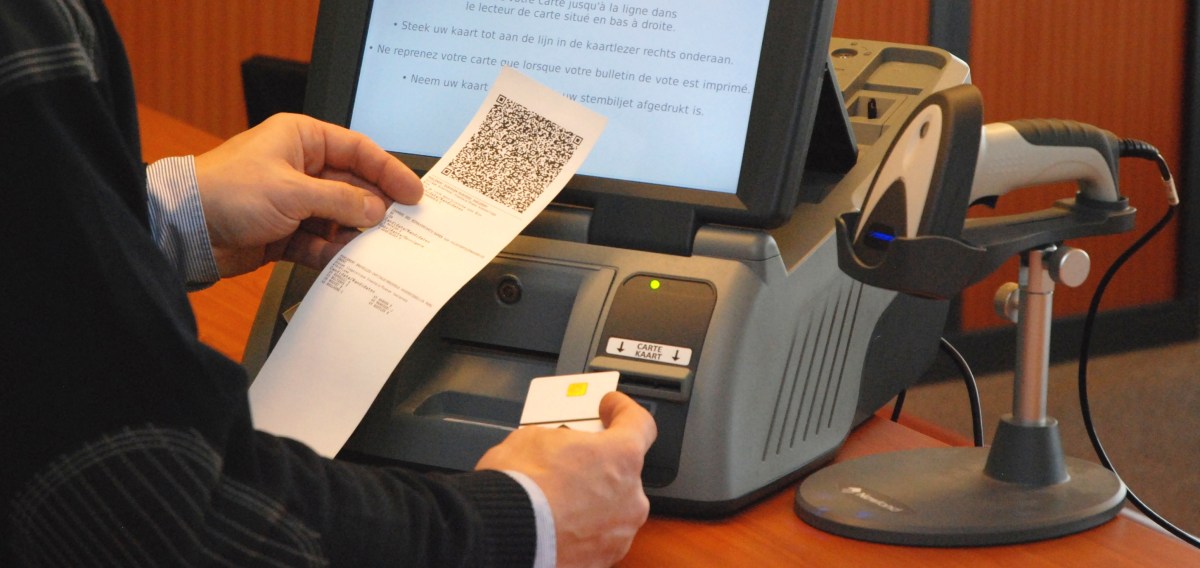
A top manufacturer of voting machines has conceded that it installed remote-access software for a “small number” of election management systems from 2000 to 2006, a practice that experts say leaves the equipment vulnerable to hackers.
The revelation could be a teachable moment as state and local election officials work to shore up their voting infrastructure security for the 2018 midterm elections.
In an April letter to Sen. Ron Wyden, D-Ore., obtained by CyberScoop, Election Systems and Software (ES&S) said it implemented the remote-access software on systems over a six-year period in order to facilitate customer support. Among other voting-related tasks, election management systems are used to program voting machines across a county.
The software in question, pcAnywhere, has proven to be vulnerable to hackers, who stole its source code in 2006.
The Nebraska-based vendor said it never set up a remote connection on voting devices like tabulators or ballot-marking devices. ES&S stopped installing the remote-access software to comply with a 2007 security-testing regime administered by the federal Election Assistance Commission (EAC), the letter said.
Vice’s Motherboard was first to report ES&S’s letter to Wyden.
“We have confirmed that the EMS workstations originally configured with the remote-connection software no longer have this application installed,” ES&S President Tom Burt wrote to Wyden.
The remote access software “was not designed to and did not come in contact with any voting machines,” ES&S said in a statement to CyberScoop. “To be clear, in accordance with EAC guidelines implemented in 2007, ES&S discontinued providing pcAnywhere over a decade ago, and no ES&S customer is using it today.”
ES&S told CyberScoop it installed the remote access software for approximately 3 percent of the 9,000 voting jurisdictions in the country, or about 270 jurisdictions. These installations were carried out at the request of the customers, the company said. Asked what security measures it put in place to prevent a compromise via the software, ES&S said it employed “advanced security and forensic measures to ensure there was no compromise.”
While the remote access software creates an additional attack surface, pcAnywhere is “far more secure than the ‘security through obscurity’ hidden backdoors” that vendors in various industries have put in their equipment, Jake Williams, founder of cybersecurity firm Rendition InfoSec, told CyberScoop.
You can read the full letter below.
UPDATE, 3:06 pm EDT: This story has been updated with a statement from Election Systems and Software (ES&S).
UPDATE, 07/20/18, 3:25 pm EDT: This story has been updated with a more detailed statement from ES&S.
[documentcloud url=”http://www.documentcloud.org/documents/4608550-Elections-Systems-amp-Software-Letter-Received-4.html” responsive=true height=500]
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/es-s-voting-machine-remote-access-ron-wyden/