Search results are sending people to fake Bitrefill checkouts
Scam sites impersonating Bitrefill's crypto checkout appear in search results, tricking victims into sending up to $1,990 in crypto directly to scammers.
Malwarebytes documents a cluster of lookalike domains copying Bitrefill's gift card checkout, surfaced via search engine results rather than email. Victims choose an amount up to $1,990 and pay in Bitcoin, Ethereum, USDC, USDT, Solana, or Litecoin to scammer-controlled addresses, with no recourse since crypto payments are irreversible. Domains use typosquatting and Punycode/IDN homoglyph tricks, and the fake sites run commercial analytics software to measure and optimize victim conversion. Bitrefill's security team is working with takedown specialists to remove the sites.
- Fake Bitrefill checkouts distributed through search results, not email
- Victims send crypto up to $1,990 directly to scammer addresses; payments unrecoverable
- Domains use typosquatting and Punycode/IDN tricks to defeat visual inspection
- Operators run commercial analytics to measure and tune the fraud funnel
- Bitrefill security team working with takedown specialists to remove sites
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | biterflll.com | y tips in seconds. Indicators of compromise (IOCs) Domains: biterflll[.]com bitigift[.]com bitrefall[.]com bitrefill-payments[.]com b |
| domain | bitigift.com | s. Indicators of compromise (IOCs) Domains: biterflll[.]com bitigift[.]com bitrefall[.]com bitrefill-payments[.]com bitrefill-pays[. |
| domain | bitrefall.com | f compromise (IOCs) Domains: biterflll[.]com bitigift[.]com bitrefall[.]com bitrefill-payments[.]com bitrefill-pays[.]com bitregift[. |
| domain | bitrefill.com | ed or charged back. Confirm that the main domain is exactly bitrefill.com before approving a payment. Be wary of domains containing a |
| domain | bitrefill-payments.com | Cs) Domains: biterflll[.]com bitigift[.]com bitrefall[.]com bitrefill-payments[.]com bitrefill-pays[.]com bitregift[.]com bitregill[.]com bitr |
| domain | bitrefill-pays.com | com bitigift[.]com bitrefall[.]com bitrefill-payments[.]com bitrefill-pays[.]com bitregift[.]com bitregill[.]com bitretill[.]com bitrgift[ |
| domain | bitregift.com | trefall[.]com bitrefill-payments[.]com bitrefill-pays[.]com bitregift[.]com bitregill[.]com bitretill[.]com bitrgift[.]com bitrgifts[ |
| domain | bitregill.com | trefill-payments[.]com bitrefill-pays[.]com bitregift[.]com bitregill[.]com bitretill[.]com bitrgift[.]com bitrgifts[.]com bitrnfill[ |
| domain | bitretill.com | [.]com bitrefill-pays[.]com bitregift[.]com bitregill[.]com bitretill[.]com bitrgift[.]com bitrgifts[.]com bitrnfill[.]com bitruflli[ |
| domain | bitrgift.com | -pays[.]com bitregift[.]com bitregill[.]com bitretill[.]com bitrgift[.]com bitrgifts[.]com bitrnfill[.]com bitruflli[.]com butrefill |
| domain | bitrgifts.com | regift[.]com bitregill[.]com bitretill[.]com bitrgift[.]com bitrgifts[.]com bitrnfill[.]com bitruflli[.]com butrefill[.]com pay-bitre |
| domain | bitrnfill.com | regill[.]com bitretill[.]com bitrgift[.]com bitrgifts[.]com bitrnfill[.]com bitruflli[.]com butrefill[.]com pay-bitregill[.]com pay-b |
| domain | bitruflli.com | retill[.]com bitrgift[.]com bitrgifts[.]com bitrnfill[.]com bitruflli[.]com butrefill[.]com pay-bitregill[.]com pay-bitrgift[.]com pa |
| domain | butrefill.com | rgift[.]com bitrgifts[.]com bitrnfill[.]com bitruflli[.]com butrefill[.]com pay-bitregill[.]com pay-bitrgift[.]com pay-bitrgifts[.]co |
| domain | example-pay.com | y’s main domain, as in pay.example.com . An address such as example-pay.com is a completely separate domain that anyone could register. |
| domain | pay-bitigift.com | pay-bitrgift[.]com pay-bitrgifts[.]com pay-butrefill[.]com pay-bitigift[.]com xn--bitrefll-71a[.]com xn--bitrefll-h2a[.]com xn--bitrefl |
| domain | pay-bitregill.com | gifts[.]com bitrnfill[.]com bitruflli[.]com butrefill[.]com pay-bitregill[.]com pay-bitrgift[.]com pay-bitrgifts[.]com pay-butrefill[.]co |
| domain | pay-bitrgift.com | l[.]com bitruflli[.]com butrefill[.]com pay-bitregill[.]com pay-bitrgift[.]com pay-bitrgifts[.]com pay-butrefill[.]com pay-bitigift[.]co |
| domain | pay-bitrgifts.com | ]com butrefill[.]com pay-bitregill[.]com pay-bitrgift[.]com pay-bitrgifts[.]com pay-butrefill[.]com pay-bitigift[.]com xn--bitrefll-71a[. |
| domain | pay-butrefill.com | pay-bitregill[.]com pay-bitrgift[.]com pay-bitrgifts[.]com pay-butrefill[.]com pay-bitigift[.]com xn--bitrefll-71a[.]com xn--bitrefll-h2 |
| domain | xn--bitrefll-71a.com | pay-bitrgifts[.]com pay-butrefill[.]com pay-bitigift[.]com xn--bitrefll-71a[.]com xn--bitrefll-h2a[.]com xn--bitrefll-pay-kfb[.]com xn--bit |
| domain | xn--bitrefll-h2a.com | y-butrefill[.]com pay-bitigift[.]com xn--bitrefll-71a[.]com xn--bitrefll-h2a[.]com xn--bitrefll-pay-kfb[.]com xn--bitrefll-pay-xfb[.]com xn- |
| domain | xn--bitrefll-pay-kfb.com | itigift[.]com xn--bitrefll-71a[.]com xn--bitrefll-h2a[.]com xn--bitrefll-pay-kfb[.]com xn--bitrefll-pay-xfb[.]com xn--bitrefll-q2a[.]com xn--bit |
| domain | xn--bitrefll-pay-xfb.com | 71a[.]com xn--bitrefll-h2a[.]com xn--bitrefll-pay-kfb[.]com xn--bitrefll-pay-xfb[.]com xn--bitrefll-q2a[.]com xn--bitreill-cz9c[.]com xn--bitrei |
| domain | xn--bitrefll-q2a.com | .]com xn--bitrefll-pay-kfb[.]com xn--bitrefll-pay-xfb[.]com xn--bitrefll-q2a[.]com xn--bitreill-cz9c[.]com xn--bitreill-pay-yq4f[.]com xn--b |
| domain | xn--bitreill-cz9c.com | kfb[.]com xn--bitrefll-pay-xfb[.]com xn--bitrefll-q2a[.]com xn--bitreill-cz9c[.]com xn--bitreill-pay-yq4f[.]com xn--btrefill-l2a[.]com xn--pa |
| domain | xn--bitreill-pay-yq4f.com | ay-xfb[.]com xn--bitrefll-q2a[.]com xn--bitreill-cz9c[.]com xn--bitreill-pay-yq4f[.]com xn--btrefill-l2a[.]com xn--pay-bitrefll-fgb[.]com Stop th |
| domain | xn--btrefill-l2a.com | a[.]com xn--bitreill-cz9c[.]com xn--bitreill-pay-yq4f[.]com xn--btrefill-l2a[.]com xn--pay-bitrefll-fgb[.]com Stop threats before they can d |
| domain | xn--pay-bitrefll-fgb.com | 9c[.]com xn--bitreill-pay-yq4f[.]com xn--btrefill-l2a[.]com xn--pay-bitrefll-fgb[.]com Stop threats before they can do any harm. Malwarebytes Br |
Full article1,441 words · extracted from malwarebytes.com · click to collapse
Bitrefill is a legitimate company that sells gift cards for popular stores like Amazon, Deliveroo, Apple, Nintendo, and thousands of others. They also sell eSIMs, and mobile top-ups. You can pay on their website for all of these with cryptocurrency.
The scam is designed to catch people searching for Bitrefill or something it sells, like a gift card. Victims see a search result that appears to lead to Bitrefill but actually points to a lookalike domain. The fake site then takes them through what appears to be a normal purchase. The fake sites are not operated by or affiliated with Bitrefill; scammers have copied its branding and checkout process.
The victim chooses an amount and a cryptocurrency before receiving a QR code and payment address. But instead of paying Bitrefill, they send the cryptocurrency directly to an address controlled by the scammers. They receive nothing in return, and recovering the payment is extremely unlikely.
Why fake crypto checkouts work so well
Phishing typically involves several steps. First, an attacker has to steal a password. Then, they may have to get past two-factor authentication (2FA), log in to the account without tripping a fraud check, and find some way to turn account access into money. Plenty of scams fall apart somewhere in that chain.
This payment scam avoids those hurdles by persuading victims to send money directly to the scammers. There is no account to break into and no stolen card to use. The victim sends cryptocurrency straight to an address the scammers control, and cryptocurrency payments generally cannot be reversed or charged back.
The payment request also fits the situation. A demand for cryptocurrency might look suspicious on many websites, but Bitrefill genuinely accepts it. On a convincing copy of its checkout, paying with cryptocurrency appears completely normal.
All this may explain why we found a cluster of fake sites rather than a single page, with checkouts allowing payments of up to $1,990.
What the fake checkout looks like
The site we examined is a close copy of Bitrefill’s checkout, hosted on a domain built by bolting a word onto the brand name. Everything a customer would expect is present. The branding is right, the layout matches, the page is quick and polished, and the payment flow behaves exactly the way the real one does.
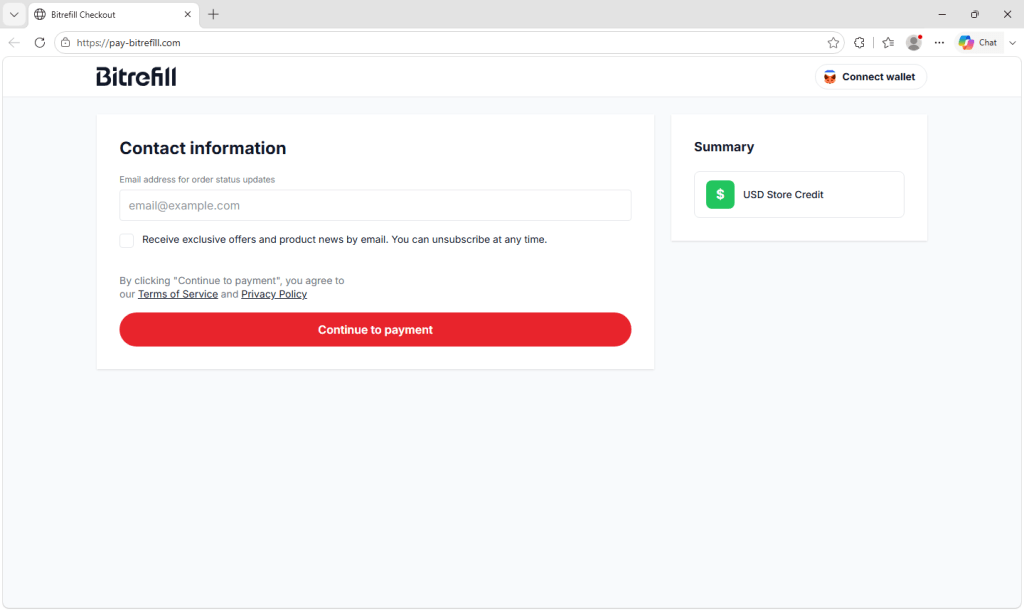
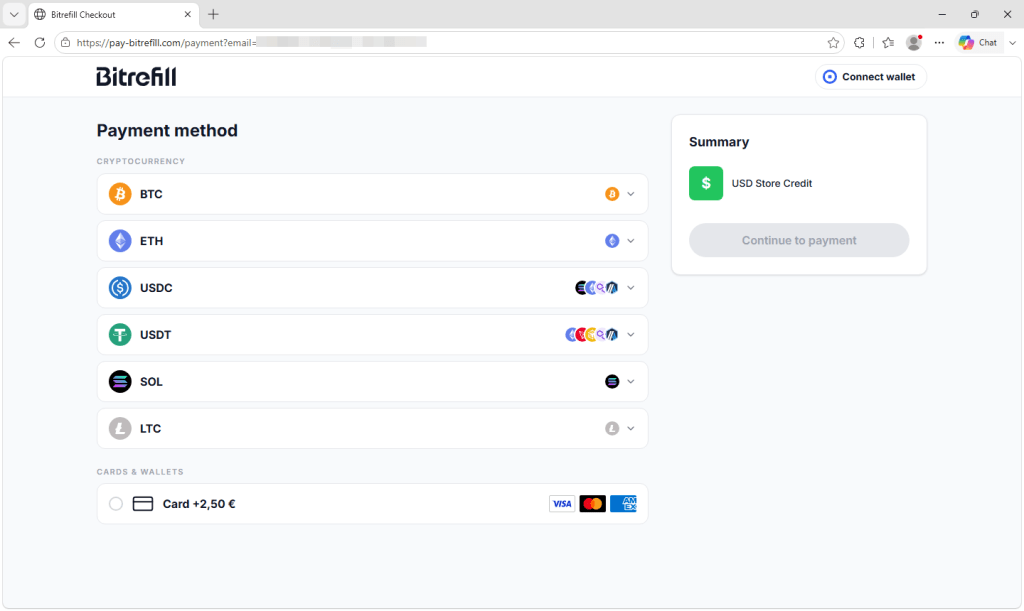
You’re asked for an email address for order updates, with links to terms of service and a privacy policy. You then choose how to pay, from a list offering Bitcoin, Ethereum, USDC, USDT, Solana, and Litecoin. The site also offers card payments for a small surcharge.
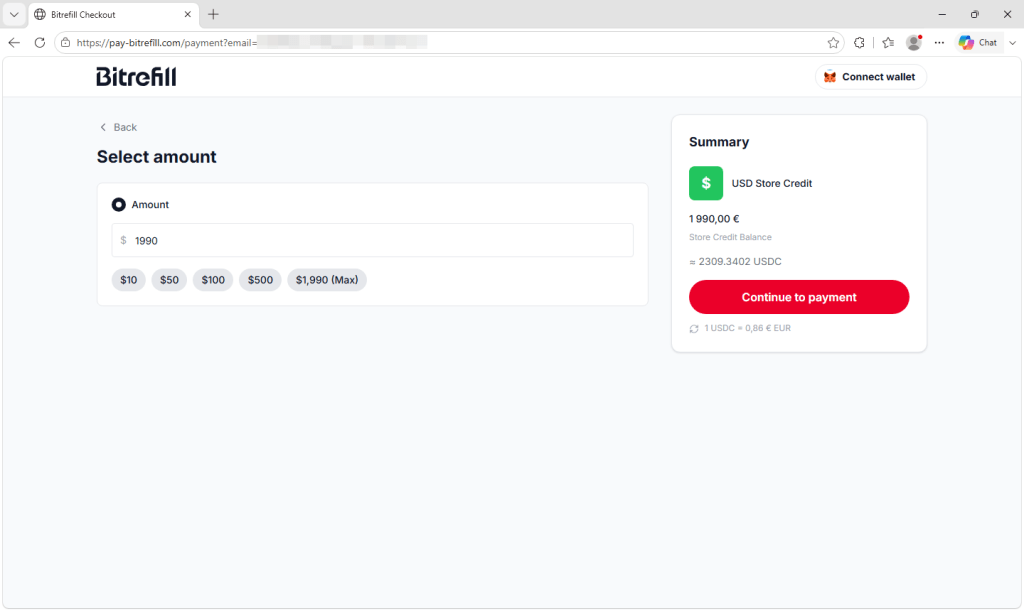
Next, you pick an amount, with preset buttons and a maximum of $1,990, although inconsistent currency symbols offer a small clue that something is wrong.
Finally, you reach a payment screen showing a QR code, an address marked for one-time use, the amount converted into your chosen cryptocurrency, and a countdown clock giving you just under an hour to send the funds.
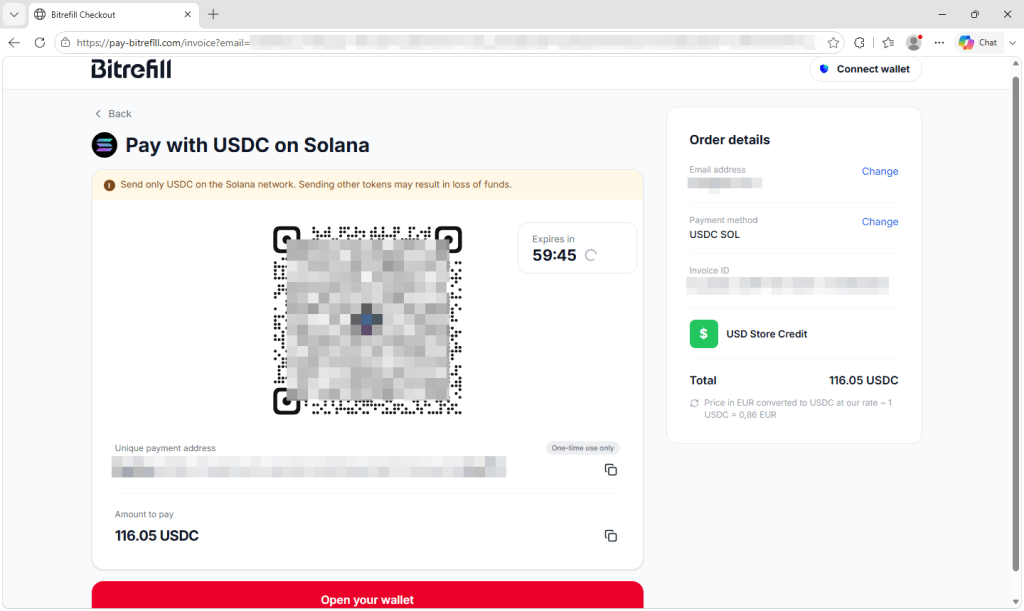
None of those elements is a red flag on its own. Unique addresses, expiry timers, and currency conversion are all normal for crypto checkouts, which is exactly why the copy is convincing. Every pressure cue on the page is borrowed from legitimate payment systems.
The only meaningful difference is the address the money goes to, and by the time the victim sends the cryptocurrency, getting it back is extremely unlikely.
How people are reaching these pages
The distribution here does not appear to rely on email. Bitrefill has said publicly that sites copying its checkout and using similar names have been turning up in search engine results, and that its security team has been working with takedown specialists to have them removed.
The site’s configuration supports that. The fake checkout hands visitors back to a second domain in the same family, and the link it uses carries a parameter naming a search engine, suggesting the operators are tagging incoming traffic by where it came from.
There’s a detail here that deserves more attention than it usually gets. The fake checkout has commercial analytics software installed on it, the same kind of product a legitimate e-commerce team uses to measure how many visitors abandon a cart. Its presence suggests the operators want to measure and improve the number of visitors who complete a payment.
These campaigns are not opportunistic one-offs thrown together by someone hoping for a lucky hit. They’re run as businesses, measured and tuned like any other funnel, with the victim in the role of the customer.
A brand name is not a destination
The domains in this cluster use several tricks to make their addresses look convincing. Some swap one letter for a visually similar character, making the brand appear correct unless you look closely. Others add a plausible word such as pay or gift, producing addresses that resemble official payment sites. Some do both.
Several use internationalized domain names, which can contain characters from different alphabets or accented versions of Latin letters. Browsers translate these domains into an ASCII format beginning with xn--, known as Punycode. To the eye, the displayed versions can be almost indistinguishable from the genuine name.
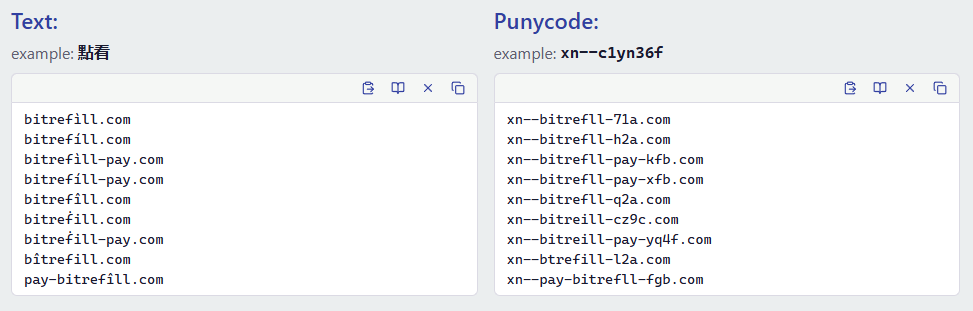
xn--.The answer is not simply to become better at spotting tiny differences. These domains are designed to defeat visual inspection, and they can be especially difficult to recognize on a phone screen. Recognizing a company name somewhere in a web address does not tell you who owns it.
Remember, seeing the right company name in a URL is not enough. Check that the actual domain is exactly the one the company uses.
What to do
- Start at the website you already trust. Use a saved bookmark or carefully enter
bitrefill.comyourself. If you are already making a purchase on the legitimate site, stay within that session instead of opening a checkout page from a separate search. - Treat search results for payment and checkout pages with suspicion. Scammers can buy search ads or manipulate their sites into appearing prominently. The first result is not necessarily the safest one.
- Check the address bar before you send. Cryptocurrency payments generally cannot be reversed or charged back. Confirm that the main domain is exactly
bitrefill.combefore approving a payment. - Be wary of domains containing a brand followed by an extra word. A legitimate subdomain would place the additional wording before the company’s main domain, as in
pay.example.com. An address such asexample-pay.comis a completely separate domain that anyone could register. - Don’t approve wallet requests on a site you have not verified. Simply connecting a wallet does not normally transfer funds, but a fraudulent site may ask you to sign a transaction or grant token permissions that allow assets to be stolen.
- If you have already sent funds, act quickly, although recovery is unlikely. Report the destination address to the exchange or wallet provider you used, report the incident to your national fraud reporting service, and notify Bitrefill so it can add the domain to its takedown efforts. Recovery services that promise to retrieve stolen cryptocurrency for an upfront fee are often follow-up scams.
Check before you click
The simplest protection against a page like this is to avoid reaching it. Malwarebytes Browser Guard is a free browser extension that blocks known scam and phishing sites, along with malicious ads and search results that lead to them.
Got a screenshot or URL of a suspected scam? Upload it to Scam Guard—built into Malwarebytes Premium Security on Windows, Mac, iOS, and Android—and you’ll get a verdict and safety tips in seconds.
Indicators of compromise (IOCs)
Domains:
biterflll[.]com
bitigift[.]com
bitrefall[.]com
bitrefill-payments[.]com
bitrefill-pays[.]com
bitregift[.]com
bitregill[.]com
bitretill[.]com
bitrgift[.]com
bitrgifts[.]com
bitrnfill[.]com
bitruflli[.]com
butrefill[.]com
pay-bitregill[.]com
pay-bitrgift[.]com
pay-bitrgifts[.]com
pay-butrefill[.]com
pay-bitigift[.]com
xn--bitrefll-71a[.]com
xn--bitrefll-h2a[.]com
xn--bitrefll-pay-kfb[.]com
xn--bitrefll-pay-xfb[.]com
xn--bitrefll-q2a[.]com
xn--bitreill-cz9c[.]com
xn--bitreill-pay-yq4f[.]com
xn--btrefill-l2a[.]com
xn--pay-bitrefll-fgb[.]com
Stop threats before they can do any harm.
Malwarebytes Browser Guard blocks phishing pages and malicious sites automatically. Free, one click to install. Add it to your browser →
About the author

Sr. Malware Research Engineer/Web Protection Technical Lead, ThreatLabs
Passionate about antivirus solutions, Stefan has been involved in malware testing and AV product QA from an early age. As part of the Malwarebytes team, Stefan is dedicated to protecting customers and ensuring their security.
Text extracted automatically; images, tables and formatting may be missing. Original: https://www.malwarebytes.com/blog/threat-intel/2026/09/search-results-are-sending-people-to-fake-bitrefill-checkouts