Russian-speaking hackers target Russian organizations with industrial spying tools
Full article775 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The discovery adds to a growing body of public reporting on corporate hacking that has often focused on Chinese-speaking hackers
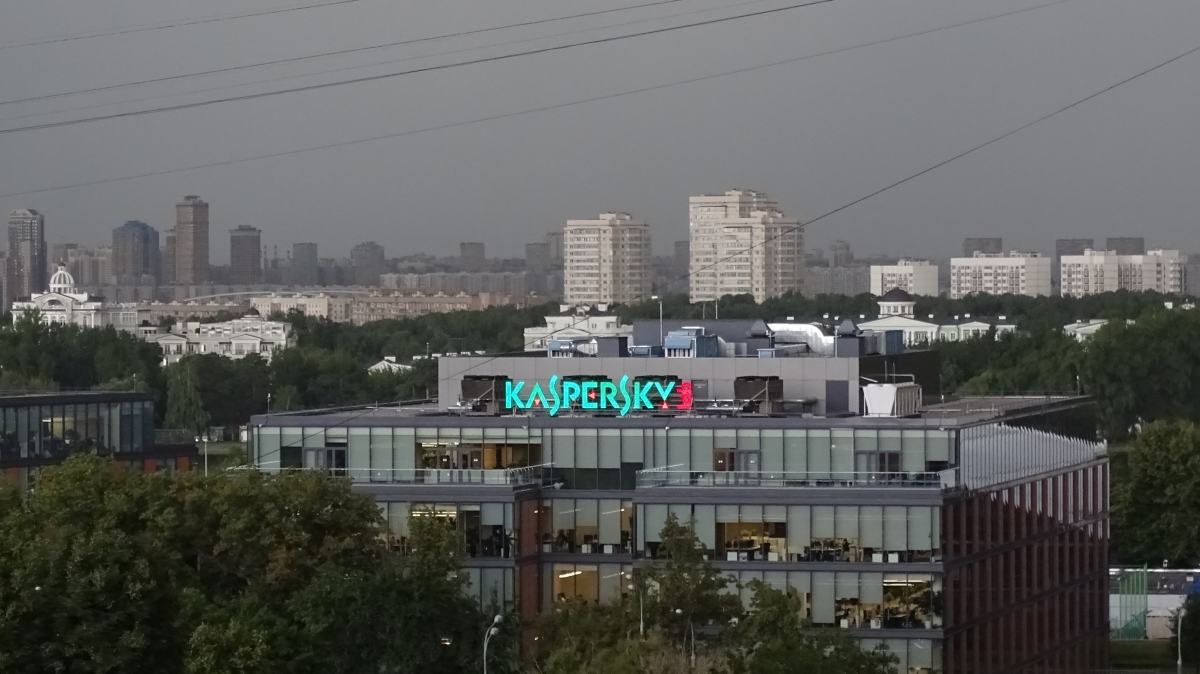
A previously undisclosed, Russian-speaking hacking group has for the last two years been conducting targeted espionage against Russian-speaking organizations, researchers said Thursday.
The type of tailored malicious code that Russian security company Kaspersky uncovered is often reserved for spying on diplomats or infiltrating telecom firms rather than corporations, researchers asserted. But these attackers have been stalking unnamed corporations, looking to siphon off certain Microsoft Office and Adobe documents.
The discovery adds to a growing body of public reporting on corporate hacking that has often focused on Chinese-speaking hackers. U.S. government officials and security researchers have accused China of economic espionage for years — a charge Beijing denies.
In this case, however, the hackers may be pretending to be Chinese but are really Russian speakers, according to Kaspersky. They set up online accounts for communicating with cloud computing infrastructure that “pretend to be of Chinese origin,” the researchers said.
To try to ensnare their targets, the hackers have been sending messages to organizations purporting to contain internal administrative data or even medical testing results. In one case, they pretended to send testing results from Invitro, one of the biggest medical laboratories in Russia.
It’s not clear who is responsible for the cyber-activity or what companies have been targeted. The researchers did not point the finger at any government or criminal organization.
“To date we don’t observe any code or infrastructure similarities with known campaigns,” said Denis Legezo, senior security researcher at Kaspersky. He declined to provide any details on the organizations targeted.
“The overall campaign sophistication doesn’t compare to top notch [advanced persistent threat] actors in terms of spreading [and] persistence method,” Legezo wrote in a blog post, using a term typically associated with state-linked hackers.
Whoever is behind the “MontysThree” malware, as the new tool is called, put a good deal of effort into disguising their code. They used an obfuscation technique called steganography to encrypt their data, according to the Kaspersky report. They also employed legitimate software, such as Internet Explorer and Citrix products, already installed on the target’s computer to hide their tracks.
The research is the second time in a week that a significant new hacking group has been exposed. On Oct. 2, analysts at another anti-virus company, ESET, revealed a long-running cyber-espionage campaign targeting governments in Eastern Europe.
More Scoops
Unusually patient suspected Russian hackers pose as State Department in ‘sophisticated’ attacks on researchers
They weren’t in any hurry, according to Citizen Lab, and used an interesting attack vector. Google Threat Intelligence Group also provided details on the attacks.
Ukrainian official: Russian hackers change tactics from disruptive attacks
Apple issues third mobile OS update after zero-click spyware campaign
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/russia-hacking-industrial-espionage-kaspersky/