Kaspersky Analyst Summit 2011
Full article345 words · extracted from securelist.com · click to collapse

Twice every year, analysts from Kaspersky meet for a couple of days to brainstorm over ongoing security issues, think about new ways to protect the users and fight against new breeds of threats.
The first summit for 2011 took place earlier in February, and brought together over 100 people from various departments inside the company. Although the exact subjects of the talks are secret as usual, the discussions revolved around subjects such as Android threats, targeted attacks, allowlisting and digital certificates.
One of the highlights of the meeting was having an external guest for an afternoon of a different kind of brainwork – the ancient game of chess. It was a great privilege to meet and talk to Grandmaster Anatoly Karpov, former World Chess Champion and one of the greatest chess players to have ever lived.
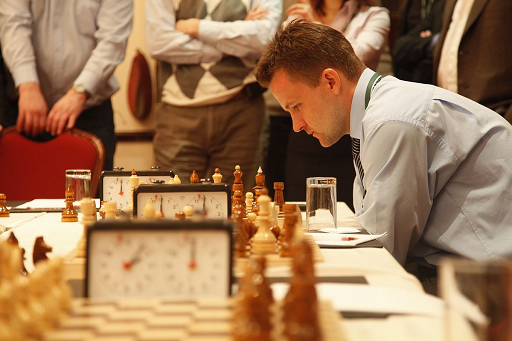
Mr Karpov was kind to play a simul against 10 chess players from Kaspersky Lab. All the games ended predictably with 1-0 (Mr Karpov played white at all the tables), except for the game with KL’s CTO Nikolay Grebennikov, who was agreed to a draw, after the black was in a winning position but blundered resulting in an equal endgame.
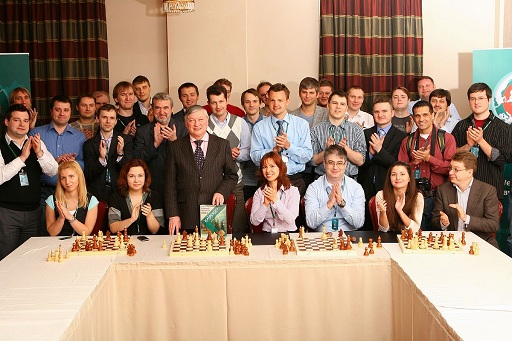
You can see GM Karpov in the picture above, with some of the KAS participants that you might recognize.
The next issue of KAS will take place in June, at a warmer, though undisclosed (for now) location.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/kaspersky-analyst-summit-2011/29833/