McAfee CEO 'cautiously optimistic' on companies' ability to handle GDPR
Full article681 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Christopher Young sees organizations working diligently to comply with the European rules, but there's only so much they can do ahead of the compliance deadline.
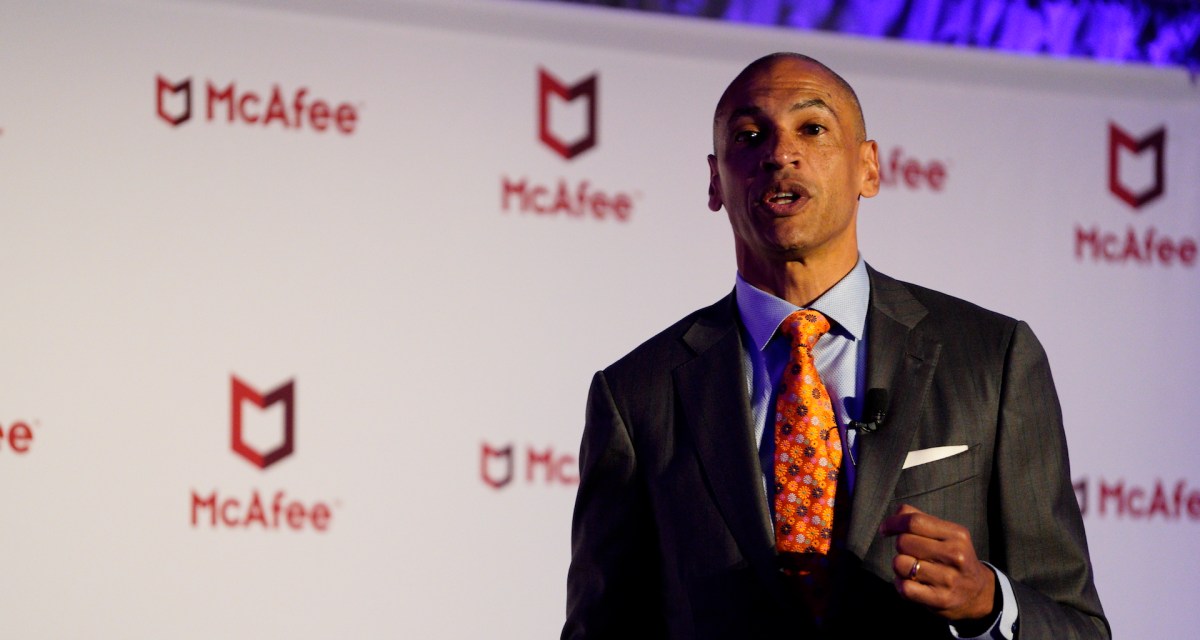
McAfee CEO Christopher Young says companies are “cautiously optimistic” about their ability to handle the European Union’s General Data Protection Regulation despite concerns about the law’s scope.
Young told CyberScoop he sees organizations working diligently to comply with the law, but there is only so much they can do ahead of the mandated compliance deadline.
“I would tell you that a lot of organizations are still trying to figure it out and are a little bit of wait-and-see mode to understand exactly how some of the aspects of GDPR take hold,” Young said on the sidelines of the Security Through Innovation Summit presented by McAfee and produced by CyberScoop and FedScoop.
The law, which goes into affect Friday, mandates much stricter controls on how data can be collected, analyzed and used. The EU considers the law a huge push toward strengthening citizen’s rights when it comes to data.
Young’s optimism is a rosier outlook than most. Numerous studies, polls and news reports have painted a picture of companies scrambling to comply with the law or run the risk of massive fines in the event of a violation.
Young believes the EU could stem a lot of the worry if they presented clarity how they will interpret the law moving forward.
“I view that the way to get clarity in these situations is paint use cases, give examples,” he said. “I think we are going to need more examples, more use cases, for people to understand. I think that the more those examples can be used, it creates a clearer picture for everyone.”
Some of the few examples out there do not paint a welcoming picture. Last month, the The Internet Corporation for Assigned Names and Numbers learned it would have to shut down its database of information tied to website ownership. The White House appealed to the EU on behalf of security researchers that use the database to scrape data. The EU deemed that practice to be illegal under GDPR.
More Scoops
Trellix, McAfee, FireEye, Mandiant: What’s next for four big names in cyber
With the arrival of Trellix, there was a lot of talk about integrating pieces of McAfee and FireEye. But in some ways, the move represents disintegration, too.
John McAfee found dead after Spanish court approved extradition to US
John McAfee arrested in Spain, charged with tax evasion
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/christopher-young-mcafee-gdpr/