Schneider Electric reports cyberattack, its third incident in 18 months
Full article590 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The ransomware group HellCat claims responsibility for the cyberattack and threatens to dump 40GB.
Listen to this article
0:00
Learn more.

Multinational energy management company Schneider Electric said Tuesday it was the victim of a cyberattack, with attackers behind a new ransomware variant claiming responsibility.
“Schneider Electric is investigating a cybersecurity incident involving unauthorized access to one of our internal project execution tracking platforms which is hosted within an isolated environment,” a spokesperson said in an emailed statement. “Our Global Incident Response team has been immediately mobilized to respond to the incident. Schneider Electric’s products and services remain unaffected.”
The company was a listed victim on the Hellcat ransomware variant’s leak site, with attackers demanding a $150,000 ransom in “baguettes,” an obtuse reference to the company’s headquarters being located in France. In reality, the attackers are looking for payment in Monero, a privacy-focused cryptocurrency.
HellCat claims to have more than 40 gigabytes of data from the company’s JIRA platform, “including projects, issues, and plugins, along with over 400,000 rows of user data.” Jira is a general application used for project management that could include sensitive or proprietary information about employees or major projects.
Attackers did not further describe what type of information was stolen.
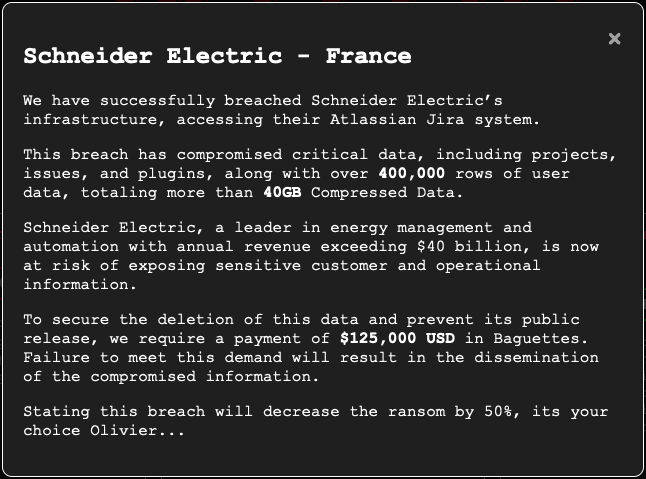
“To secure the deletion of this data and prevent its public release, we require a payment of $125,000 USD in Baguettes. Failure to meet this demand will result in the dissemination of the compromised information,” the note says, adding that “stating the breach” will decrease the ransom by half. “Its your choice Olivier…”
The message seemingly refers to new Schneider Electric Chief Executive Olivier Blum, who took over as CEO this week after Peter Herweck was ousted from the role.
HellCat has previously published records they claim to be from the Jordan Ministry of Education and Tanzania’s College of Business Education.
The incident marks the third time in the past 18 months that Schneider Electric has been attacked by ransomware groups. In January, the company’s sustainability business division was hit with Cactus ransomware. In June 2023, the company disclosed that it was targeted by Cl0p via the exploit used in the MoveIT breach.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/schneider-electric-energy-ransomware-hellcat/