Vietnamese hackers appear to be researching an NSA backdoor tool
Full article667 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Codenamed ODDJOB, the tool was originally leaked by Shadow Brokers, but it now appears to be drawing interest from the group known as OceanLotus.
A hacker group with suspected ties to the Vietnamese government appears to be researching a leaked National Security Agency tool codenamed ODDJOB, based on documents uploaded to the repository VirusTotal and tied to a source already identified as OceanLotus group, otherwise known as APT32.
A classified user manual for ODDJOB was originally published on April 14 by a mysterious group, known for sharing NSA documents, named the Shadow Brokers. A copy of this same document was then uploaded April 17 to VirusTotal along with other malicious email attachments by OceanLotus. Multiple U.S. cybersecurity firms say OceanLotus is aligned with the interests of the Vietnamese government.
The specific version of the manual uploaded by OceanLotus was not weaponized, meaning it didn’t carry malware that could be used to convert the harmless PDF to a phishing lure.
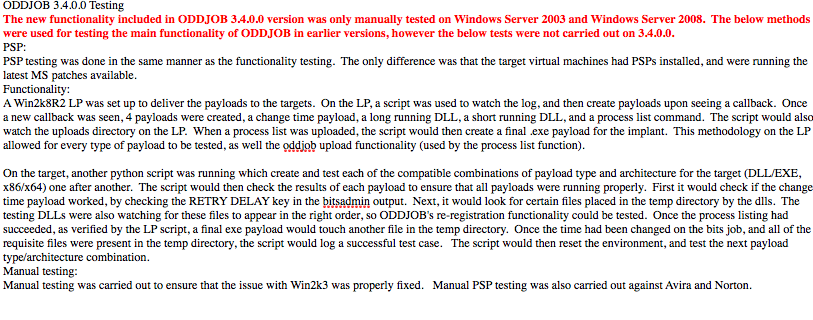
Screenshot of the mentioned document
ODDJOB is a high-quality, masterfully engineered digital weapon believed to have been once used to help U.S. spies collect intelligence stored on machines running older versions of Microsoft Windows. Details on this backdoor implant are scarce at the moment. The operational computer code behind ODDJOB was not released by the ShadowBrokers.
OceanLotus’ apparent interest in the ODDJOB manual underscores the efforts now being made by nation-backed hacking groups to better understand, and potentially reuse, leaked NSA capabilities — a fear perhaps already realized with the WannaCry ransomware campaign.
When ODDJOB is deployed against a target computer it attempts to obscure network traffic by appearing to be the Microsoft Background Intelligence Transfer Services, or BITS, which is typically used by Windows Update to apply a patch to a computer.
As of Thursday afternoon, the related file uploaded to VirusTotal remained in plain view.
The manual was first made public by the Shadow Brokers in April, but interest in this document by nation-states was previously unreported.
CyberScoop first reported Wednesday that OceanLotus was likely behind a cyber-espionage operation aimed at the Philippines government; a campaign which similarly saw sensitive documents be uploaded to VirusTotal. The reason for why these documents are being uploaded to a public forum remains unclear.
In addition to the ODDJOB manual, the aforementioned file dump includes, among other documents, an apparently leaked transcript of a phone conversation between U.S. President Donald Trump and Philippines President Rodrigo Duterte, briefing notes for a call between Philippine government officials and a U.S. senator, and internal documents tied to the Philippine National Security Council.
OceanLotus has been known to conduct missions against valuable corporations, foreign governments, dissidents and domestic journalists since at least 2014, according to research conducted by FireEye.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/vietnamese-hackers-appear-researching-nsa-backdoor-tool/