Brazilian Trojan Bankers
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| md5 | 00c79b15e024d1b32075e0114475f1e2 | e detect both apps as Trojan-Banker.AndroidOS.Binv.a (MD5s: 00C79B15E024D1B32075E0114475F1E2 and A18AC7C62C5EFD161039DB29BFDAA8EF) and we’re quite sure |
| md5 | a18ac7c62c5efd161039db29bfdaa8ef | ndroidOS.Binv.a (MD5s: 00C79B15E024D1B32075E0114475F1E2 and A18AC7C62C5EFD161039DB29BFDAA8EF) and we’re quite sure that these are only the first crude a |
Full article527 words · extracted from securelist.com · click to collapse


It took some time but they’re finally here – Brazilian cybercriminals have started to target their attacks towards mobile banking users. This week we spotted the first Trojan banker targeting Brazilian users of Android devices. Two malicious applications meant to pass for apps from local Banks were hosted on Google Play.
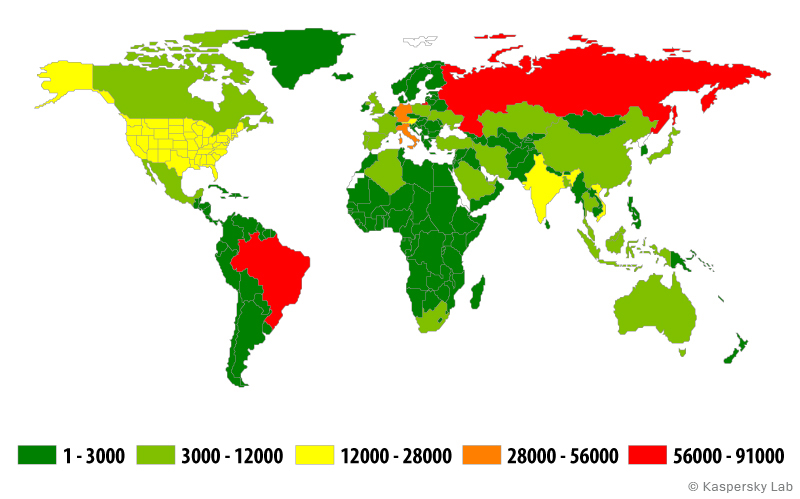
According FEBRABAN (the local Federation of Banks), more than 6 million Brazilians are using mobile banking regularly, so it’s not surprising to find malware targeting mobile users. In fact, Brazil was crowned the country most attacked by banking malware in our Q3 threat evolution report:
 This move by Brazilian bad guys was predictable and awaited as a natural development in the local malware scene. In 2012, we witnessed attacks using phishing pages in mobile format and now a bad guy using the name “Governo Federal” (Federal Government) was able to publish 2 malicious apps in the Play store:
Both apps used the name of two very popular public Brazilian Banks – the first app was published on October 31st and registered 80 installations. The second was published on November 10th and had only 1 installation.
To create the malicious app, the (lazy) bad guy decided to use “App Inventor”: a free platform that allows anyone to create their own mobile Android application, no technical knowledge required. The result is an app big in size and full of useless code. But both apps had the function to load the logos of the targeted Banks and open a frame – the phishing page programmed to capture the user’s credentials. Simple, but effective, as mobile banking users in Brazil still use single authentication, without tokens or OTPs, where only the account number and password are required.
The phishing pages of the targeted Banks were hosted on a hacked website. A good soul removed them and inserted an alert to the visitors stating: “Este é um aplicativo Falso, denuncie este app”, meaning “This is a fake app, please report it”. As a result, when the user downloads, installs and opens the fake banking app, this message is displayed inside, instead of the original phishing page:
We reported both apps to Google, and they promptly removed them from the Play Store. We detect both apps as Trojan-Banker.AndroidOS.Binv.a (MD5s: 00C79B15E024D1B32075E0114475F1E2 and A18AC7C62C5EFD161039DB29BFDAA8EF) and we’re quite sure that these are only the first crude attempts of many more to come.
Thanks to my colleague Roman Unucheck for the valuable help in this case.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/brazilian-trojan-bankers-now-on-your-android-play-store/67661/