Royal spam
Full article255 words · extracted from securelist.com · click to collapse



The wedding of Kate Middleton and Prince William is by far the most popular topic of conversation today. It’s virtually impossible to look at a newspaper or a blog without seeing some mention of the royal newlyweds. And now we are getting in on the act.
And it’s not because we here at Kaspersky Lab take a major interest in the private lives of the British royals. But spammers obviously do – take a look at the offer we received today:
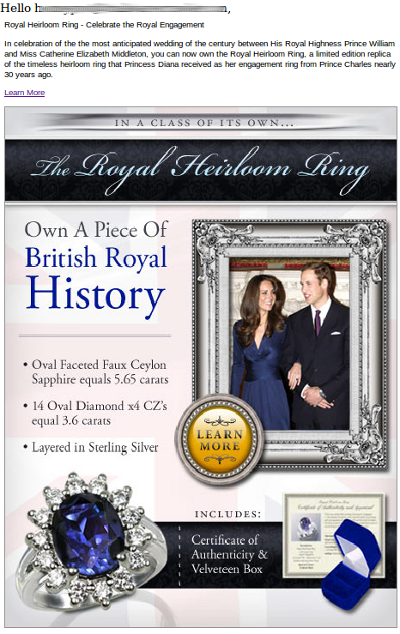
Yes, fake Swiss watches and iPads are so passé – what you need is a replica of Kate Middleton’s engagement ring, originally given to Lady Diana by William’s father Prince Charles. The spammers claim you now have the chance to “own a piece of British royal history”. This royal family heirloom also comes complete with a “certificate of authenticity”.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/royal-spam/29664/