DHS's diagnostics open door to collaboration inside agencies, says Commerce official
Full article680 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Having to implement new DHS network monitoring tools department-wide has started a conversation in many agencies about other shared services.
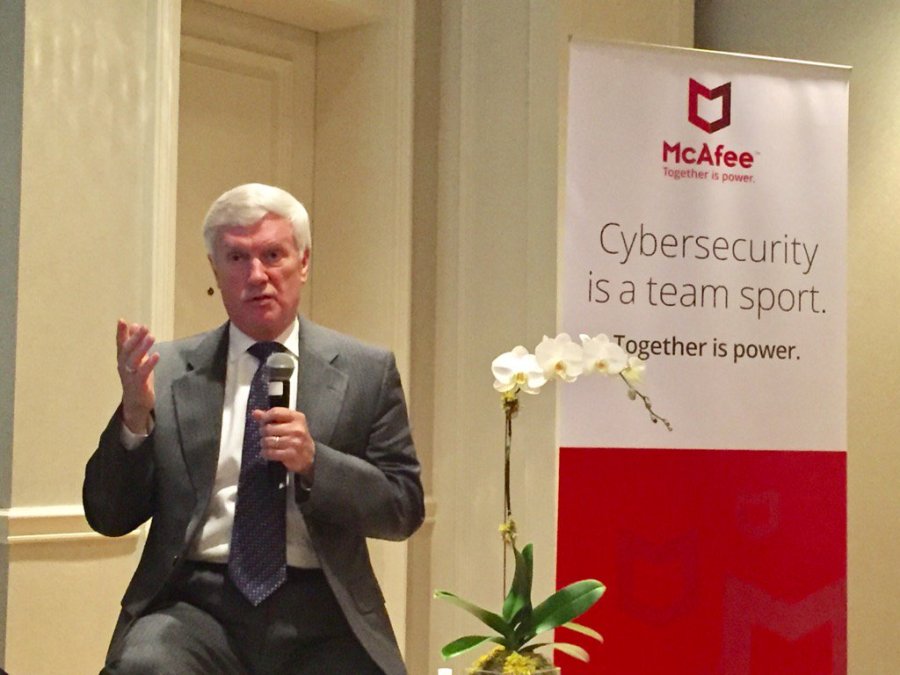
A funny thing happened when the CIO Council at the Department of Commerce sat down to figure out how to deploy the new tools coming from the Department of Homeland Security’s Continuous Diagnostics and Monitoring, or CDM, program.
Rod Turk, the department’s CISO and acting CIO, said people on the council — which brings together the CIOs from all the various agencies and bureaus that make up Commerce — started asking questions.
“Questions like, ‘Why do we have multiple Security Operation Centers and Network Operation Centers?’ … We have three SOCs just in [the Commerce headquarters building] … We had 73 separate pen-testing engagements … What can we do more efficiently when it relates to cybersecurity?” recalled Turk, who said he’s sat on the council for about eight years.
Turk spoke at a breakout session on CDM on Thursday at the 2017 McAfee Security Through Innovation Summit hosted by FedScoop and CyberScoop.
Under the governmentwide CDM program, DHS pays for cybersecurity tools and services that monitor the IT networks of U.S. federal agencies and departments. Phase one, which is currently being rolled out, collects data about all the hardware and software assets departments have connected, checks for vulnerabilities in the network and helps mangers configure their systems securely.
Turk said the cross-cutting functionality required by the deployment of the CDM tools helped get many other conversations started about ways the various parts of the department could bring their IT provisioning together, in what’s called shared services. It was a “significant culture shift,” he said.
“From a shared services point of view it’s kind of broken the ice to get us thinking about other things we could do collaboratively,” he said.
Shared services can drive budget efficiencies, but they can also improve outcomes, he said, adding it was not specifically intended as a cost-cutting exercise.
The department was folding its SOCs into a single operation, centered on the current SOC for the National Oceanic and Atmospheric Administration, based in West Virginia.
“They have 45 percent [of our network capacity] across the whole department so we are leveraging that,” he told CyberScoop afterwards.
On penetration testing, when white hat hackers-for-hire try to breach a network’s defenses, Turk said the department’s various bureaus and agencies between them had contracted for 73 separate engagements. “We want to collapse all that into one contract,” he said, “so we can view it from an enterprise-wide standpoint.”
The mandate for all federal departments to implement the CDM program has been especially challenging for those, like Commerce, that house a variety of bureaus and agencies.
“Some federated models work better than others,” is the kindest way to put it, said session moderator Hillary Palmer, McAfee’s enterprise account manager.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/cdm-commerce-dhs-shared-services/