The Pentagon's latest bug bounty target is its travel booking system
Full article641 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Because the Defense Travel System is used by millions of people and maintains sensitive information, hardening its security is a priority for DoD, organizers said.
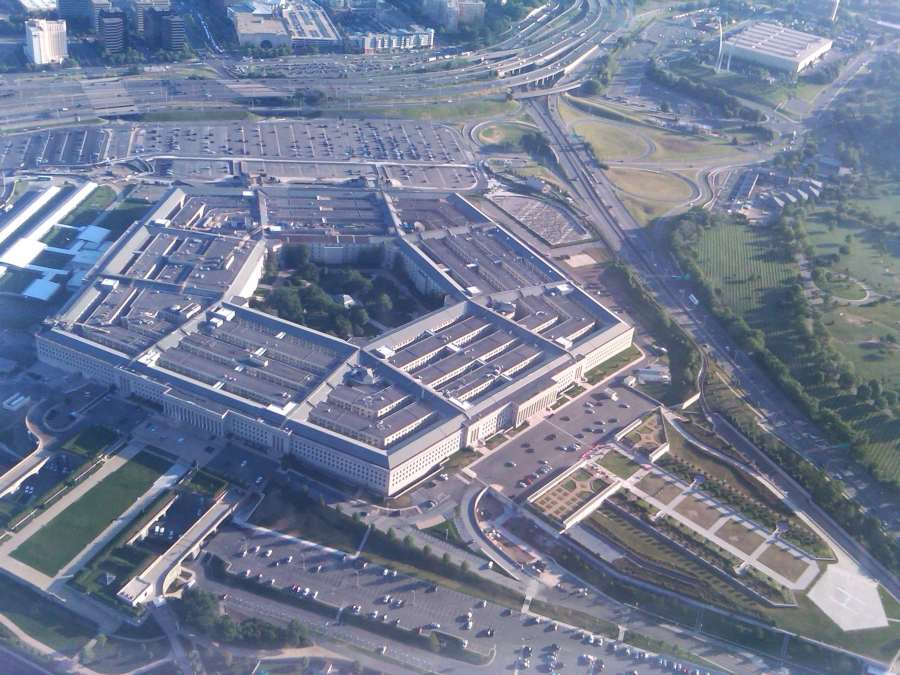
The Department of Defense’s attraction to bug bounty programs continues with a contest to find security flaws in its travel booking system.
The Pentagon is again pairing with HackerOne, a private company that has run similar programs for the Air Force, Army and the DoD at large, with hackers reporting hundreds of valid vulnerabilities and the Pentagon paying out hundreds of thousands of dollars.
The latest program is focused on the Defense Travel System (DTS), an enterprise system that DoD personnel use to book things like airline and hotel reservations when they travel for DoD business.
Because DTS is used by millions of people and maintains sensitive information, hardening its security is a priority for DoD, said Reina Staley, the chief of staff for the Defense Digital Service (DDS), which oversees the military’s bug bounty contests under the “Hack the Pentagon” program.
“The quick, positive reception of the [Hack the Pentagon] program has been a major win; inviting hackers to uncover vulnerabilities in DoD assets sounds counterintuitive to traditional government security practice, but the value of crowdsourcing external talent has been clear in every challenge we’ve run to date,” Staley told CyberScoop by email.
The Pentagon is essentially crowdsourcing the security of DTS from a pool of hackers recruited by HackerOne. Participants are probing DTS for vulnerabilities that could be exploited by adversaries. People who submit a valid vulnerability could win money. The program opened April 1 and will close April 29.
“The most security mature organizations look to others for help,” said Alex Rice, HackerOne’s co-founder and CTO, in a press release. “We’re excited to bring a fresh, mission-critical asset to the hacker community with the goal of protecting the sensitive government data it contains.”
Researchers have to apply to participate in the challenge, which is open to 600 participants. HackerOne will choose about 30 percent by lottery and the rest based on the company’s internal reputation system. That means the program is seeking experienced white hat hackers who are familiar with how a bug bounty program works.
HackerOne does not specify on the registration page the bounty ranges or what kind of security vulnerabilities are within the scope of the challenge. Government employees and active duty military personnel can also submit bugs, but can’t win any cash. Participants have to be citizens and residents of the U.S., United Kingdom, Canada, Australia or New Zealand — members of the so-called Five Eyes intelligence alliance.
Latest Podcasts
Government
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/pentagon-hackerone-hack-the-dts/