Senators revive bill to harmonize conflicting cybersecurity regulations
Full article570 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The legislation Sens. Gary Peters and James Lankford would create an executive branch panel to align federal cyber rules.
Listen to this article
0:00
Learn more.
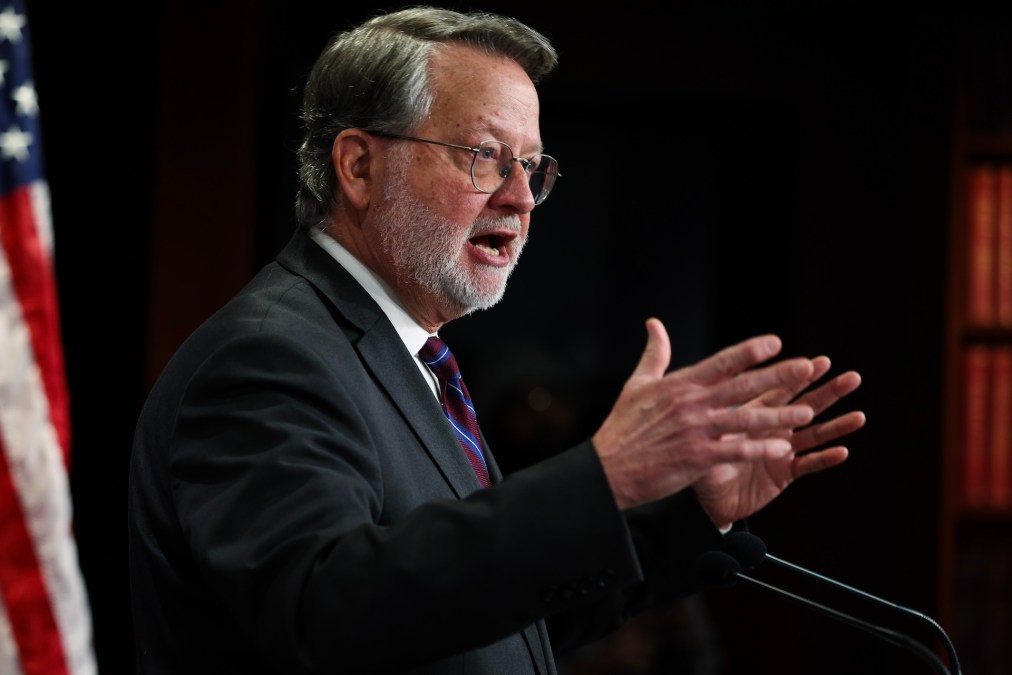
A bipartisan Senate duo is reintroducing legislation Thursday that would establish an executive branch panel to align conflicting cybersecurity regulations on the private sector.
Michigan Sen. Gary Peters, the top Democrat on the Homeland Security and Governmental Affairs Committee, is bringing back the Streamlining Federal Cybersecurity Regulations Act with co-sponsor James Lankford, R-Okla.
“By reducing the number of duplicative or burdensome reporting requirements, we can give businesses the tools to better secure our critical infrastructure against the serious threat of cyberattacks,” Peters said about the reintroduction of the bill, which CyberScoop is first reporting. “This legislation ensures federal agencies can work collaboratively to create effective cybersecurity standards, enabling businesses to focus on safeguarding their systems rather than navigating a maze of conflicting requirements.”
The Office of the National Cyber Director would lead the executive branch panel, with other members including the head of each regulatory agency; the heads of the Cybersecurity and Infrastructure and Security Agency and the National Institute of Standards and Technology; and the head of the Office of Information and Regulatory Affairs of the Office of Management and Budget. It would seek to harmonize any conflicting cyber rules, which proliferated under former President Joe Biden.
The legislation advanced out of the Homeland Security and Governmental Affairs Committee by a 10-1 vote last year, with support from industry groups and the Biden administration. The senator who now chairs the panel, Rand Paul, R-Ky., voted against it, saying that the slate of bills the committee voted on that day would add to the federal budget.
“Bureaucratic red tape shouldn’t get in the way of preventing a cyber-attack, but complicated regulations are making it more difficult to address the major cyber threats facing our national security and critical infrastructure,” Lankford said. “Harmonizing these efforts will make sure that federal requirements are focused on actually improving security instead of imposing a convoluted set of compliance challenges.”
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/senators-revive-bill-to-harmonize-conflicting-cybersecurity-regulations/