Fiesta parties on
Full article241 words · extracted from securelist.com · click to collapse


Over the last couple of weeks, we’ve been seeing new modifications of the PDF exploits spread and managed by the El Fiesta toolkit. Among other things, this nasty package targets unpatched Adobe and browser vulnerabilities to download more malicious code onto the victim machine.
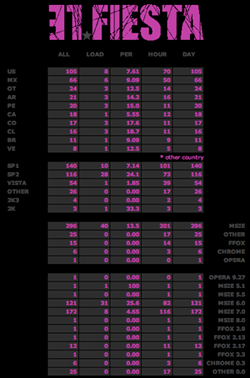
A ‘nice’ feature – for the bad guys, that is – is that Fiesta can be used not just to launch attacks, but to monitor them online. The screenshot below shows data on attacks which have been launched on machines around the world.
El Fiesta got a fair bit of publicity back in September this year. The fact that we’re seeing new variants shows there are still a good number of machines with unpatched software out there that malware writers want to get their hands on.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/fiesta-parties-on/30466/