Health insurer Excellus penalized $5.1M by HHS for data breach
Full article858 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The incident dates back to the era of well-publicized hacks on corporations such as Target, Sony and Home Depot.
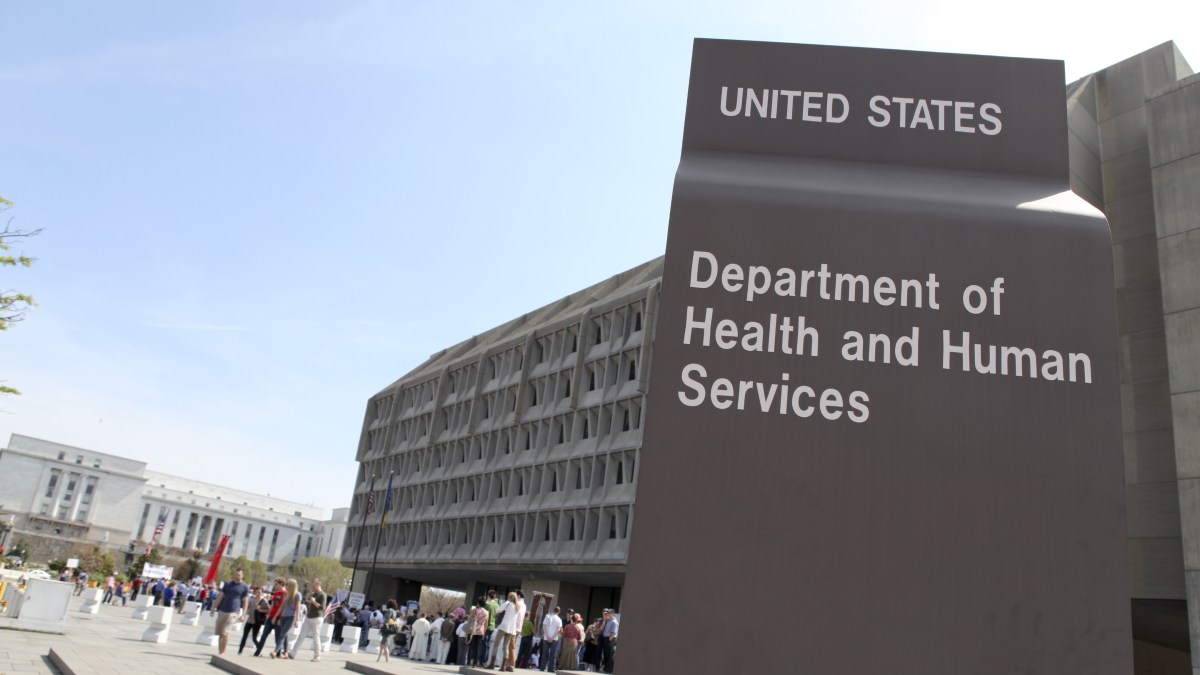
The Department of Health and Human Services says New York health insurer Excellus has agreed to pay a multimillion-dollar penalty after a data breach exposed sensitive information about more than 9 million people between late 2013 and May 2015.
The $5.1 million fine is for violations of privacy and security rules under the Health Insurance Portability and Accountability Act (HIPAA), according to the department’s Office for Civil Rights (OCR).
The incident stemmed from a hack against Excellus’ systems during an era that featured well-publicized attacks on corporations such as Target, Sony and Home Depot. Years later, health data remains a ripe target for cybercriminals, particularly ransomware gangs. U.S. federal agencies warned about an “imminent” ransomware threat in October 2020.
The OCR said the breached data included names, addresses, dates of birth, email addresses, Social Security numbers, bank account information, health plan claims and clinical treatment information.
“The hackers installed malware and conducted reconnaissance activities that ultimately resulted in the impermissible disclosure of the protected health information of more than 9.3 million individuals,” the office said.
The penalty will be paid by Rochester-based Lifetime Healthcare Companies, OCR said, which includes Excellus BlueCross BlueShield, Univera Healthcare and others. The not-for-profit holding company provides health insurance coverage to more than 1.5 million people in Upstate and Western New York.
The penalty from the federal government comes as Excellus continues to fight a class action lawsuit from victims of the incident. In that case, Excellus has tried to argue that it’s impossible to say whether data from the breach was actually put to illicit use. Courts have generally rejected the idea that plaintiffs in such lawsuits must directly link data misuse to the breach in question.
The civil suit, still active in the U.S. District Court for the Western District of New York “alleges that the companies failed to protect customer information, waited too long to tell customers about the breach and did not give customers adequate information about how to protect themselves in the wake of the breach,” according to a website for the lawyers representing the plaintiffs.
OCR said the HIPAA violations included a “failure to conduct an enterprise-wide risk analysis, and failures to implement risk management, information system activity review, and access controls.” In addition to the $5.1 million penalty, Excellus will “undertake a corrective action plan that includes two years of monitoring,” OCR said.
OCR Director Roger Severino used the case as an opportunity to remind health care companies of their vulnerability to criminal hacking.
“We know that the most dangerous hackers are sophisticated, patient, and persistent,” Severino said. “Health care entities need to step up their game to protect the privacy of people’s health information from this growing threat.”
Excellus’ penalty is one of the larger fines paid to OCR for data breaches. Last year Premera Blue Cross was assessed $6.85 million for a 2014 breach. The insurer Anthem paid $16 million in 2018 for its massive breach in late 2014. OCR penalties often come in addition to other legal actions, including suits from state attorneys general. Anthem, for instance, paid $39.5 million directly to states.
More Scoops
Bipartisan health care cybersecurity legislation returns to address a cornucopia of issues
The bill, first introduced late last year, deals with regulations, training, grants and more.
How HHS has strengthened cybersecurity of hospitals and health care systems
Stronger cyber protections in health care targeted in new Senate bill
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/excellus-data-breach-fined-hhs-ocr/