DNC hackers using NATO cyber conference to find phishing targets, researchers say
Full article735 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
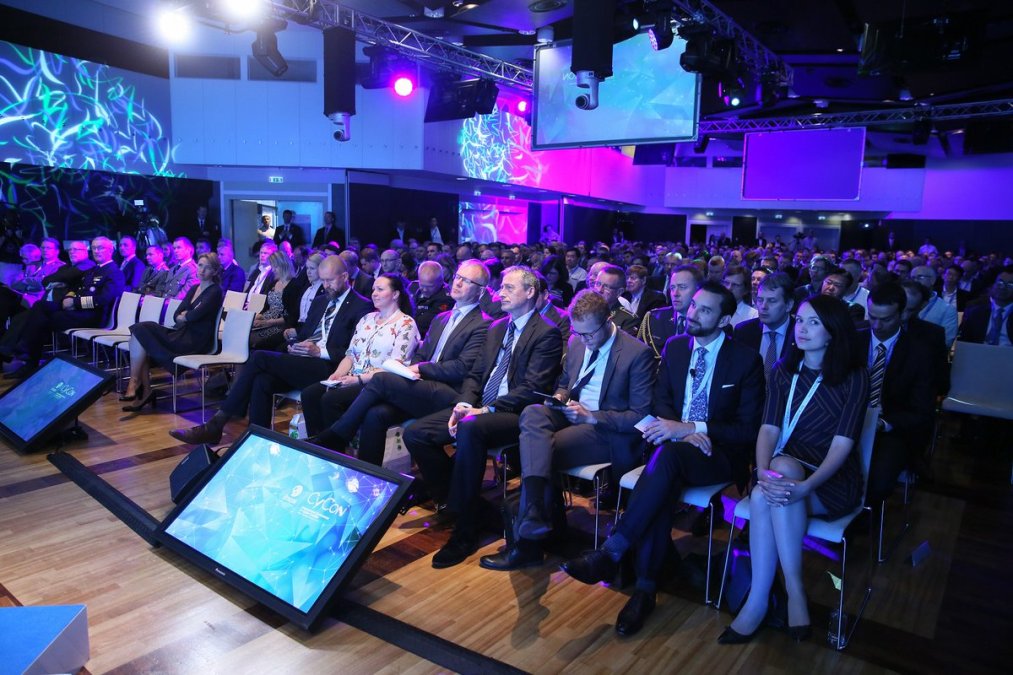
According to Cisco's Talos research team, Fancy Bear was sending phishing emails to people looking to attend CyCon.
There is evidence showing that the same infamous hacking group responsible for last year’s breach at the Democratic National Committee has attempted to spy on people interested in an upcoming D.C.-based cybersecurity conference, according to Cisco’s Talos research team.
In a blog post published Sunday, Talos noted that Group 74 — otherwise known as APT28 or Fancy Bear — recently sent a wave of spearphishing emails carrying malware-laden Microsoft Word attachments. These malicious emails contained information regarding a conference known as CyCon scheduled for early November.
The event is produced by the U.S. Army Cyber Institute in collaboration with NATO. The conference often features top leaders from both the U.S. government and other allied nations who help guide cybersecurity-relevant policies and missions.
“This attack is another example of sophisticated social engineering undertaken by the bad guys in order to trick their intended victims into opening malicious files. The entire spectrum of threat actors, from the least to the most sophisticated, are all trying to entice users to click that link or open that document,” said Cisco Talos Threat Researcher Martin Lee. “Users need to be suspicious of any unexpected document or invitation that they may receive, no matter how legitimate it may seem.”
Attendees of the CyCon conference in the past have included journalists, prominent politicians, defense ministers, NATO officials, former NSA executives and private sector cybersecurity leaders. Naturally, a significant portion of these conference-goers handle sensitive material or regularly communicate with others who do so.
“We assume that the targeted people are linked or interested by the cybersecurity landscape,” the Talos blog post reads.
It’s not clear exactly how or why APT28 targeted individuals broadly interested in this event.
“We have no information regarding the number or profile of the recipients,” Lee said.
APT28 has become synonymous with the Kremlin’s intelligence apparatus.
Talos noted in their research that the booby-trapped documents used by APT28 in this case contained no exploits. Rather, the attackers relied simply on a malicious Visual Basic for Applications (VBA) macro to trick users into connecting to a remote server where the hackers could have planted malware.
It’s possible APT28 decided to use low quality capabilities before resorting on other, more expensive and elaborate tools, which if outed could be a significant loss.
While this specific intrusion technique is relatively well known within the cybersecurity community, it appears as if APT28 made several configuration adjustments based on publicly available security research to avoid detection, according to Cisco.
“Threat actors are constantly seeking methods to improve the effectiveness of their attacks. This attack is part of the long history of threat actors of all types seeking to make their attacks appear legitimate and enticing to their intended victims,” said Lee. “Security teams must expect threat actors to use any and all information available to them, and to perform in-depth research in order improve the effectiveness of attacks. Well resourced, advanced threat actors are typically adept at researching their intended targets and crafting effective social engineering as part of their attacks.”
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Jail time for Maine child in 764 marks turning point in federal law enforcement
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/fancy-bear-cycon-spear-phishing-cisco-talos/