Senators press Treasury to speak about breach, planned response to hackers
Full article974 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Sens. Sherrod Brown and Ron Wyden want details on the reported Treasury breach and whether it will issue sanctions.
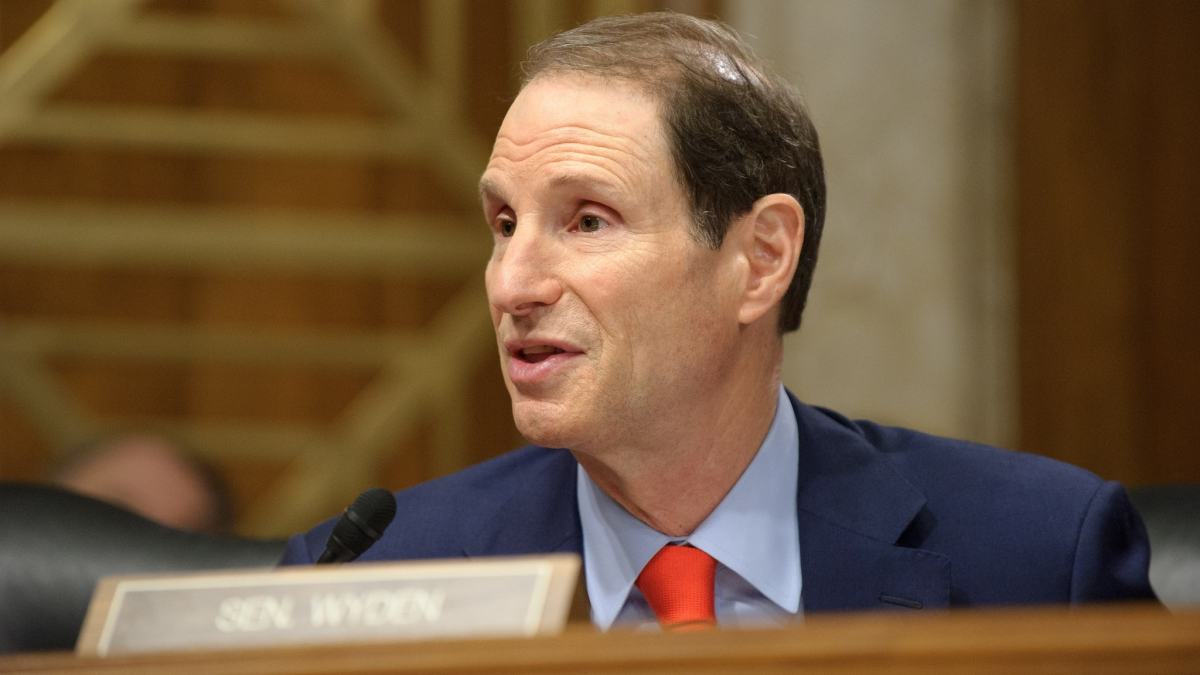
Two key Senate Democrats extensively questioned the U.S. Treasury Department on Tuesday about its reported data breach, a subject it has been less forthcoming about than the other federal agencies swept into the compromise of SolarWinds software.
The senators, Sherrod Brown of Ohio and Ron Wyden of Oregon, also want to know whether Treasury plans to sanction the attackers and if it has begun evaluating the overall damage to the economy of the cyber-espionage campaign, which could ripple through the private sector, too.
The senators’ letter to Treasury Secretary Steven Mnuchin pushes the department not only to provide information about its own breach, but also to develop a broader response that includes punishments for the hackers responsible. Cybersecurity researchers have tied them to Russia.
“These media reports suggest that these attacks were comprehensive and historic and bad actors may have had access to critical U.S. government networks for many months,” wrote Brown, the top Democrat on the Banking, Housing and Urban Affairs Committee, and Wyden, the top Democrat on the Finance Committee, who said they harbored “deep concern” about the incidents.
So far, Treasury has said nothing publicly about its breach. It has only referred requests for comment back to the White House’s National Security Council, which said over the weekend that it was aware of the reported breaches and that “we are taking all necessary steps to identify and remedy any possible issues related to this situation.”
Some agencies, such as the Commerce Department, have confirmed they were breached, although they have given few details. Others who were reportedly compromised have given partial statements, such as the Department of Defense, which said it “is aware of the reports and is currently assessing the impact.”
Multiple news outlets have reported that the breach at Treasury is likely the result of the SolarWinds software vulnerability.
The Senate duo wants Treasury to provide a list of which of its divisions, networks and services were affected, with an emphasis on whether hackers accessed any classified information in Treasury’s intelligence office. Brown and Wyden want to know when the department discovered the breach and provide details on how it responded, including when it sought help from other security agencies like the FBI.
They asked whether the breach was related to a vulnerability implanted in SolarWinds software, the subject of an emergency directive over the weekend from the Department of Homeland Security’s Cybersecurity and Infrastructure Security Agency (CISA) — and whether Treasury has complied with that directive.
Lawmakers had questions about those other agencies Tuesday, as well. Leaders of the Senate Commerce, Science and Transportation Committee, alongside leaders of the Senate Appropriations subcommittee responsible for the annual Commerce-Justice-Science spending bill, sent their own set of questions to the heads of the FBI and CISA.
Their queries spanned a wider range of victims than those of Wyden and and Brown. “The possible implications reach far beyond the specific federal agency jurisdiction of the Committees,” they wrote.
The bipartisan leaders of the two Commerce-related panels asked CISA to identify every federal agency that reported it was a customer of SolarWinds, and to describe what kinds and volumes of information might have been susceptible to unauthorized access. They also asked how CISA and the FBI were coordinating their investigations into to agency breaches and whether those agencies failed to comply with federal information security rules, as well as how CISA and the FBI were aiding private sector customers of SolarWinds.
Nor are those senators who lobbed questions at agencies on Tuesday the only members of Congress who have taken an interest in the agency breaches and SolarWinds in recent days.
Jackson Barnett contributed to this story.
More Scoops
Rep. Delia Ramirez takes over as top House cybersecurity Dem
She replaces Rep. Eric Swalwell following his resignation, giving her the position of ranking member of the Subcommittee on Cybersecurity and Infrastructure Protection.
Four Senate Democrats call on DHS to reinstate Cyber Safety Review Board membership
Exclusive: Peters, Rounds tee up bill to renew expiring cyber threat information sharing law
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/treasury-breach-solarwinds-wyden-brown/