European raid targeted notorious ransomware gang DoppelPaymer
Full article621 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
The DoppelPaymer ransomware gang is considered one of the world's most dangerous after it was linked to the death at a hospital in Germany.
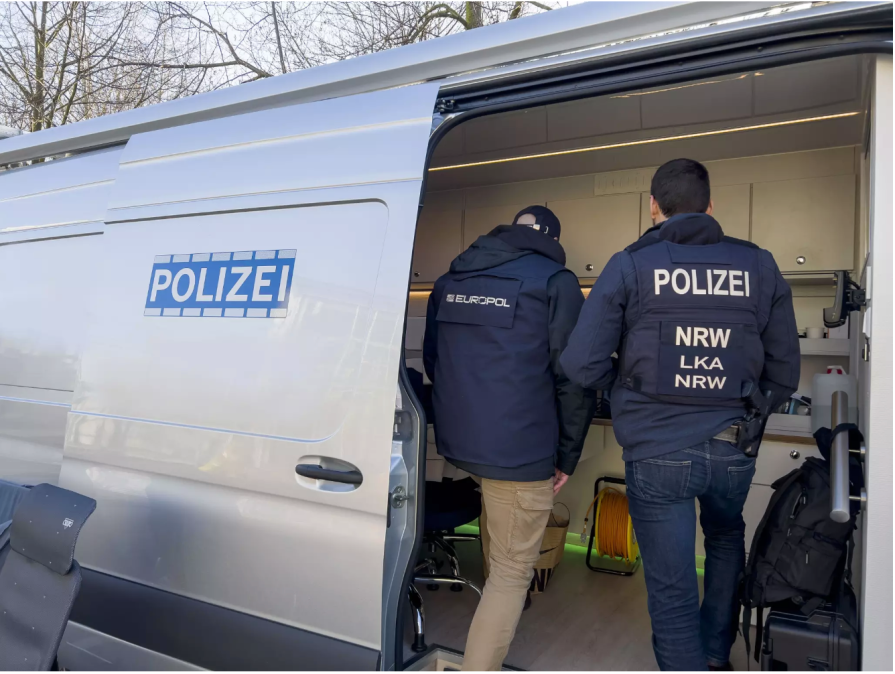
In the latest blow to international ransomware operators, police raided the homes of members of the notorious DoppelPaymer gang, seizing computer equipment and interrogating suspected members of the group believed to be responsible for extorting at least $42 million from victims in the U.S.
The DoppelPaymer ransomware, blamed for hundreds attacks globally, is also linked to the death of a patient at the University Hospital in Düsseldorf in Germany after hackers infected the hospital’s computer systems with malware — an incident believed to be the first death directly caused by ransomware.
The joint operation in late February involved police in Germany, Ukraine and the Netherlands, along with Europol and the FBI, according to a release issued Monday by Europol. “The individuals were interrogated, while electronic equipment was seized and is currently being analysed. Further investigative activities are on-going,” a Europol spokesperson told CyberScoop.
The raid follows a push by the White House to intensify efforts to take down ransomware operations, including by increasing cooperation with law enforcement agencies abroad. In one such high-profile operation, the FBI took down the infrastructure that the Hive ransomware group, one of the world’s most prolific cybercrime syndicates, used to carry out operations globally.
In the operation against DoppelPaymer, Euopol said police in Germany raided the home of a German national who they believe is a key player in the ransomware operation. “Investigators are currently analysing the seized equipment to determine the suspect’s exact role in the structure of the ransomware group.” Additionally, Ukrainian police “interrogated a Ukrainian national who is also believed to be a member of the core DoppelPaymer group. The Ukrainian officers searched two locations, one in Kiev and one in Kharkiv. During the searches, they seized electronic equipment, which is currently under forensic examination.”
According to Europol, the DoppelPaymer ransomware began surfacing in 2019 and targeted various organizations, including critical infrastructure operators. “The criminal group behind this ransomware relied on a double extortion scheme, using a leak website launched by the criminal actors in early 2020. German authorities are aware of 37 victims of this ransomware group, all of them companies.”
The FBI did not immediately respond to a request for comment.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
FCC proposes public scorecard to rate telecoms on anti-robocall efforts
Technology
Threats
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/doppelpaymer-ransomware-gang-europol-raid/