What's lurking in federal mobile tech? Apps, devices could hold nasty surprises.
Full article860 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
When federal agencies have for the first time to include mobile devices and apps in their information security reporting for FY2018 starting this October, they may be in for a nasty surprise, if the experience of the Department of Homeland Security is anything to go by.
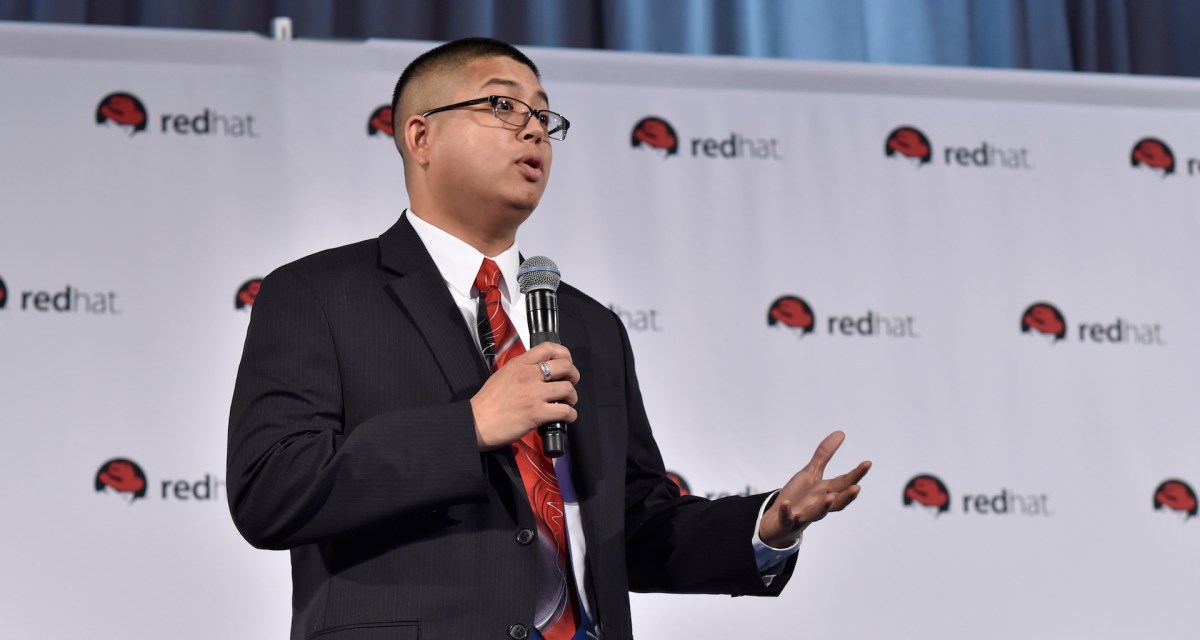
A discovery by Department of Homeland Security techs shows that federal agencies could get some nasty surprises as they prepare for a new reporting mandate assessing the security of their mobile devices and apps.
When security specialists from the DHS Science and Technology Directorate’s mobile security research and development team scanned the MyTSA mobile app, they found hard-coded credentials, program manager Vincent Sritapan said Thursday at the Red Hat Government Symposium presented by FedScoop.
“What does this mean? This means … you are exposing the backend,” Sritapan said, referring to the fact that, in many applications, credentials erroneously hard-coded into the software can be a backdoor into the data that apps collect and to their cloud-based functionality.
The MyTSA app is designed to let airline passengers get crowdsourced or historical data about wait-times at airport security checkpoints. It includes a searchable database of items that can and can’t go in checked or carry-on bags. It’s unclear how much or what data was potentially exposed by the blunder — a well-known type of coding error comparable to the Eavesdropper vulnerability reported this week.
“It’s already been fixed,” Sritapan said of the potential exposure, but noted that it was found “after the fact, after the app had been built.”
Initially, Sritapan said, the Transportation Security Administration had rejected an offer from his team to scan MyTSA using a set of automated tools they had helped develop, but the TSA officials changed their minds.
For fiscal 2018, which started Oct. 1, agencies won’t have a choice. The Trump administration is requiring more reporting from agencies on their mobile technology under the Federal Information Security Modernization Act (FISMA).
Sritapan said a review his program conducted of mobile threats earlier in 2017 found a lot of security holes in federal mobile deployments.
“We have mobile apps across the board, everywhere, the question comes down to: What due diligence are we taking?” he asked, adding his team found there were standards aplenty available in the federal ecosystem, but none were compulsory.
“There’s lots of guidance out there … but none of it was really required,” he said.
Overburdened and under-resourced federal managers prioritize compulsory activities, Sritapan explained. “You have to make it a requirement,” he said, “Because you can tell CIOs all day long about the threat, but unless it’s a real requirement and it’s mandated, they don’t have the time and their budgets are limited.”
The DHS team’s review recommended, among other things, that Congress and the White House Office of Management and Budget add mobile deployments to agency reporting requirements under FISMA.
Sritapan took back-handed credit for creating the mandate for fiscal 2018.
“If you’ve never reported mobile assets, mobile devices and apps, before: Guess what? You’re going to be doing it this year coming up,” he told the audience of federal IT specialists and open-source software executives from the private sector.
“If you want to hate someone, hate me later,” he joked.
The FISMA reporting wouldn’t be enough, he said, “For us, the security requirements for mobile app development aren’t quite there yet.”
He pointed to an order issued by then-acting Defense CIO John Zangardi earlier this year, making National Information Assurance Partnership (NIAP) protection profiles a requirement for Pentagon systems.
Sritapan acknowledged that achieving a NIAP protection profile could cost $40,000-$60,000 and took two to three months. But he underlined that he expected it to be a continuing focus of Zangardi’s since his appointment by President Trump as DHS CIO last month.
“We’re expecting a real focus on mobile security” from the new CIO, he said.
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
The G7 tells industry to hurry up and prep for post-quantum encryption
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/sritipan-fisma-mobile-security-niap-protection-profiles-threats-requirements/