Google asks mobile security vendors to help keep hackers out of the Play Store
Full article761 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
In announcing the partnership, Google acknowledged that the current processes for reporting malicious apps “aren’t designed to scale.”
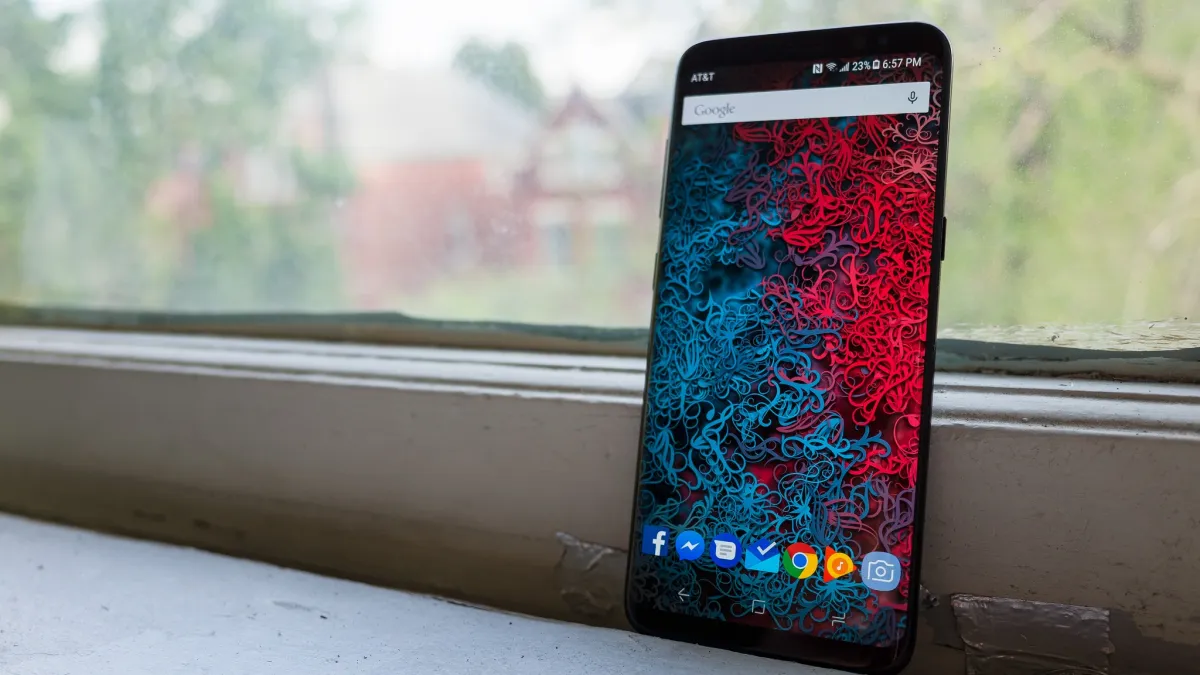
Google announced Wednesday it would work with multiple cybersecurity companies to better secure the Google Play Store, which hackers have repeatedly used to distribute malicious software.
Google’s decision to collaborate with ESET, Lookout, and Zimperium is an acknowledgement of the challenges of securing the Play Store and the countless devices that interact with it. Each company has distinguished itself by releasing research detailing how hackers are using mobile apps to spread nefarious code.
Google will integrate its Google Play malware detection systems with each of those companies’ anti-virus scanning engines. That will allow the companies to do an extra layer of vetting before an app appears in the Play Store.
In announcing the App Defense Alliance, as the partnership is known, Google acknowledged that the current processes for reporting malicious apps in and out of the Play Store “aren’t designed to scale.”
With over 2.5 billion Android devices in use, the scale of the security challenge is staggering. In 2017, security specialists removed roughly 700,000 malicious apps from the Play Store. In but one illustration of the issue, last January, cybersecurity company Trend Micro found spyware that had been downloaded over 100,000 times from the Play Store. The malware was capable of stealing call logs and SMS conversations from a target’s phone.
Apple has had to remove shady apps, too, but not nearly on the same scale as in the Play Store, where developers can more easily hide malicious functionality behind encrypted code or delay its activation.
“We hand-picked these partners based on their successes in finding potential threats and their dedication to improving the ecosystem,” Dave Kleidermacher, Google’s vice president of Android security and privacy, wrote in a blog.
Lookout said the alliance would help the company step up its work on mobile security.
“Even before this partnership, Lookout worked closely with Google to help them remove mobile app threats from the Google Play Store, such as ViperRAT, Desert Scorpion, and BeiTaAd,” Lookout said. “With the launch of the App Defense Alliance, Lookout will now be able to identify these sort[s] of malicious apps before they ever become a threat to the general public.”
More Scoops
Google and Amnesty International teamed up to make it harder for spyware vendors to hide
Intrusion Logging marks the first feature from a major device vendor to aid with forensic detection of sophisticated threats, Amnesty International said.
Court ruling in Epic-Google fight could have ‘catastrophic’ cyber consequences, former gov’t officials say
Rep. Garbarino: Ending CISA mobile app security program for feds sends ‘wrong signal’
Latest Podcasts
Government
FBI officials say AI is bolstering adversaries, emphasizing need to focus on cyber basics, patching
Feds accuse China of ‘systematic’ distillation of U.S. AI models
CIA’s Michael Ellis says cyber intelligence is changing how the agency operates
Jail time for Maine child in 764 marks turning point in federal law enforcement
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/google-asks-mobile-security-vendors-help-keep-hackers-play-store/