Beware – that social network app for your phone may be a Trojan!
Full article339 words · extracted from securelist.com · click to collapse



The features of malicious programs for mobile devices continue to expand: the first malicious program for mobile phones has been detected that steals logins and passwords for the Russian-language social networking site VKontakte.
Account credentials for various social networking sites are in high demand on the black market. That’s why criminals are trying to steal as many logins and passwords as possible using phishing pages and a variety of malicious programs. An example of this kind of malware is a new Trojan for mobile devices.
The malicious program Trojan-PSW.J2ME.Vkonpass.a is a 17 KB JAR archive called vkmob.jar which masks itself as an application for accessing the popular VKontakte site from a mobile phone.
If the application vkmobile (the name of the Trojan when installed on phones) is launched, the following will be displayed on the screen:
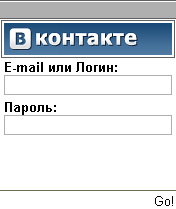
If the user enters his/her login and password and presses “Go!”, the Trojan will attempt to send the data via SMTP to the criminal’s e-mail. If the attempt is unsuccessful a “connection error” message is displayed; if the attempt is successful, “Error 401” appears on the screen.
Users need to be careful when using applications that pass themselves off as clients for various social networks, because in some cases those “clients” turn out to be malicious. Legitimate applications (if they exist) are usually available from the social networking sites themselves.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/beware-that-social-network-app-for-your-phone-may-be-a-trojan/29606/