Pentagon's websites need better security, Wyden says
Full article810 words · extracted from cyberscoop.com · click to collapse
Get our latest cybersecurity news first on Google.
Wyden warns that neglecting the security of public-facing DOD websites could embolden cybercriminals and state-backed hackers.
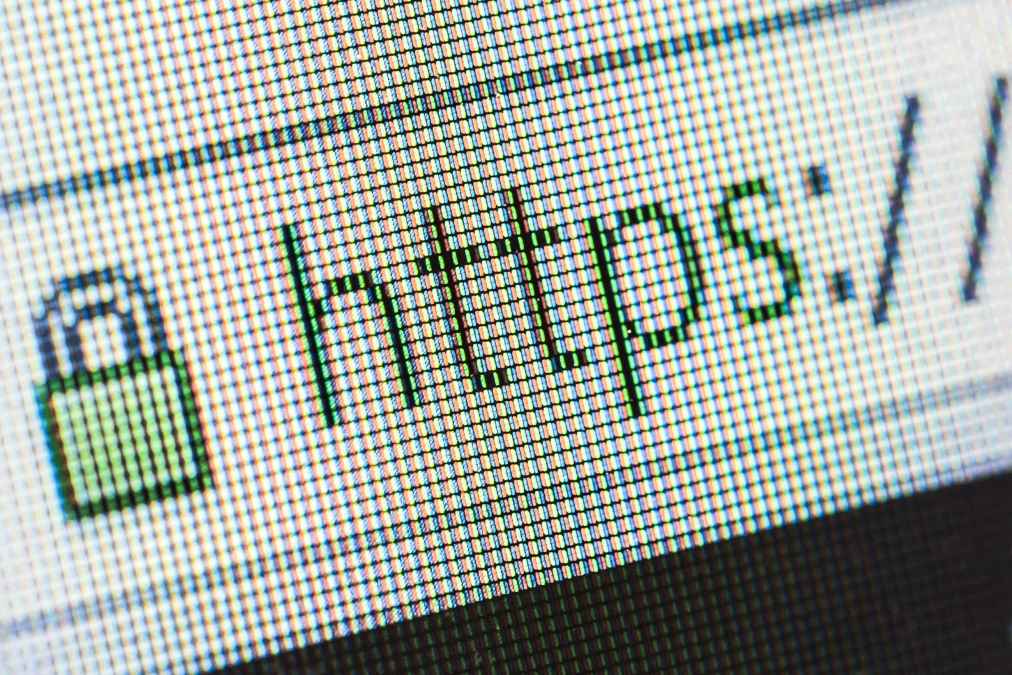
If you try visiting certain Department of Defense websites, like the one for Strategic Operations Command or the Navy’s Blue Angels, you might be met with a browser message telling you that your connection is not secure and that malicious actors could be trying to steal your information.
Sen. Ron Wyden, D-Ore., wants the Pentagon to fix this issue. In a letter written to DOD Chief Information Officer Dana Deasy on Tuesday, Wyden calls for the department to implement proper encryption and protection on all of its public-facing websites.
Wyden writes that a “small number” of DOD websites, such as the Army, Air Force and NSA homepages by default use trusted certificates and HTTPS encryption, the web protocol that ensures secure connections and prevents man-in-the-middle attacks. But many others, Wyden says, like the CIO’s own website, either don’t employ HTTPS or issue basic certificates.
“Many mainstream web browsers do not consider these DOD certificates trustworthy and issue scary security warnings that users are forced to navigate before accessing the website’s information,” Wyden writes. “These challenges do not only impact civilians; servicemembers accessing DOD pages from home regularly encounter security warnings and must click through such errors when accessing public DOD resources.”
The senator says that DOD is lagging on this issue. A 2015 memo from the Office of Management and Budget set a requirement that all websites only be available through HTTPS and HSTS by the end of 2016. HSTS is a policy whereby a website forces a browser to use the secure HTTPS protocol, and not the less secure HTTP. A 2017 Department of Homeland Security directive reiterated the OMB requirement.
Wyden says that the timing is critical for the Pentagon to secure its websites because, starting in July, the Google Chrome Browser will warn users that any HTTP connection is “not secure.”
“These warnings will erode the public’s trust in the Department and its ability to defend against sophisticated cyber threats. Moreover, the DoD’s refusal to implement cybersecurity best practices actively degrades the public’s security by teaching users to treat critical security warnings as irrelevant,” Wyden writes.
Ignoring the issue and “normalizing” these browser warnings could encourage cybercrime and nation-state hacking, Wyden says.
Wyden wants an “action plan” from Deasy by July 20. The senator urges Deasy to direct all Pentagon agencies and offices to implement the internet security orders from OMB and DHS. In addition to that, Wyden says DOD agencies and offices should deploy “certificates trusted by major web browsers” for all public-facing websites and services and assess the use of “shorter-lived, machine-generated certificates” that are often available for free.
A spokesperson for DOD said the department does not comment publicly on congressional correspondence and will respond to Wyden directly.
More Scoops
Sen. Wyden urges feds to discard older, insecure, public-facing VPNs
In a letter first reported by CyberScoop, Ron Wyden, D-Ore., said ‘devastating’ attacks on the federal government have accumulated due to the tech.
Wyden calls on FTC to investigate Microsoft for ‘gross cybersecurity negligence’ in protecting critical infrastructure
‘Russian state-sponsored cyber actors’ cited in hacks of U.S. defense contractors
Latest Podcasts
Government
Technology
Threats
Chinese espionage groups swarm to exploit triple-link chain of zero-days
Microsoft discloses two actively exploited zero-days among 974 vulnerabilities
Russian national extradited to US for alleged involvement in bank-account takeover scheme
Attackers exploit zero-days in consistently besieged SonicWall product
Policy
Whistleblower says USPS deploying new, ‘untested’ IT systems governing mail-in ballots
‘Watershed 250’ test program in Texas looks to private sector for water cybersecurity help
Former sexual abuse victims say Grok used their images, videos to train deepfake capabilities
Cyber threats nudge Trump to sign executive order on foreign equipment in U.S. energy infrastructure
Text extracted automatically; images, tables and formatting may be missing. Original: https://cyberscoop.com/wyden-pentagon-websites-not-secure-https/