And the winner is…
Full article343 words · extracted from securelist.com · click to collapse



It’s been a busy time in our spam lab. Sure, spam never goes away, but in May alone we’ve had spam linked to Mother’s Day
and spam linked to Victory Day, a major public holiday in Russia celebrating the end of World War II on 9th May. The message below is themed to fit the patriotic sentiments of the holiday, but the text at the bottom advertises printing services.
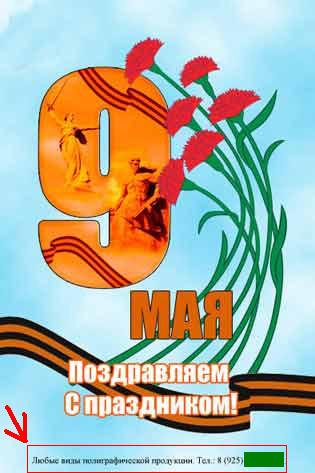
And now we’ve got a lot of Eurovision spam. Not surprising with the final looming. Tickets have been on sale on the Russian Internet since the middle of February, but this hasn’t stopped the spammers offering tickets which are one and a half, or sometimes twice, as expensive as tickets offered through official channels.
Of course, if you’re the one selling on a ticket, you’d be happy to get two or three times the face value. The problem is if you’re the buyer, and you pay over the odds for something that turns out to be a forgery.
There are lots of security features designed to distinguish genuine tickets from fakes, and funnily, some spammers are stressing this: the spam below (where the logo contains “noise” added by the spammers) ends the message by exhorting recipients to “Beware of fakes!”.
This is one of those rare cases when I, as a spam analyst, find myself agreeing with the spammers!
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/and-the-winner-is/30512/