World Cup 2010 has kicked off
Full article366 words · extracted from securelist.com · click to collapse



At last! What every football fan has been dreaming of. The start of World Cup 2010!
Even if you hate football, you just can’t help but know it’s World Cup time again, and one thing’s for sure, spammers will be doubly aware of it. It’s not that long since our last post dedicated to football-related spam. The Nigerian letters proclaiming lottery wins that we wrote about then have continued unabated – we have received lots of other messages all stating that the recipient has won millions of dollars in a FIFA competition.
One day before it all kicked off, a different kind of mailing appeared with the subject ‘FIFA World Cup South Africa… bad news’. The body of the message tells you to find out more about some “scandal news” that is contained in the attachment.
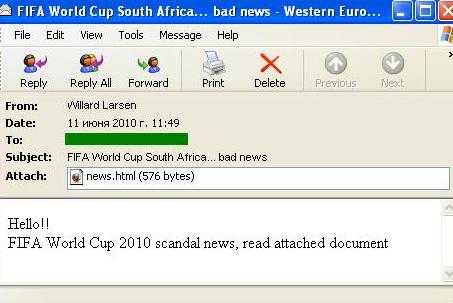
As you can see, the attachment is an HTML file. We’ve already written much about spammers hijacking the hottest news stories for the exclusive purposes of distributing malware and adverts for Viagra – in this case it is the latter. The HTML file redirects users to a Canadian pharmaceutical site.
The same domain used in the message above was also used in another recent large-scale mailing for Viagra – that mailing was disguised as a standard message from the Twitter social networking site:
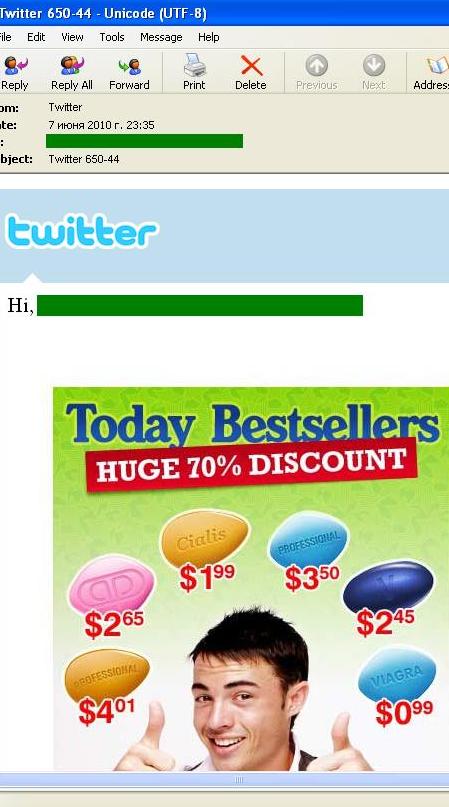
Now that the World Cup is underway spammers will no doubt continue to try and get in on the act by sending football-themed spam. Be careful. Enjoy the football. Don’t read spam!
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/world-cup-2010-has-kicked-off/29609/