Recapping the top stories from Black Hat and DEF CON
Vulnerabilities mentionedAll →
| CVE | Vulnerability | CVSS | EPSS | Flags | Affected | Exposure | Published |
|---|---|---|---|---|---|---|---|
| CVE-2022-40982 | Information exposure through microarchitectural state after transient execution in certain vector execution units for some Intel(R) Processors may allow an auth Information exposure through microarchitectural state after transient execution in certain vector execution units for some Intel(R) Processors may allow an authenticated user to potentially enable information disclosure via local access. NVD description · AI analysis pending | 6.5 | 3% | PoC ×2 |
| — |
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| md5 | 2915b3f8b703eb744fc54c81f4a9c67f | d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507 MD5: 2915b3f8b703eb744fc54c81f4a9c67f Typical Filename: VID001.exe Claimed Product: N/A Detection |
| md5 | 3e10a74a7613d1cae4b9749d7ec93515 | 40b49096e2f8f78d646891b45c649473a5b67b8beddac46ad398e1 MD5: 3e10a74a7613d1cae4b9749d7ec93515 Typical Filename: IMG001.exe Claimed Product: N/A Detection |
| md5 | 4c9a8e82a41a41323d941391767f63f7 | 1d4fe4344914e4d5c89747b838506090717f3fb749852b2d8109b6 MD5: 4c9a8e82a41a41323d941391767f63f7 Typical Filename: !!Mreader.exe Claimed Product: N/A Detect |
| md5 | 7bdbd180c081fa63ca94f9c22c457376 | 83227f5e7988d1ad9c0aecd66d58bb7b4d8518ae23e110308dbf91 MD5: 7bdbd180c081fa63ca94f9c22c457376 Typical Filename: c0dwjdi6a.dll Claimed Product: N/A Detect |
| md5 | d47fa115154927113b05bd3c8a308201 | cc1fc8e48e849ca9717c0700ef7ce2265511276f7015d7037d8725 MD5: d47fa115154927113b05bd3c8a308201 Typical Filename: mssqlsrv.exe Claimed Product: N/A Detecti |
| sha256 | 00ab15b194cc1fc8e48e849ca9717c0700ef7ce2265511276f7015d7037d8725 | t: N/A Detection Name: Win.Dropper.Coinminer::1201 SHA 256: 00ab15b194cc1fc8e48e849ca9717c0700ef7ce2265511276f7015d7037d8725 MD5: d47fa115154927113b05bd3c8a308201 Typical Filename: mss |
| sha256 | 1c25a55f121d4fe4344914e4d5c89747b838506090717f3fb749852b2d8109b6 | duct: N/A Detection Name: Win.Worm.Coinminer::1201 SHA 256: 1c25a55f121d4fe4344914e4d5c89747b838506090717f3fb749852b2d8109b6 MD5: 4c9a8e82a41a41323d941391767f63f7 Typical Filename: !!M |
| sha256 | 5616b94f1a40b49096e2f8f78d646891b45c649473a5b67b8beddac46ad398e1 | ware files from Talos telemetry over the past week SHA 256: 5616b94f1a40b49096e2f8f78d646891b45c649473a5b67b8beddac46ad398e1 MD5: 3e10a74a7613d1cae4b9749d7ec93515 Typical Filename: IMG |
| sha256 | 9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507 | uct: N/A Detection Name: Trojan.GenericKD.33515991 SHA 256: 9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507 MD5: 2915b3f8b703eb744fc54c81f4a9c67f Typical Filename: VID |
| sha256 | a31f222fc283227f5e7988d1ad9c0aecd66d58bb7b4d8518ae23e110308dbf91 | uct: N/A Detection Name: Trojan.GenericKD.65065311 SHA 256: a31f222fc283227f5e7988d1ad9c0aecd66d58bb7b4d8518ae23e110308dbf91 MD5: 7bdbd180c081fa63ca94f9c22c457376 Typical Filename: c0d |
Full article1,527 words · extracted from blog.talosintelligence.com · click to collapse
Thursday, August 17, 2023 14:00
Welcome to this week’s edition of the Threat Source newsletter.
I had a significant amount of FOMO last week seeing everyone out in Vegas. (I was happy to not get conference crud sickness, but it seems like I missed a great time otherwise.)
But, as anyone who works with me could guess, I was following closely online through social media and news reporting. If you’re in the same boat as me and couldn’t attend BlackHat or DEF CON in person, I wanted to use this space to recap what I felt were the top stories and headlines coming out of the various new research that was published, talks, interviews and more.
Unsurprisingly, it seems like AI was the talk of the town. One panel, which featured the former Cyber Czar in the Obama administration, promised coming action from the Biden administration around AI and its intersection with cybersecurity, including an executive order that apparently will be as broad as earlier orders around the U.S.’ broader approach to security.
There were many other panels and talks around AI, along with questions about whether the technology has plateaued after so many companies developed their own ChatGPT-like.
I was also fascinated by several interviews and talks from an FBI official about distributed denial-of-service attacks. I’ve written before about how there’s a renewed interest in DDoS attacks recently, especially those targeting high-profile companies and games.
Two high-ranking government officials gave a joint talk at Black Hat where they said the majority of DDoS attacks are the result of a dispute over business transactions or good ‘ol fashioned video game beef.
The same presenters gave additional details on how the FBI prioritizes stopping DDoS attacks. Chances are, if you’re a bad actor who makes the news for DDoS attacks, the federal government is not far behind.
I also always love the crazy vulnerabilities or hacking methods that come out of both these conferences. A highlight for me was a group of researchers who found a way to hijack one of the most popular automatic card shufflers (fitting for Vegas) to the point that someone could know the order of cards ahead of time in a gambling game.
I’m not quite sure what the actual attack surface is here because the potential hacker would need to install a tiny physical USB device into the shuffler, and I don’t think any casino worker would be thrilled to see you crawling around on the floor, but I do always love to see the downside of putting a USB port on everything.
And there was the brief, but confusing, saga at DEFCON about the pop-up notifications iPhone users were getting asking people to pair with a rogue Apple TV. Turns out it was a harmless prank from one of the attendees, who just wanted to drive home the point that it’s important to really turn off Bluetooth all the way, and not just click the little button in the Control Center.
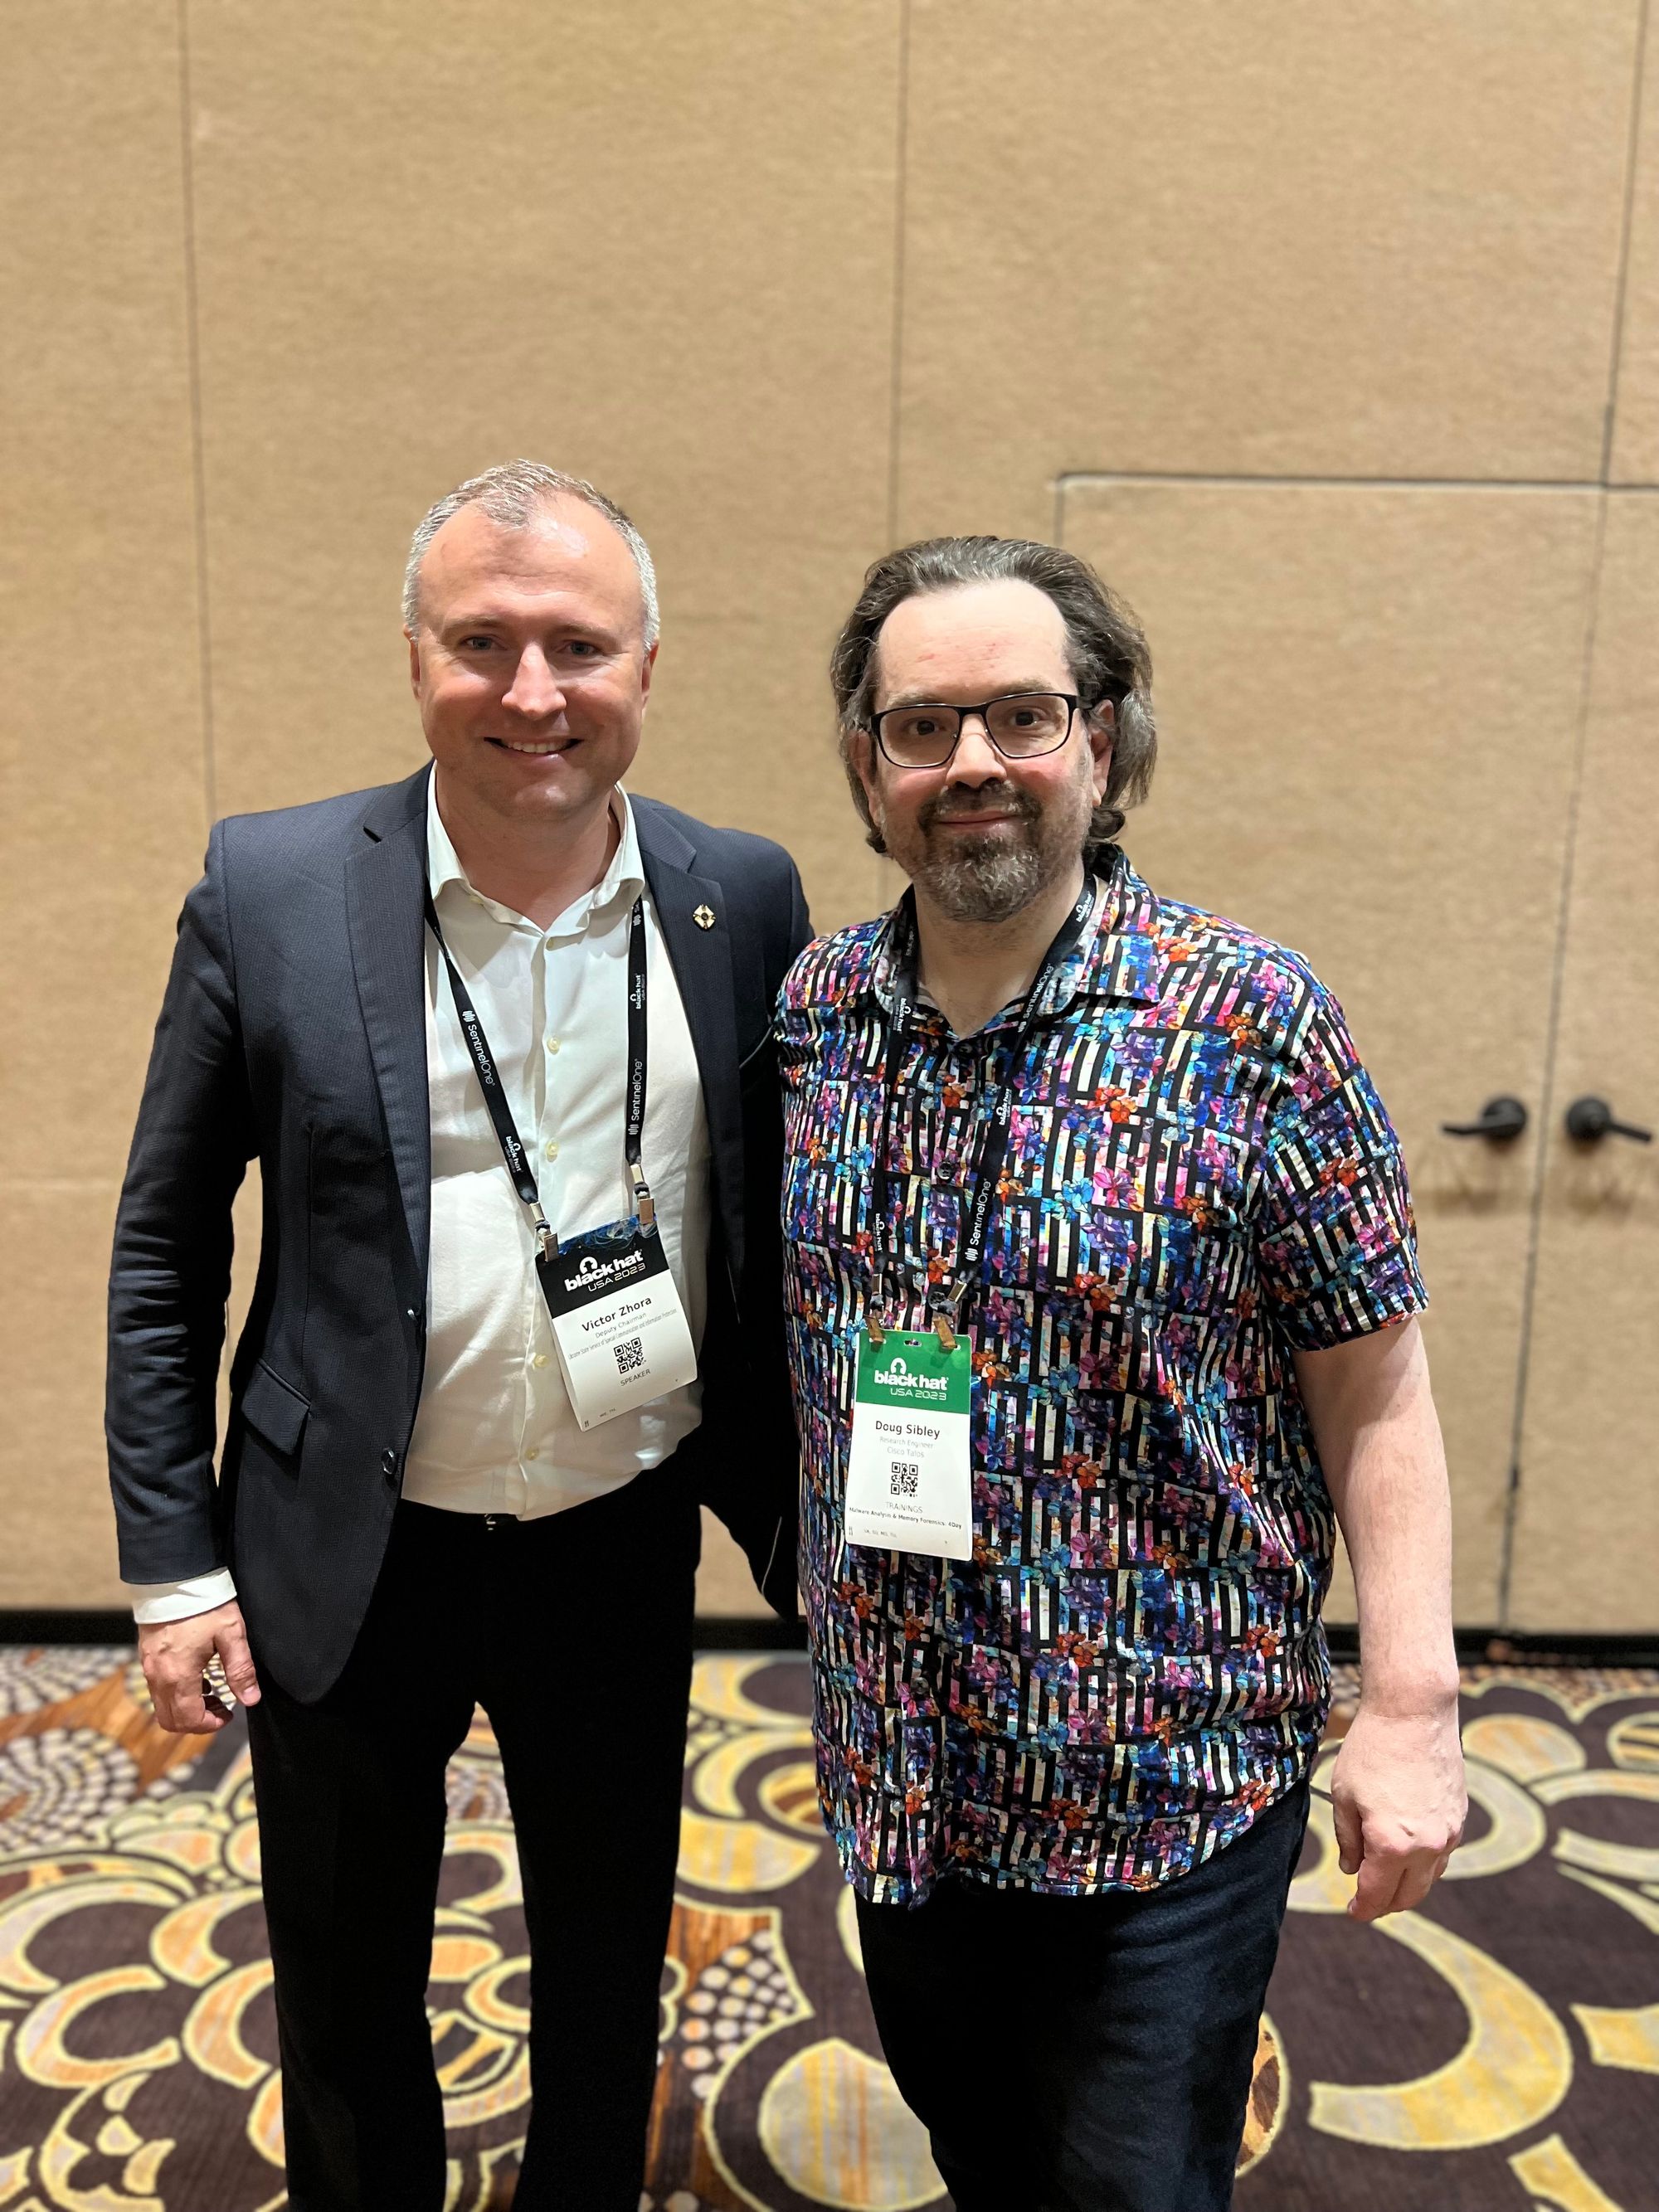
Lastly, we wanted to thank Viktor Zhora, the deputy chairman and chief digital transformation officer at the State Service of Special Communication and Information Protection for Ukraine, for taking the time to say “Hi” to us on the show floor. He specifically took time out of his day to make sure he could meet Matt Olney, who’s been one of our leaders in helping support Ukraine. Viktor was a speaker at BlackHat and had a very busy schedule of media appearances, so we were flattered that he made sure to see Matt.
The one big thing
Since AI was already the talk of the town at Black Hat and DEF CON, we wanted to continue the conversation around tehse tools and the implications on cybersecurity. As one of our incident responders wrote in the latest in our “On the Radar” series, AI’s influence is growing across the security space, bringing with it major implications for cybercriminals and defenders. The recent adoption of AI has raised significant concerns for cybersecurity due to the many ways that criminals can use AI for disruption and profit.
Why do I care?
AI can help streamline criminals' operations, making them more efficient, sophisticated, and scalable while allowing them to evade detection and attribution. AI presents another avenue for cybercriminals to exploit by utilizing it to analyze enormous amounts of information, including leaked data. This analysis empowers them to identify vulnerabilities or high-value targets, enabling more precise and effective attacks that could potentially yield greater financial gains. For defenders, though, AI also opens the door to new defensive tactics and tools, so it’s important to see the positives and negatives of AI in security.
So now what?
There is no real action for the average user to take at this point, but I feel this piece is a good opportunity for everyone to take a step back about what we currently know, and don’t know, about AI and its intersection with security.
Top security headlines of the week
Two police precincts in the U.K. had mistakenly been leaking the personal information of individuals connected to crimes for years. The UK's Norfolk and Suffolk police constabularies disclosed that, between April 2021 and March 2022, the information was accidentally attached to crime statistics distributed as part of Freedom of Information Act (FOIA) requests. The data includes personally identifiable information related to witnesses, suspects and victims of a variety of crimes, including domestic violence, assaults, thefts and hate crimes. The forces say they are now contacting more than 1,200 people who may have been affected. Representatives from the two departments said in a statement that, “Strenuous efforts have been made to determine if the data released has been accessed by anyone outside of policing. At this stage we have found nothing to suggest that this is the case.” (CSO Online, Politico)
Viktor Zhora, one of Ukraine’s top cybersecurity officials, said at Black Hat that his country is taking several steps to document what may constitute war crimes committed by Russian state-sponsored actors. Zhora said that attacks affecting critical infrastructure and communications for civilians could fall under such umbrellas and his team is actively collecting evidence as the kinetic military conflict continues. Speaking alongside Zhora, Jen Easterly, the U.S.’ top cybersecurity official, said the U.S. has learned several lessons from Russia’s invasion of Ukraine, including the importance of assistance from private cybersecurity companies. (CyberScoop, The Record)
Several years’ worth of Intel chips contains a newly discovered flaw known as “Downfall,” which is like the Meltdown and Spectre bugs from several years ago. Identified as CVE-2022-40982, the issue could allow the CPU to “unintentionally reveal internal hardware registers to software,” according to a write-up from Google’s security research team. Proof of concept code shows that an attacker could use Downfall to steal encryption keys from other users on a given server and other sensitive data. Downfall affects most CPUs in Intel's 6th through 11th-generation Core lineups for consumer PCs. Most of the affected devices were sold starting in 2015 and may still be available in systems today. Intel’s patch for the issue negatively affects the performance of the CPUs, with some studies finding that performance could dip to 40 percent. (Ars Technica, PC World)
Can’t get enough Talos?
- Cisco XDR: from detection and response to continuity after a cyberattack
- As Ransomware Gangs Shift To Data Extortion, Some Adopt A New Tactic: ‘Customer Service’
- Talos Takes Ep. #150: What's the difference between data theft extortion and ransomware?
Upcoming events where you can find Talos
Grace Hopper Celebration (Sept. 26 - 29)
Orlando, Florida
Caitlin Huey, Susan Paskey and Alexis Merritt present a "Level Up Lab" titled "Don’t Fail Knowledge Checks: Accelerating Incident Response with Threat Intelligence." Participate in several fast-paced activities that emphasize the importance of threat intelligence in security incident investigations. Attendees will act as incident responders investigating a simulated incident that unfolds throughout this session. Periodic checkpoints will include discussions that highlight how incident response and threat intelligence complement each other during an active security investigation.
ATT&CKcon 4.0 (Oct. 24 - 25)
McLean, Virginia
Nicole Hoffman and James Nutland discuss the MIRE ATT&CK framework in “One Leg to Stand on: Adventures in Adversary Tracking with ATT&CK.” Even though ATT&CK has become an industry standard for cyber threat intelligence reporting, all too often, techniques are thrown at the bottoms of reports and blogs without any context never to be seen again after dissemination. This is not useful for intelligence producers or consumers. In this presentation, Nicole and James will show analysts how to use ATT&CK as a guideline for creating a contextual knowledge base for adversary tracking.
Most prevalent malware files from Talos telemetry over the past week
SHA 256: 5616b94f1a40b49096e2f8f78d646891b45c649473a5b67b8beddac46ad398e1
MD5: 3e10a74a7613d1cae4b9749d7ec93515
Typical Filename: IMG001.exe
Claimed Product: N/A
Detection Name: Win.Dropper.Coinminer::1201
SHA 256: 00ab15b194cc1fc8e48e849ca9717c0700ef7ce2265511276f7015d7037d8725
MD5: d47fa115154927113b05bd3c8a308201
Typical Filename: mssqlsrv.exe
Claimed Product: N/A
Detection Name: Trojan.GenericKD.65065311
SHA 256: a31f222fc283227f5e7988d1ad9c0aecd66d58bb7b4d8518ae23e110308dbf91
MD5: 7bdbd180c081fa63ca94f9c22c457376
Typical Filename: c0dwjdi6a.dll
Claimed Product: N/A
Detection Name: Trojan.GenericKD.33515991
SHA 256: 9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507
MD5: 2915b3f8b703eb744fc54c81f4a9c67f
Typical Filename: VID001.exe
Claimed Product: N/A
Detection Name: Win.Worm.Coinminer::1201
SHA 256: 1c25a55f121d4fe4344914e4d5c89747b838506090717f3fb749852b2d8109b6
MD5: 4c9a8e82a41a41323d941391767f63f7
Typical Filename: !!Mreader.exe
Claimed Product: N/A
Detection Name: Win.Dropper.Generic::sheath
Text extracted automatically; images, tables and formatting may be missing. Original: https://blog.talosintelligence.com/threat-source-newsletter-aug-17-2023/