Insights from the 1st Ibero
Full article456 words · extracted from securelist.com · click to collapse
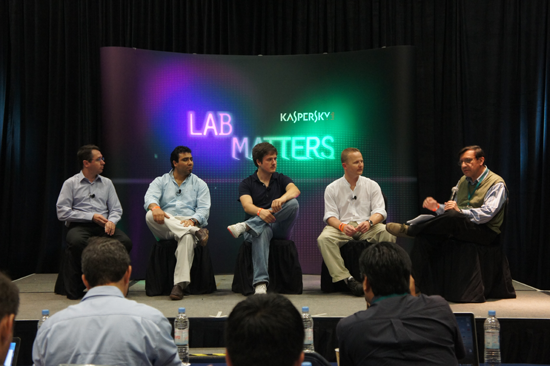

Last week, we held our first Ibero-American virus analyst summit, to which we invited 34 journalists from 14 Latin American countries, as well as Spain and Portugal. Speakers and panelists included antivirus experts Jorge Mieres, Fabio Assolini, Vicente Diaz and Dmitry Bestuzhev.
Our summit was held in the vicinity of Cancn in Mexico – a place that is famous for its beaches, resorts and ancient Mayan pyramids.
What did we discuss? Regional targeted APT attacks, which we believe may become a real threat within 5 years or less. Specifically, we talked about targeted APT ttacks in which one Ibero-American country attacks another country in the same region. Such attacks can be reasonably expected to take place as soon as three or four years from now.
Another issue discussed was that the number of attacks targeting financial data correlates with the economic situation in the country affected by the attacks. The economic crisis in Spain and Portugal led to a decrease in the number of such attacks, compared to the countries of Latin America.
Jorge Mieres demonstrated that many infection-related problems in the Ibero-American region are due to pirated unpatched software. What further aggravates the situation is that there is often a lack of policies and configurations aimed at improving the overall security situation.
Fabio Assolini presented detailed information on Brazilian malware writers and their annual earnings. Curiously, while malware writers in Europe and Asia prefer to remain in the shade and refrain from disclosing their identities, their Brazilian colleagues conduct PR campaigns in social networks and on YouTube.
Finally, Vicente Diaz presented examples that demonstrate how easily our online social life can be used for targeted attacks. He also talked about the threats which we are not yet aware of and which will nevertheless become real in the near future, such as on-board computer infections in cars and other vehicles.
We also recorded several webcasts in three languages: English, Spanish and Portuguese. They should become available to the general public soon. The event offered a plethora of interesting insights, and this is just the beginning!
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/insights-from-the-1st-ibero-american-summit/30677/