Tomorrow’s spam
Indicators of compromiseauto-extracted · verify before use · export allAll →
| Type | Indicator | Context |
|---|---|---|
| domain | geocities.com | pam and phishing 19 Nov 2009 minute read Maria Namestnikova Geocities.com has been gone for a month now, and you’d have thought the s |
Full article286 words · extracted from securelist.com · click to collapse



Geocities.com has been gone for a month now, and you’d have thought the spammers would be missing it. But one of the messages we got today shows that on the contrary, the spammers are looking forward to the future.
Here’s the message we got today – with tomorrow’s date on it. As most people configure their mail client to sort incoming messages by date, putting a future date on an email will ensure maximum visibility by putting it right at the top of the inbox.
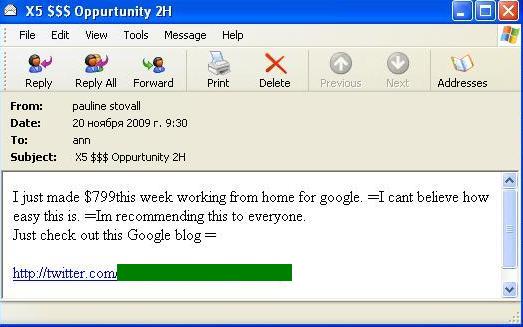
The links in these messages lead to new Twitter accounts:
Which in turn link to a site looking very like a news portal. But the only working links here reference making money by working from home.
The account shown above also has tweets with links to typical Viagra and weight loss sites. It’s clear that spammers may be moving with the times by changing the tools they use, but they haven’t changed their message. And why should they, as long as there’s profit to be made?
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/tomorrows-spam-today/30585/