Hack in The Box Security Conference 2011 Amsterdam / NL
Full article337 words · extracted from securelist.com · click to collapse



Since yesterday I’ve been attending the annual Hack-in-the-Box Quad-Track Security Conference in Amsterdam/NL. There’s a very nice and open atmosphere here at the conference, besides the beautiful city of Amsterdam.
First, Joe Sullivan (CSO at facebook), held a very interesting keynote about the development of security innovations at facebook. For him innovation is “these hacking culture, we think about each day at facebook”. After explaining some of the newer security innovations (https-only, login notifications, login approvals [if e.g. geo-location of a user is suspicious], recognized devices, recent activity) he talked about the recent fb-scams with malicious scripts. “No one would do that, copying and pasting a script into the browser! – Yes, they do…”, he said.
Also a remarkable talk I attended was about binary planting, given by Mitja Kolsek (CTO at ACROS Security). In “Binary Planting: First Overlooked, Then Downplayed, Now Ignored” Mitja also showed a new method he called “advanced binary planting”, which uses a feature from Windows’ special folders (like control panel, printers, etc.) and clickjacking to make it possible to own the users’ computer.
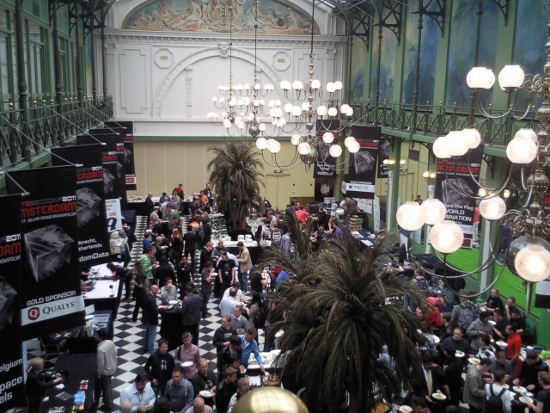
In the winter garden of the conference hotel there’s a technology showcase area. Hackerspaces from all over Europe and the Netherlands are showcasing their projects here. There also is a capture-the-flag competition happening, a lock-picking and (sponsor) companies-showcase.
For more informations please see the conference website.
Latest Webinars
Reports
Kaspersky researchers have discovered new Mirage Kitten attacks using previously undocumented malware families: NodeRabbit in Node.js and PollCat in JavaScript.
Our experts discovered a new CoolClient backdoor variant with a kernel-mode rootkit driver that hides malicious processes, files, and network connections from security tools and threat analysts.
Kaspersky experts break down a new Armored Likho campaign that poses as a fundraising efforts and delivers a new Still Toolkit aimed at stealing Telegram data and eavesdropping on victims.
Kaspersky researchers reveal previously undocumented malware attributed to Mirage Kitten (UNC1549, Smoke Sandstorm, Nimbus Manticore): NightLedger backdoor, ArcBridge, and BridgeHead tunneling tools.
Text extracted automatically; images, tables and formatting may be missing. Original: https://securelist.com/hack-in-the-box-security-conference-2011-amsterdam-nl/30830/